Just under 100 days separate us from 30 December 2026, the date the EU Deforestation Regulation starts to apply to large and medium operators and traders. Micro and small operators that are new to the rules have until 30 June 2027, although those already covered by the old EU Timber Regulation are in the December group.

After two postponements, this date looks firm. In its simplification review of May 2026 the European Commission confirmed that the regulation will not be reopened and that the existing timelines continue to apply. The July 2026 package then delivered the practical pieces teams had been waiting for: an updated product scope, a working information system, and guidance and FAQs in all EU languages.

Here is the encouraging part. Most of what EUDR asks for is supplier data, and collecting supplier data at scale is something procurement teams already know how to do. The teams that will be comfortable in December are not the ones with the best legal memo. They are the ones who started the data campaign early and kept the response rate high.

The short version

  • 30 December 2026 is the application date for large and medium operators and traders, plus micro and small operators previously covered by the EU Timber Regulation. 30 June 2027 applies to other micro and small operators.
  • Seven commodities are in scope: cattle, cocoa, coffee, oil palm, rubber, soya and wood, along with many derived products such as leather, chocolate, tyres, furniture and paper.
  • The core deliverable is a due diligence statement (DDS) submitted through the EU information system, which returns a reference number that travels down the chain.
  • Geolocation is the hard part. You need coordinates for every plot of land where the commodity was produced, plus evidence that production was legal in the country of origin.
  • Records are kept for five years, so this is a permanent data set, not a one-off filing.
  • Several simplifications genuinely reduce the workload, including one statement covering multiple shipments in defined cases, reuse of upstream reference numbers by downstream operators, and a group authorised representative.
  • Penalties are meaningful, with maximum fines of at least 4 percent of total annual EU-wide turnover, so this is worth doing properly.

What actually decides whether you are ready

Almost every EUDR article focuses on the legal obligations. That framing is useful for the general counsel and much less useful for the person who has to make it happen.

In practice, readiness comes down to one number: the share of your in-scope suppliers who have returned complete, usable data. A legal analysis can be finished in a week. Getting plot coordinates out of several hundred suppliers across multiple countries and languages takes months, because it depends on people outside your organisation finding time to answer you.

That reframing changes what you do first. Instead of starting with the regulation, start with the list of suppliers you need to hear from, and treat the next 14 weeks as a structured data campaign with owners, reminders and a visible completion rate. This is the same discipline as a good supplier onboarding programme, applied to a narrower question.

The data you need from suppliers

The regulation is specific about the information an operator has to collect and keep. For each in-scope product, that means:

  1. Product description, including HS code, trade name and the commodities it contains.
  2. Quantity, expressed in net mass and, where relevant, volume or number of units.
  3. Country of production, and for some chains the specific region.
  4. Geolocation of every plot of land where the commodity was produced. For cattle, this extends to every establishment where the animals were kept from birth to slaughter.
  5. Evidence of legal production under the laws of the country of origin, covering land use rights, environmental and forest rules, labour rights and tax and customs obligations.
  6. Supplier and customer details for products that already carry due diligence, including the reference numbers of the statements attached to them.

Two practical notes make this much easier to run. First, composite products need geolocation for each in-scope commodity they contain, so a chocolate bar with cocoa and palm oil generates two data trails rather than one. Second, the five-year retention requirement means this belongs in your permanent supplier master data, not in an inbox folder.

Where the simplifications genuinely help

The December 2025 revision and the 2026 packages removed real work. Four changes are worth building your plan around.

One statement can cover several shipments. Where the material comes from the same assessed harvest events and nothing in the supply chain has changed, a single due diligence statement can cover multiple shipments within a year. That turns a per-consignment task into a per-supply-chain task, which is a very different workload.

Downstream operators reuse reference numbers. Companies handling products for which due diligence has already been done collect and retain the upstream reference numbers rather than repeating the exercise. First-level downstream operators are not required to chase suppliers for those numbers either, since upstream operators provide them. If most of your volume is bought inside the EU from operators who have already filed, your job is largely to capture and store numbers reliably.

Groups can use one authorised representative. A single EU-established entity can submit statements on behalf of group members, which helps organisations with many legal entities. Legal responsibility still sits with each operator, so internal ownership still needs to be clear. If you run a multi-entity supply base, the same logic as multi-entity, multi-language onboarding applies here.

Country benchmarking reduces effort on low-risk origins. Where a commodity comes from a country classified as low risk, simplified due diligence applies and a full risk assessment is not required unless a substantiated concern arises. Knowing your origin mix early tells you where the real work sits.

Scope has narrowed in useful places. Printed products such as books and newspapers came out in December 2025. The July 2026 delegated act removed cattle hides and leather, retreaded tyres, soybeans for sowing, rubber articles, belts and vehicle seats, and added soluble coffee, certain palm oil derivatives and frozen cattle tongues, with the newly added products applying from 30 December 2027. Re-checking your HS codes against the current list is one of the highest-return hours you can spend this month.

A 14-week supplier data plan

Weeks 1 to 3: scope and segment

  1. Pull every purchased item against the current in-scope HS code list and confirm your own status as operator, trader or downstream actor. Scope errors are the most expensive mistake available, and they are cheap to fix now.
  2. Split in-scope suppliers into three groups: EU suppliers who will pass you a reference number, direct importers where you own the full due diligence, and suppliers whose status you cannot yet tell.
  3. Rank by volume and by origin risk. A simple risk-based segmentation tells you which twenty suppliers deserve a phone call rather than an email.

Weeks 4 to 7: launch the data request

  1. Build one request form per supplier group rather than one for everybody. A supplier passing you a reference number should not be asked for plot coordinates.
  2. Send it through a channel that tracks who has responded. A supplier portal with a visible completion status beats an email campaign, because you can see the gap rather than guess at it.
  3. Tell suppliers why you are asking and what happens if the data is late. Suppliers respond faster to a clear commercial consequence and a named contact than to a forwarded regulation.
  4. Set automated follow-up on a fixed cadence. Response rates rise sharply with the second and third reminder, and nobody has time to chase 300 suppliers by hand.

Weeks 8 to 11: assess, verify and close gaps

  1. Run risk assessment on what has arrived: check coordinates resolve to plausible plots, check legality evidence is current, and check the country classification you assumed.
  2. Escalate non-responders commercially. Category managers move data faster than compliance reminders do.
  3. For high-volume or high-risk origins, decide whether you need mitigation such as satellite checks, third-party verification or a remote supplier audit.
  4. Treat every missing or failed data point as a tracked action with an owner and a date, the same way you would handle a supplier corrective action.

Weeks 12 to 14: file and prove

  1. Register in the information system, dry-run a due diligence statement for one straightforward chain, and confirm the reference number flows to the people who need it.
  2. Decide which chains qualify for a single multi-shipment statement and document why, since that reasoning is what you will be asked about later.
  3. Make sure every decision, document and reference number sits in a reporting and audit trail that someone can navigate in minutes, with retention set to five years.

If you finish the first two blocks and are still collecting in week 12, that is normal. The value of starting now is that the gap is visible while there is still time to close it.

The data is worth more than the filing

It is tempting to treat this as a compliance cost. The more useful view is that you are about to build something your organisation has wanted for years: a verified map of where your material actually comes from, down to the plot.

That map answers questions well beyond deforestation. It tells you your true origin concentration, which is a supply continuity question. It feeds CSRD and CSDDD reporting rather than duplicating it, since much of the same evidence is requested twice under different names. It gives customers a credible answer when they flow their own requirements down to you. And it supports the wider supplier ESG picture you are already being asked for.

Teams that build this once, in a structured system, spend the following years maintaining it. Teams that build it in a spreadsheet for December rebuild it every time someone asks a new question. The same logic applies here as in the shift from annual reviews to continuous monitoring: the cadence you design now decides how much effort next year costs.

Where software helps

No platform makes you EUDR compliant, and any vendor who says otherwise is overselling. What good software does is remove the two things that actually break these programmes: chasing people, and losing evidence.

EvaluationsHub handles the supplier-facing layer of exactly this work. Structured data requests with per-supplier completion tracking, automated reminders that keep the response rate climbing, documents and evidence stored against the supplier record rather than in an inbox, and an audit trail that builds itself as the team works. It connects to the rest of the supplier lifecycle too, so origin and compliance data sits beside supplier scorecards, risk and corrective actions instead of in a separate silo. If you are also working through the broader due diligence agenda, our purchasing manager’s guide to CSDDD covers the neighbouring requirement.

If you want to see what this looks like with your own supplier list, you can run a focused pilot or book a demo.

Frequently asked questions

When does EUDR apply?
The EU Deforestation Regulation applies from 30 December 2026 for large and medium operators and traders, and for micro and small operators that were already covered by the EU Timber Regulation. Other micro and small operators have until 30 June 2027. Products added by the July 2026 delegated act apply from 30 December 2027.

Which products are covered by EUDR?
Seven commodities are in scope: cattle, cocoa, coffee, oil palm, rubber, soya and wood, together with many derived products including leather, chocolate, tyres, furniture and paper. The list has changed more than once, so check current HS codes rather than an older summary.

What supplier data does EUDR require?
Product description and HS code, quantity, country of production, geolocation coordinates for every plot of land where the commodity was produced, evidence that production was legal in the country of origin, and supplier and customer details including reference numbers of any existing due diligence statements. Records are kept for five years.

Do I need a due diligence statement for every shipment?
Not always. A single statement can cover several shipments within a year where the material comes from the same assessed harvest events and the supply chain has not changed. Once different harvest events are involved, a new statement is needed.

What if I only buy from EU suppliers?
You are likely a downstream actor for much of that volume. In that case your main obligation is to collect and retain the reference numbers of the due diligence statements provided by your suppliers, rather than repeating the underlying due diligence yourself.

What are the penalties for non-compliance?
Member States set penalties, with maximum fines for legal entities of at least 4 percent of total annual EU-wide turnover. Other sanctions include confiscation of products and revenues, temporary exclusion from public procurement and public funding, and a temporary ban on placing or exporting the products concerned.

Is EUDR going to be delayed again?
In its simplification review of May 2026 the Commission confirmed that the regulation will not be reopened and that existing timelines continue to apply. Planning around 30 December 2026 is the prudent assumption.


Sources: European Commission, Regulation on deforestation-free products; European Commission, Commission updates product scope and tools to support EUDR, 13 July 2026; Council of the EU, Council signs off targeted revision to simplify and postpone the regulation, 18 December 2025; Baker McKenzie, EU Commission publishes simplification review of EUDR, May 2026; Schoenherr, EU Deforestation Regulation: is your supply chain ready?.

On 16 September 2026, ISO published ISO 9001:2026, the first full revision of the world’s most widely used quality management standard in more than a decade. Certification bodies are already publishing gap guides, and most commentary focuses on leadership, quality culture and climate.

For supplier quality and vendor management teams, the more useful question is simpler: what does the new edition change about how we select, monitor and develop external providers, and what should we do about it this quarter?

The good news: nothing in ISO 9001:2026 asks you to rebuild your supplier programme. The revision rewards teams that already manage suppliers with structure, evidence and follow-through, and it gives everyone else a clear reason to get there over the transition period.

The short version

  • Clause 8.4 (control of externally provided processes, products and services) keeps its core logic. You still need defined criteria for evaluating, selecting, monitoring and re-evaluating external providers, with documented evidence.
  • Clause 6.1 now separates risks from opportunities, each with its own action cycle. That maps neatly onto supplier risk management on one side and supplier development on the other.
  • Clause 4.1 asks you to determine whether climate change is a relevant issue, which for most manufacturers quickly leads to the supply base.
  • Clause 4.2 asks which interested-party requirements you will actually address through the QMS, which matters when customers flow down supplier requirements.
  • Quality culture and ethical behaviour are now explicit in leadership and awareness requirements, and suppliers are part of how that culture shows up in practice.
  • A three-year transition is widely expected, in line with earlier revisions. Confirm exact dates with your certification body.

Why 8.4 staying stable is actually good news

Clause 8.4 has always been where supplier management lives inside ISO 9001. It requires an organisation to determine the controls it applies to external providers, and to base them on the potential impact of what those providers deliver.

The 2026 edition keeps that foundation. Clause 8.1 is aligned with 8.4 terminology so operational planning now explicitly covers externally provided processes, products or services that are relevant to the QMS. In other words, suppliers are part of the operation you plan, not a separate topic you audit once a year.

That stability gives supplier quality teams a practical advantage: the work you invest now in consistent evaluation criteria, performance data and follow-up will carry straight into your transition audit. If you want a refresher on what good looks like, our guide on how to build a weighted supplier scorecard covers the mechanics.

Where the 2026 revision touches your supplier programme

1. Risks and opportunities now run on separate tracks (6.1)

In ISO 9001:2015, risks and opportunities sat together, and in many QMS documents “opportunities” became an afterthought. The 2026 edition splits them: one action cycle for risks, one for opportunities. A note also links risk actions to maintaining conformity during and after disruptions.

For a supplier programme, this is a helpful framing:

  • The risk track covers single-source exposure, financial fragility, capacity, quality escapes, geopolitical and logistics disruption. This is the work of supplier risk management: identifying which suppliers could interrupt conformity, and what you do before it happens.
  • The opportunity track covers suppliers who could improve cost, quality, innovation or sustainability if you invest in the relationship. This is where supplier development programmes and structured supplier performance improvement belong.

An auditor asking “how do you address opportunities?” is a chance to show that your best suppliers are managed actively, not only your worst ones.

2. Disruption resilience becomes part of the quality conversation

The link between risk actions and conformity during disruption reflects what quality teams have experienced over the past few years. It is hard to demonstrate that link with an annual supplier survey and a spreadsheet.

What helps is a monitoring rhythm that surfaces early signals: late deliveries trending up, a drop in responsiveness, repeated minor nonconformities. Moving from annual reviews to continuous supplier monitoring is one of the most practical steps you can take here, and it pays off in daily operations long before the audit.

3. Climate change relevance (4.1) reaches the supply base

The 2024 climate amendment is now fully integrated: organisations must determine whether climate change is a relevant issue for their context. For most manufacturers, a large share of climate exposure sits with suppliers, whether as physical risk to supplier sites or as emissions data customers are starting to request.

ISO 9001:2026 does not turn your QMS into a sustainability report. But if you conclude climate is relevant, your supplier evaluation criteria are a natural place to reflect it. Teams already collecting supplier ESG and CSRD data can connect those two worlds rather than running them in parallel.

4. Interested-party requirements you commit to (4.2)

The new 4.2 requirement asks you to determine which interested-party requirements will be addressed through the QMS. In practice, a lot of those arrive as customer flow-downs: supplier approval rules, special characteristics, traceability, audit rights.

Being explicit about which of these you manage through your supplier processes makes audits smoother and makes the conversation with customers easier. For automotive suppliers, our article on building a supplier scorecard that satisfies IATF 16949 shows how customer-specific requirements translate into scorecard criteria.

5. Quality culture and ethics include how you treat suppliers

Leadership must now demonstrate commitment to quality culture and ethical behaviour, and people must be aware of what that means (7.3). Culture is visible in behaviour, and supplier management is one of the most visible places: whether evaluations are fair and consistent, whether feedback reaches the supplier, whether corrective actions are closed or quietly forgotten.

Consistency across evaluators and sites matters here. Our piece on reducing bias in supplier performance reviews offers a few simple design choices that make evaluations more defensible and more useful for the supplier.

A practical 90-day plan for supplier quality teams

You have time. The aim of the first 90 days is not to be “2026-certified” but to know where you stand and to start collecting the evidence you will need anyway.

Days 1 to 30: map and baseline

  1. Get the standard and your certification body’s transition guidance, and note the dates that apply to you.
  2. List your current supplier evaluation, selection, monitoring and re-evaluation criteria (8.4.1) and check they are applied consistently across sites and categories.
  3. Segment suppliers by impact on conformity. A simple Kraljic-based segmentation is enough to decide where controls should be tighter.

Days 31 to 60: split risks and opportunities

  1. For critical suppliers, record the top risks to conformity and the planned actions, including continuity during disruption.
  2. Separately, pick three to five suppliers with clear improvement or innovation potential and define what you want to achieve with each.
  3. Decide whether climate change is relevant for your context, and if so, which supplier criteria will reflect it.

Days 61 to 90: close the loop and prove it

  1. Make sure every nonconformity from a supplier leads to a tracked supplier CAPA with an owner, a due date and verification of effectiveness.
  2. Check that evaluation results, decisions and follow-ups are retained as documented information that an auditor can navigate in minutes. A clear reporting and audit trail is the difference between a stressful audit and a calm one.
  3. Share results with suppliers. Feedback that never reaches the supplier improves nothing.

Where software helps (and where it does not)

A standard cannot be met by a tool, and ISO 9001:2026 is deliberately technology-neutral. What software does well is make good practice the default: the same criteria applied by every evaluator, reminders that keep reviews on cadence, CAPAs that cannot silently stall, and an audit trail that builds itself as you work.

EvaluationsHub is built for exactly this layer of supplier lifecycle management, from supplier onboarding and supplier scorecards to risk, CAPA and development. If you want to see how your current process would look in a structured setup, you can start a supplier performance pilot or book a demo.

Frequently asked questions

When was ISO 9001:2026 published?
ISO published ISO 9001:2026 on 16 September 2026. It replaces ISO 9001:2015.

How long is the ISO 9001:2026 transition period?
A three-year transition period is widely expected, in line with previous revisions, which points to late 2029. Your certification body will confirm the exact dates and audit rules that apply to you.

Does ISO 9001:2026 change clause 8.4 on external providers?
The core requirements of 8.4 remain: defined criteria for evaluation, selection, performance monitoring and re-evaluation of external providers, with documented evidence. The wider revision (separate risk and opportunity cycles in 6.1, climate relevance in 4.1, interested-party requirements in 4.2, quality culture and ethics) influences how you apply those controls.

Do we need new supplier evaluation criteria for ISO 9001:2026?
Not necessarily. Many organisations can keep their criteria and strengthen consistency, risk and opportunity actions, and evidence. If you decide climate change is relevant to your context, reviewing supplier criteria with that lens is a sensible step.

Is a supplier scorecard enough to meet clause 8.4?
A scorecard covers performance monitoring, which is a central part of 8.4. Auditors will also look at selection criteria, re-evaluation, actions on poor performance and documented evidence, so the scorecard works best as part of a connected process.


Sources: ISO news release, September 2026; ISO 9001:2026 standard page; CQI | IRCA revision guidance; TÜV Rheinland revision overview; SGS publication note.

Published by EvaluationsHub. We make one of the products discussed below, so we have described every other vendor using their own public pages and linked each claim. Vendor information last reviewed 29 September 2026.

Every supplier management vendor now has an AI story. Some call it an assistant, some a copilot, some a fleet of agents. The demos look alike: a chat box, a summary of a supplier, a risk alert that appears on cue. The differences that matter for a supplier quality or vendor management team sit underneath, and they rarely show up in a standard demo script.

This guide gives you a way to compare them. It is written for people who have to live with the result: the supplier quality engineer who owns the CAPA, the category manager who owns the QBR, and the procurement lead who has to explain an AI decision to an auditor.

Why comparing AI features is harder than it looks

Buyers are clearly interested and still cautious. In a Gartner survey of 101 chief procurement officers run in January and February 2026, only 36% said they were very confident in their ability to redesign roles and processes around AI. The Hackett Group’s 2026 Procurement Key Issues study found that 43% of organisations are actively pursuing AI deployment, but only 12% report large-scale implementation, and that 69% access AI through capabilities embedded in their existing procurement platforms.

That last figure is the important one. Most teams will not buy AI on its own. They will get whatever AI comes with the supplier platform they choose. So the AI question is really a platform question, and it deserves the same rigour as the rest of your evaluation.

Three things make it hard:

  • The same words mean different things. “Agent” can mean a model that drafts an email or one that changes supplier master data without asking.
  • Availability varies. Several capabilities announced in 2025 and 2026 are in beta, rolling out, or planned for a later release. Vendors usually say so on their own pages, but not in the demo.
  • AI is only as good as the supplier data under it. A brilliant model reading a stale supplier record produces a confident, wrong answer.

Compare the loop, not the model

Almost every vendor builds on one of a handful of large language models. Comparing model names tells you little. What differs is the loop the AI sits in. For supplier management, that loop has five steps, and you can compare every vendor on each one:

  1. Read. Which of your data can the AI actually see? Scorecards, contracts, CAPA history, supplier portal submissions, external risk feeds, ERP transactions?
  2. Reason. Does it show why it reached a conclusion, with the data points and sources behind it?
  3. Recommend. What does it propose: a summary, a score, a corrective action, a sourcing event, a message to a supplier?
  4. Act. What happens next? Does a person approve, edit or dismiss, or does the AI proceed on its own? Which actions can it never take alone?
  5. Record. Is every AI output, approval and outcome logged in a way you could export and hand to an auditor?

A capability that is strong at step 3 and silent on steps 4 and 5 is a nice demo. A capability that is solid across all five is something you can put into a regulated supplier quality process.

Eight questions to ask every vendor

Use these in the RFP and again, live, in the demo. They are deliberately practical.

1. What supplier data does the AI read, and how fresh is it?

Ask for a list of the objects the AI can access. The most useful supplier AI connects things that normally live apart: a contractual KPI in one place and the measured OTIF or PPM in another. If the AI only reads documents you upload into a chat, it is a writing aid, which is useful but different.

2. Can you show me the reasoning behind one recommendation?

Pick a recommendation in the demo and ask to see exactly which data triggered it. You want to see the threshold, the measured values and the time window, not a paragraph of fluent prose.

3. What can it do without a human, and can I switch that off?

This is the single most important question. Ask for the list of actions the AI can take autonomously, the list it can only propose, and whether you can configure the boundary per action type. Supplier-facing communications, awards and changes to bank details deserve particular attention.

4. Where is the audit trail, and can I export it?

For teams working under ISO 9001, IATF 16949, GMP or medical device rules, an AI-proposed corrective action is still a corrective action. You need to show who approved it, when, and on what evidence.

5. Is my data used to train models, and where is it processed?

Get the answer in writing, in the contract, not just on a web page. Ask separately about the vendor’s own models and any third-party model providers they use.

6. What is generally available today, and what is on the roadmap?

Ask the vendor to mark each capability you saw as generally available, beta, or planned, with dates. There is nothing wrong with a roadmap. There is something wrong with buying one by accident.

7. What happens when the AI is wrong?

Ask to see a dismissed recommendation. Does the dismissal get recorded? Does the system learn from corrections? Can you tune thresholds so the queue does not fill with noise?

8. Can you run it on our data before we sign?

A demo on the vendor’s sample data proves the interface works. A short session on a slice of your own supplier data proves the AI works for you.

What leading vendors say their AI does

The table below summarises how each vendor describes its own AI for supplier management, using its public pages as of 29 September 2026. It is a starting point for your own questions, not a ranking, and features change quickly. Where a vendor’s page did not address a topic, we say “not stated on the page reviewed”. That does not mean the capability is absent, only that you should ask.

Supplier management AI as described by each vendor (public sources, reviewed 29 September 2026)
Vendor AI layer Supplier management examples, in the vendor’s framing Oversight and data statements published A genuine strength
SAP (Ariba) Joule, Supplier Management Assistant Sanctions screening, financial health checks and risk evaluations; supplier classification; onboarding data enrichment; “corrective action plans before performance risk materializes” Not stated on the supplier management page reviewed; see SAP’s general AI ethics principles Built on a long-established supplier lifecycle module and third-party data enrichment
Coupa Navi agents Supplier Discovery Agent and Supplier Assistance Agent (announced November 2025) Not stated in the announcement reviewed Community data from a very large buyer and supplier network
Ivalua IVA Validating documents and enriching profiles at onboarding; keeping risk and performance scores current “Every AI action has a person accountable”; continuous audit trails; IVA inherits user permissions; “never uses your data to train LLMs” Among the clearest published governance commitments
JAGGAER JAI Supplier self-service onboarding and cited answers across procurement data “JAI suggests. You decide. Always.” No customer data used for model training; data processed in the customer’s selected region Explicit data residency statement and source citations on answers
Oracle Fusion Procurement Supplier Qualification Workspace (agentic app) AI summary of qualification compliance; flags missing or adverse qualifications; currently up to 500 strategic suppliers across three tiers “Review AI recommended priority actions for accuracy before applying” Precise release documentation, including stated limits
Gatekeeper Gatekeeper AI and agents SLA Compliance Check Agent; Bank Details Validator Agent; claims 50+ agents Not stated in detail on the page reviewed A wide catalogue of narrow agents on one vendor and contract record
Kodiak Hub AI across the platform AI-enhanced insights for supplier performance, risk forecasting and anomaly detection; document extraction ISO 27001 stated; AI oversight not stated on the page reviewed AI inside a full SRM loop of ratings, goals and actions
Prewave AI-based risk alerts Prioritising risks by AI-driven impact, probability and relevance; deep-tier mapping Not stated on the page reviewed External risk sensing across languages and supply tiers

Two patterns stand out. First, governance disclosure is uneven. A few vendors publish specific commitments on human accountability, training data and residency; many do not address them on their AI pages at all. Second, most published examples cluster around risk sensing, onboarding documents and sourcing. Fewer vendors describe AI that connects what a supplier promised in a contract with how that supplier is actually performing, which is where supplier quality teams spend most of their week.

Suites, specialists and risk platforms: which kind of AI fits you

A source-to-pay suite’s AI is a strong fit if you already run that suite, your priority is transactional efficiency across sourcing, contracts and payables, and you have an enterprise agreement in place. The AI benefits from seeing spend and transaction data in one system.

A risk intelligence platform’s AI is a strong fit if your main exposure is external: disruption, sanctions, adverse media or deep-tier visibility. It watches the world outside your supply base very well.

A supplier performance and lifecycle specialist’s AI is a strong fit if your pain sits in the relationship itself: scorecards, corrective actions, QBRs, contractual KPIs, supplier development, and the evidence trail auditors ask for. Here the AI can be very close to the data that quality and vendor management teams work with every day.

Many large organisations will combine a suite with a specialist. The limits of S2P suites for supplier relationship work and the ERP versus specialised SPM question are covered in separate articles.

Where EvaluationsHub, InitiativesHub and Eva AI fit

We are a younger specialist that is growing quickly, and we built our AI around the loop described above rather than around a chat window. Three products work on one supplier data model:

  • EvaluationsHub covers supplier performance and risk: weighted supplier scorecards per segment, risk and ESG data collection, corrective actions (CAPA), QBR management and a two-way supplier portal.
  • InitiativesHub covers execution: intake, RFx, supplier qualification, awarding, contract management with SLAs and KPIs mapped to clauses, and onboarding that hands over to EvaluationsHub when it is complete. Together, the two cover the full supplier lifecycle.
  • Eva AI is the AI layer on top. It is designed to do three things.

Contract and performance cross-check. Eva reads the KPI obligations in your contracts and compares them with live scorecard data. When a deviation crosses a threshold you define, it proposes a corrective action with its reasoning attached. For example: a contract requires 97% OTIF, the 30-day average is 88.4%, and the gap has exceeded your 5-point threshold for three consecutive weeks.

Risk and compliance monitoring. Eva watches risk signals across the supplier portfolio against your acceptance frame and proposes the right compliance workflow, linked to the relevant contract clause.

Cost reduction intelligence. Eva looks for consolidation opportunities, suppliers ready for renegotiation based on performance, and pricing anomalies, and proposes structured cost reduction projects in InitiativesHub.

On the questions above, our answers are simple. Eva recommends and you decide: every action is held for human review, with approve, edit or dismiss in one click. No supplier-facing action happens without explicit approval. Confidence thresholds are configurable per action type. Every AI recommendation, approval and outcome goes into an immutable, exportable audit trail. The platform is ISO 27001 certified and hosted in the EU.

We are not the right choice for everything. If you want one vendor for requisitions, invoices and payments, a suite will serve you better. If deep-tier news monitoring in dozens of languages is your main need, a dedicated risk intelligence platform goes further. Our focus is the performance, risk and improvement loop with your suppliers, and the AI that makes that loop faster without taking the decision away from your team.

A note on regulation

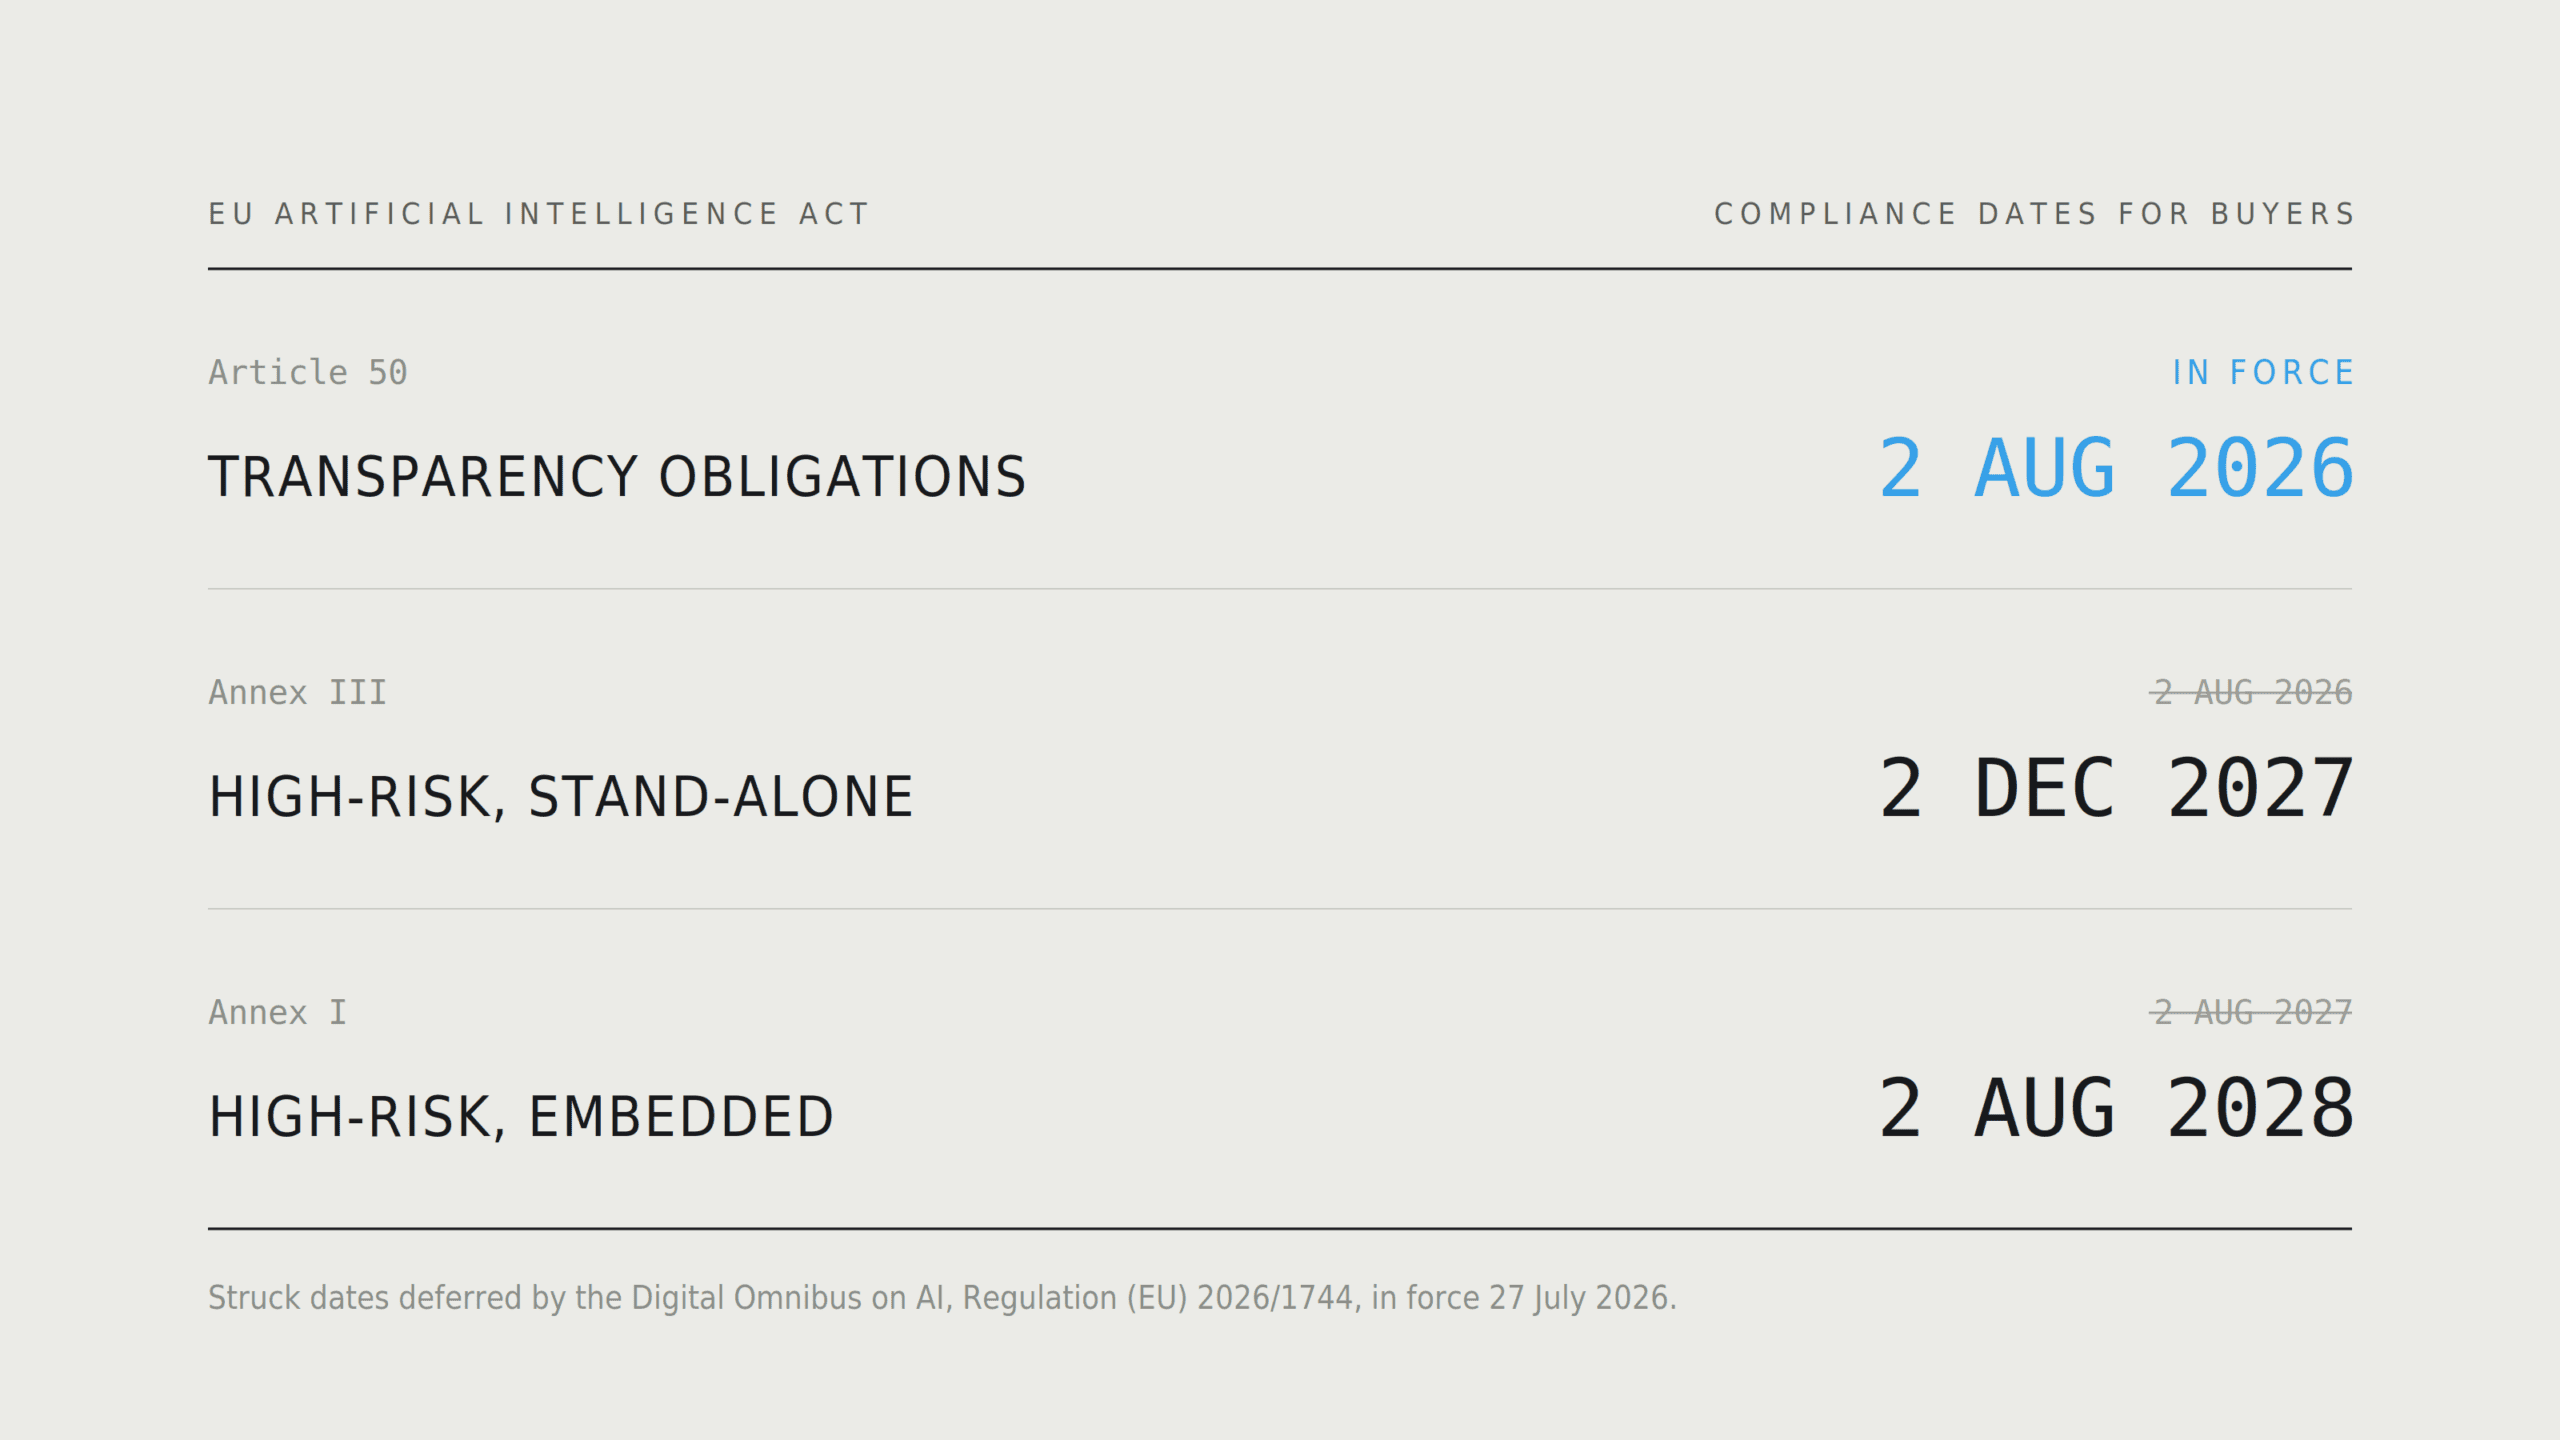
Human oversight is becoming a regulatory expectation, not only good practice. Under the EU AI Act, high-risk AI systems must be designed so that people can oversee them effectively. In May 2026 the Council and Parliament agreed to move the application dates for high-risk obligations to 2 December 2027 for stand-alone high-risk systems and 2 August 2028 for those embedded in products. Most supplier management uses are unlikely to fall in the high-risk categories, but the oversight principle is a sensible benchmark for any AI that proposes actions affecting suppliers. Our EU AI Act guide for procurement goes further; check any specific obligation with your legal team.

What this comparison cannot tell you

We compared public statements, not live systems. We did not test any vendor’s AI on real data, pricing for AI add-ons is rarely published, and some capabilities may be further along or further behind than a web page suggests. Ask each vendor, including us, to show you the loop working on your own suppliers.

Frequently asked questions

What is the most important AI feature in SRM software?

The ability to connect data that normally sits apart, such as contract obligations and measured performance, and to turn a deviation into a proposed action with clear reasoning. Summaries and chat are helpful, but the value is in the action loop.

Should AI in supplier management act without human approval?

For low-risk, reversible, internal tasks, limited autonomy can be reasonable. For supplier-facing communications, awards, corrective actions and any change to supplier bank details, human approval with an audit trail is the safer design and the one auditors will expect.

How do I check whether a vendor’s AI feature is actually available?

Ask the vendor to label each capability as generally available, beta or planned, with dates, and put that list in the contract schedule. Many vendors state availability on their own release notes or press releases, so check those too.

Do I need clean supplier data before AI is useful?

You need reasonably current core data: supplier records, a scorecard with defined KPIs, and your key contract terms. You do not need perfection. A good platform will show you where data gaps are weakening its recommendations.

If you want to see the loop on your own supplier data, book a demo and bring one supplier you are worried about.

By Prof. Dr. Bert Paesbrugghe, founder of EvaluationsHub and associate professor at IÉSEG School of Management.

A kitchen can have a superb fishmonger and still run out of fish on a Saturday night. I learned that as a chef long before I studied buyers for a living. The fishmonger was financially sound, delivered great product and never once missed an invoice. The problem sat elsewhere: one boat, one road, one driver. When any of the three failed, the supplier was fine and my dining room was not.

Procurement is now discovering the same lesson at scale. ProcureAbility’s 2026 CPO Benchmark Study, published on 9 September 2026 and based on 160 senior procurement leaders at large enterprises across 21 industries, describes what it calls a shift in procurement’s risk focus from supplier health to supply continuity. Read that sentence twice. For years we asked whether the supplier is a sound business. Increasingly we are asking whether the thing we need will actually arrive.

The numbers behind that shift are worth sitting with. In the same study, 62% of respondents cite geopolitical disruption as a primary risk and 55% cite logistics disruption. Yet only 6% say they have predictive or real-time monitoring tools, while 62% still rely on manual or periodic risk assessment. So buyers worry about continuity more than anything, and most of them check on it the way a chef checks a walk-in fridge: by opening the door now and then and hoping.

Why this is a relationship question, not only a tooling question

When I interviewed buyers for my research, continuity came up again and again, often before price did. The sentence behind it was rarely “we want the cheapest supplier” and far more often “I never want to explain to my board why the line stopped”. Business continuity is the buyer’s quiet top priority, and it shapes how they judge every supplier interaction, whether or not they say so.

Here is the part that interests me most. The early warning signs of a continuity problem usually sit with the supplier long before they sit in any dashboard. A second-tier component maker is struggling. A port is congested. A key engineer has left. The supplier often knows first. Whether the buyer hears about it depends on something no monitoring tool can buy: the quality of the relationship.

That is where balance enters. If a supplier expects to be punished for bad news, bad news arrives late. If a buyer never explains which parts of the supply are truly critical, the supplier cannot prioritise them. Both sides are guessing, and the guessing happens in the space where continuity is won or lost.

Three habits that build continuity before the crisis

Say what “critical” means. Most buyers have a mental list of the three or four things that would stop the business. Few suppliers have ever seen that list. Share it. A supplier who knows that one item out of forty matters enormously will treat it differently on a bad week. This is mise en place for a relationship: everything in its place before service starts.

Make bad news cheap. Ask suppliers, in a regular conversation and not only in a quarterly review, what worries them about the next ninety days. Then respond to the answer with help, not a penalty clause. A supplier who is thanked for an early warning will send the next one earlier.

Swap the snapshot for a rhythm. A yearly risk assessment is a photograph of a river. Continuity moves. Even without expensive tooling, a light monthly check-in on the handful of critical suppliers gives you more signal than a thick annual questionnaire. Technology can then amplify that rhythm, but it should follow a logic you have already agreed on.

The balance point

There is a temptation, when risk headlines pile up, to tighten control: more audits, more clauses, more reporting demands. Some of that is sensible. Yet a supplier buried in compliance requests has less attention left for your actual supply, and the relationship becomes a paperwork exercise that produces reassuring documents and thin resilience.

The alternative is equilibrium. The buyer is clear about what matters and generous with context. The supplier is honest about risk and early with news. Neither side wins at the other’s expense, because the outcome both want, goods arriving on time, is shared.

I explore this buyer-side perspective, including what buyers told me they wish their suppliers understood, in my book The Buyer’s Balance: What your customers want to share with you (Owl Press, 2025, ISBN 9789464778908). More at evaluationshub.com/book.

So here is my question for this week. If your most critical supplier had a problem today, how many days would pass before you heard about it, and from whom?

Source: ProcureAbility, 2026 CPO Benchmark Study, press release of 9 September 2026 (160 senior procurement leaders, 21 industries).

Ask a purchasing manager what keeps them awake at night and you will rarely hear “unit price”. You hear a version of the same sentence, phrased a dozen different ways: the line has to keep running.

I have interviewed a lot of buyers over the past decade for my research, and this is the most consistent thing I have found. Savings get you a good annual review. A stoppage gets you a very different conversation with the board. Continuity is not one priority among several for most purchasers but the floor that everything else stands on.

So here is the uncomfortable question. If continuity is the thing you care about most, how much of your actual supplier conversation is about it?

What the numbers say

QIMA’s 2026 Global Sourcing Survey, which draws on the experiences of more than 1,000 businesses with international sourcing networks, found that the average company now maps 60% of its supplier network, up from 53%. That is real progress. And yet only 18% report full end-to-end visibility. Four out of five buying organisations are making continuity decisions with a partial map.

The same survey found that 79% of supply chains expect costs to be a major disruption in 2026, and that 43% shifted sourcing locations during 2025. The map is changing faster than most organisations can redraw it.

Sit with that for a moment. Your top priority is the thing you can see least clearly.

Your supplier can see what you cannot

Here is what I find strange about the way most buyer-seller conversations are structured. The person sitting across the table often knows exactly the part of the chain you have never mapped. They know which of their own inputs is single-sourced. They know their tier-two supplier has been quoting longer lead times since spring. They know the plant in question runs at 95% and has no slack for your rush order in November.

They know all of it. And in a great many relationships, nobody ever asks.

When I was still cooking, mise en place was not a nice-to-have. You did not discover at seven in the evening that the fish had not arrived. You found out at ten in the morning, because you had a relationship with the person who brought the fish, and that person told you things before you had to ask. That relationship was worth considerably more than the three cents a kilo you might have saved somewhere else.

Procurement has exactly the same dynamic and usually far less of the conversation.

Why buyers hold back

Buyers have reasons for not opening up about continuity risk. If you tell a supplier you have no alternative source, you have told them something useful about your negotiating position. If you tell them the launch date is immovable, you have handed them leverage.

I understand the instinct. I also think the arithmetic has changed. The cost of an information gap that hides a disruption is now much higher than the few points of margin that gap protects. A supplier who does not know that a particular component is critical to you will not prioritise it when their own capacity tightens, not out of obstruction but out of simple ignorance.

This is the balance I write about in The Buyer’s Balance: What your customers want to share with you (Owl Press, 2025). Equilibrium in a B2B relationship is not a matter of both parties being pleasant to each other but of both parties holding roughly the same picture of what is going on, so that each can act sensibly on it.

Three questions worth asking this quarter

If continuity is genuinely your top priority, put it into the conversation rather than into a clause.

Where is your own single point of failure? Not yours as in your company. Theirs. Most suppliers will answer honestly if you ask in a way that does not sound like the opening of an audit.

What would you need from us to hold our lead time if your capacity tightened? Usually the answer is a forecast, or earlier notice, or a commitment they can plan against. Often it costs you nothing at all.

What have you told other customers that you have not told us? Slightly cheeky. Very revealing.

None of these show up on a supplier scorecard. All three of them do more for continuity than another paragraph about liquidated damages.

The consistency point

A supplier who tells you about a problem three weeks early is worth more than one who never has problems on paper. Predictability beats brilliance. A vendor who performs at eight out of ten every single time is far easier to build a business around than one who swings between ten and four.

And if you want that from your suppliers, you have to be that for your suppliers. Consistent forecasts. Consistent feedback. Consistent honesty about what you actually need and when.

Your top priority deserves more than a paragraph in the contract.


Bert Paesbrugghe is associate professor of sales management and purchasing strategy at IESEG School of Management and author of The Buyer’s Balance: What your customers want to share with you (Owl Press, 2025), ISBN 9789464778908. More at evaluationshub.com/book.

Source: QIMA, 2026 Global Sourcing Survey: From Disruption to Opportunity (2026), based on responses from over 1,000 businesses with international sourcing networks. qima.com

Most supplier performance software gets evaluated in a way that guarantees an inconclusive answer. Here is how to design a pilot that produces a decision instead of a debate.

By the time a procurement team starts looking seriously at supplier performance software, the problem is usually well understood internally. Scorecards live in spreadsheets, half the stakeholders never respond, the quarterly review depends on whoever remembered to update the file, and nobody can produce a twelve-month trend for a strategic supplier without losing a day to it.

What happens next is where most evaluations go wrong. The team books three demos, picks a favourite, runs something called a pilot for a few weeks, and then discovers the pilot never answered the question they actually needed answered. It was too small to show anything, too short to show a trend, or scoped in a way that quietly avoided the hard parts.

A pilot is not a longer demo. It is an experiment, and it deserves to be designed like one.

Start by writing down what the pilot is testing

Feature questions belong in a demo. You can confirm in thirty minutes whether a platform supports weighted criteria, multi-language surveys, or a CAPA workflow. Spending eight weeks confirming the same thing is expensive.

A pilot exists to test behaviour, and there are really only three questions worth the effort:

  1. Will our internal stakeholders respond? Adoption inside the buying organisation is the single most common point of failure, and it has almost nothing to do with software quality.
  2. Will our suppliers engage? A supplier-facing process that suppliers ignore is a reporting exercise, not a performance system.
  3. Does the output change a decision? If the pilot produces dashboards that nobody acts on, you have bought visibility, not performance management.

Write those down, in your own words, with your own numbers attached. Everything below is in service of answering them.

Choose the pilot suppliers deliberately

Two instincts to resist. The first is to pick the easiest suppliers, the ones with an engaged account manager who will fill in anything you send. That proves nothing, because those relationships already work. The second is to load the pilot with your worst performers, which turns a software evaluation into a series of difficult commercial conversations and confuses the two.

A representative slice of fifteen to twenty-five suppliers works better than either extreme. In practice:

  • Two or three strategic suppliers where the relationship is good, to test depth: multi-criteria evaluation, joint improvement plans, executive-level reporting.
  • Ten to fifteen tactical or leverage suppliers, to test scale: does the automation actually remove the chasing, or does it just move it into a new tool?
  • Two or three suppliers with a live performance issue, to test the action loop end to end, from finding the problem to closing it.
  • At least one supplier outside your home country or language, because that is where portal adoption assumptions break.

Cover at least two categories with different internal evaluator groups, for example quality and operations, or IT and facilities. If procurement is the only function scoring suppliers during the pilot, you have tested a procurement tool and learned nothing about what happens when the evaluator is an engineer with no interest in your project.

Record the baseline before day one

You cannot demonstrate improvement against a memory. Before anything is configured, spend half a day capturing where you are today. It is the least glamorous part of a pilot and the part that carries the business case.

Baseline metric How to capture it Why it matters
Stakeholder response rate in your last evaluation round Invitations sent versus completed The primary internal adoption signal
Elapsed days from launch to a complete scorecard set Calendar dates from your last cycle Measures the real cost of chasing
Hours spent per cycle collecting and consolidating data Ask the person who actually does it The number your finance function will care about
Open supplier issues with a named owner and a due date Count them Most teams discover the number is close to zero
Suppliers with comparable score history over twelve months Count them Distinguishes a trend from a collection of anecdotes

Most of these numbers are uncomfortable to write down. That discomfort is the point. In ninety days they become the before column in a one-page comparison, and a before-and-after table is far more persuasive than any vendor benchmark.

Run it for two cycles, not one

Sixty to ninety days, spanning at least two full evaluation cycles.

One cycle tells you the platform can send a survey and build a scorecard. Two cycles tell you whether anything moved between them: whether response rates rose once stakeholders knew what to expect, whether an action raised in the first cycle was closed by the second, whether a score changed and you can explain why. Supplier performance management is a loop, and testing half a loop teaches you very little.

If your production cadence is quarterly, compress it during the pilot rather than waiting six months for a verdict. Run monthly, or run two cycles six weeks apart. You can settle the production cadence and governance model once you know the process works.

Put real suppliers in it

This is where rollouts die, and it rarely shows up in an internal-only pilot.

Your suppliers already maintain portal logins for most of their major customers. If yours needs a new password, a training call, and a PDF manual, the engagement rate you see with twenty suppliers is the engagement rate you will see with four hundred, only worse, because at four hundred nobody is calling to help them.

Things worth measuring on the supplier side:

  • How many suppliers complete their first action without contacting anyone for help
  • Elapsed time from invitation to first login
  • What happens when the registered contact is a shared mailbox, or when the person forwards the request to a colleague
  • Whether a supplier can see what they are being measured on, before they are measured on it

That last point is not a usability detail. Suppliers who understand the criteria improve against them. Suppliers who receive a score with no visible basis dispute it, and disputes are the most expensive output a scorecard programme can generate.

Agree the success criteria in writing, before kickoff

One page, signed off by your sponsor and shared with the vendor. Specific numbers, not adjectives:

  • Stakeholder response rate above a defined threshold by the second cycle
  • A complete scorecard set within a defined number of working days, with no manual chasing by the procurement team
  • A defined number of supplier actions raised, assigned to a named owner, and closed inside the platform
  • At least one real decision that used pilot output as evidence: a negotiation position, a volume reallocation, a supplier development plan, or a de-escalation

The last criterion is the one that persuades a CFO. The others are hygiene.

Expect the vendor to negotiate these targets, and let them. A vendor who pushes back on a specific number usually knows exactly where the friction sits in that part of the process, and that conversation is more revealing than any demo.

Decide in advance what happens on day ninety

Three outcomes, all legitimate: roll out, extend with a specific and named fix, or stop. Write down which evidence leads to which, and who makes the call.

Pilots without a pre-agreed exit tend to drift into permanent free trials. That is worse for you than for the vendor. There is no budget conversation, no internal urgency, the champion’s attention moves elsewhere, and within a quarter the team has quietly reverted to the spreadsheet while an unused login sits in the tech stack.

What a good pilot report looks like

Two pages, not twenty:

  1. Before and after on the baseline metrics you captured in week one.
  2. One supplier story, end to end. Issue identified, action raised, owner assigned, closure evidence, score movement. A single complete example is more convincing than aggregate statistics.
  3. Adoption numbers for both sides, internal and supplier.
  4. An honest list of what did not work. Configuration gaps, integration friction, stakeholders who never engaged.
  5. The cost of doing nothing, expressed in the hours and elapsed days from your baseline.

Point four matters more than people expect. A pilot report with no negatives in it reads as a sales document and gets discounted accordingly by anyone senior enough to approve the spend.

Five ways pilots go wrong

  • Procurement-only participation. You learn nothing about the stakeholders who will make or break the rollout.
  • Importing poor supplier master data and blaming the platform. Clean twenty records properly rather than importing two thousand badly. Data quality problems surface either way, but at least you will know which ones are yours.
  • Changing the evaluation framework mid-pilot. Then cycle one and cycle two are not comparable, and you have lost the trend you were trying to observe.
  • Running single-threaded. One champion, no sponsor. If that person changes role, the pilot ends regardless of results.
  • Measuring satisfaction instead of behaviour. “Everyone liked it” is not evidence. Response rates, closure rates, and cycle times are.

The short version

Most supplier performance evaluations end without a decision, not because the software is difficult to judge, but because nobody defined in advance what would count as evidence. Spend the first week on baseline data and success criteria, put real suppliers in the scope, run two cycles, and the final report more or less writes itself.


EvaluationsHub runs structured pilots with a defined scope, agreed success criteria, and a fixed end date. If you already run supplier evaluations in spreadsheets, send us your current setup and we will rebuild it in the platform so your pilot starts from your framework rather than a generic template. Book a session with a procurement specialist.

Analyst Coverage of Supplier Relationship Management in 2026: Who Covers SRM, and How to Read It
EvaluationsHub ResearchAnalyst Landscape2026

Analyst coverage of supplier relationship management in 2026

Who covers SRM, what each evaluation actually assesses, and the inclusion thresholds that quietly decide which vendors you ever get to see.

There is no single analyst report called "the SRM Magic Quadrant."

That is the first thing worth knowing, because most shortlists are built as though there were one. Supplier relationship management is covered in pieces, spread across four research houses that each define the market differently, evaluate different things, and set different bars for which vendors are even allowed to appear. Read one report as if it were the whole map and you will end up with a shortlist shaped by an inclusion rule you never saw.

This is a short guide to what actually exists, current as at July 2026. It is drawn from a longer reference report; the link is at the end.

The reports that cover SRM, and what each one is

Four publishers matter for supplier management technology. They are not interchangeable.

The analyst evaluations that shape SRM shortlists, July 2026
EvaluationPublisherCurrent editionWhat it evaluates
Magic Quadrant for Source-to-Pay SuitesGartner21 Jan 2026
13 vendors
Whole procurement suites. Supplier management is one required module inside a larger footprint.
Magic Quadrant for Supplier Risk Management SolutionsGartner4 May 2026
2nd edition
Supplier risk specifically: risk sensing, sub-tier mapping, continuous monitoring.
The Forrester Wave: Supplier Value Management PlatformsForresterQ3 2024
9 providers
A scored, weighted evaluation of the nine platforms Forrester judges most significant.
Supplier Value Management Platforms LandscapeForresterQ1 2026
29 vendors
An unscored market overview. Broader net than the Wave, no ranking.
SolutionMapThe Hackett Group
(Spend Matters)
Spring 2026
118 vendors
500+ requirements per category, mandatory demos, verified customer ratings. Refreshed twice a year.
50 to Know / 50 to WatchThe Hackett Group2025–26
117 named
Analyst-selected recognition lists based on demonstrations. A shortlist starting point, not a ranking.
Procurement Outsourcing PEAK MatrixEverest Group2025
23 providers
Service providers, not software. Relevant when someone else will run the transformation.

The practical takeaways. If a vendor says it is "recognised by Forrester," ask which instrument: being scored in the Wave and being listed in the unscored Landscape are very different statements. If a vendor cites Gartner, ask which quadrant, because supplier risk and source-to-pay are separate markets with separate reports. And note that there is no Magic Quadrant for supplier performance management at all; that discipline is covered only inside broader categories, which means buyers of pure SRM technology have the least analyst validation available to them.

The part nobody reads: inclusion criteria

A quadrant tells you who won. The inclusion criteria tell you who was allowed to play.

The second is more useful, and almost nobody looks it up. To qualify for Gartner's 2026 source-to-pay Magic Quadrant, a vendor had to hold at least 40 live customers with $500 million or more in revenue, plus at least 12 new customers at that scale signed in a single calendar year.1 Forrester's Wave scores nine providers. Even SolutionMap, the broadest instrument, requires the vendor to complete a 500-plus requirement questionnaire and a live demonstration.

These are reasonable design choices for the job each report does. Gartner's source-to-pay report is explicitly written for large enterprises selecting one suite for the whole organisation, and the thresholds fit that job. But stack the criteria together and a pattern appears that no single report states.

The coverage floor A chart showing analyst evidence is dense for buyers above one billion in revenue and thin below five hundred million, because vendor inclusion thresholds exclude those serving smaller buyers. The band between one hundred million and one billion is labelled thinly evidenced. ANALYST EVIDENCE DENSITY BY BUYER REVENUE $10bn + $1–10bn $500m–1bn $100–500m GARTNER · FORRESTER · SOLUTIONMAP · PEAK GARTNER · LANDSCAPE · SOLUTIONMAP SOLUTIONMAP · PARTIAL THINLY EVIDENCED GARTNER S2P FLOOR: 40 CUSTOMERS AT $500M+ Coverage follows vendor eligibility thresholds, not buyer need.
The coverage floor. Above roughly $1bn in buyer revenue, four independent instruments cover the market. Between $100m and $1bn, where most European manufacturers and mid-market industrials sit, a buyer relies largely on vendor claims and its own reference checks.

The evidence is dense above $1 billion in buyer revenue and thin below it. Not because smaller organisations matter less, but because the vendors serving them cannot clear the thresholds to appear. If your company sits between €100 million and €1 billion, the published landscape was, in large part, drawn for a different terrain.

What to do about it if you are below the floor

None of this means ignore the analysts. Their methodology sections are genuinely instructive and their coverage of the enterprise end is the best available. It means use the reports for what they are good at, and compensate where they thin out.

  • Use the criteria, not the placements. Gartner's list of required modules and its published evaluation weightings is a well-built requirements skeleton. Lift the structure; do not inherit the vendor list.
  • Weight verified customer ratings over quadrant position. SolutionMap is the only instrument combining a functional assessment with mandatory demos and anonymised verified customer references. For a mid-market buyer that carries more signal than a coordinate on a grid.
  • Reference-check at your own scale. A reference from a $12 billion customer tells you nothing about implementation effort at $400 million. Insist on references matched on revenue, supplier count and team size.
  • Run a paid pilot on real data. Below the floor, eight to twelve weeks on a live supplier segment produces more decision-relevant evidence than any report. Design the pilot before you shortlist, so vendors compete on identical terms.

The one-line rule

Ask three questions of any placement a vendor cites: which report exactly, what date and ID, and what were the inclusion criteria. The third question is the one that changes shortlists, and it is the one almost nobody asks.

Full reference report

The complete SRM vendor landscape and transformation guide

This piece is a summary of one section. The full report maps every vendor by functional layer, lists all major analyst evaluations with dates and inclusion criteria, and sets out an evidence-based sequence for running a procurement transformation. Fully sourced, no analyst text reproduced.

Read the full report

Questions and answers

Is there a Gartner Magic Quadrant for supplier relationship management?

No. Gartner publishes a Magic Quadrant for Source-to-Pay Suites and a separate one for Supplier Risk Management Solutions. Supplier information and performance management is treated as a module inside the source-to-pay market, not as a standalone Magic Quadrant. Supplier performance management as a discipline is covered by Forrester under supplier value management and by The Hackett Group's SolutionMap under supplier relationship management and risk.

Which analyst firms cover supplier relationship management in 2026?

Four. Gartner covers it inside source-to-pay and covers supplier risk separately. Forrester covers it under supplier value management, in a scored Wave of nine providers and an unscored Landscape of 29. The Hackett Group, through Spend Matters, covers it in SolutionMap across 118 vendors and in its 50 to Know and 50 to Watch recognition lists. Everest Group covers procurement outsourcing service providers rather than software.

What is the difference between the Forrester Wave and the Forrester Landscape?

The Wave is a scored, weighted evaluation of nine providers Forrester judges most significant. The Landscape is an unscored overview of a wider set, 29 vendors in Q1 2026. Inclusion in a Landscape is a statement of market presence, not of assessed capability. A vendor citing "recognised by Forrester" could mean either, so establish which.

Why do most SRM analyst reports focus on large enterprises?

Because of inclusion thresholds. Gartner's 2026 source-to-pay Magic Quadrant requires a vendor to hold at least 40 live customers with $500 million or more in revenue, plus 12 new such customers in a single year. Vendors serving smaller buyers cannot qualify, so the published evidence is dense above $1 billion in buyer revenue and thin below it. The gap reflects vendor eligibility rules, not buyer need.

How should a mid-sized company use analyst reports to choose SRM software?

As a requirements skeleton, not a shortlist. Use the published module lists and evaluation weightings to build requirements, weight verified customer ratings above quadrant position, insist on references matched to your own revenue band and supplier count, and run a paid pilot on live suppliers with identical terms across shortlisted vendors.

Author. Prof. Dr. Bert Paesbrugghe is founder and CEO of EvaluationsHub, associate professor at IÉSEG School of Management and guest professor at Ghent University. His doctoral research on buyer-seller relationships received the American Marketing Association Best Dissertation Award.

Source. Figures are drawn from the publicly available editions of the Gartner, Forrester, Hackett Group and Everest Group evaluations current at July 2026. The full report carries the complete source register. No analyst text is reproduced.

Published by EvaluationsHub, a supplier lifecycle and performance management platform. evaluationshub.com

How to Build a Supplier Scorecard That Actually Satisfies IATF 16949 | EvaluationsHub
Supplier performance managementAutomotive12 min read

How to build a supplier scorecard that actually satisfies IATF 16949

Most procurement and quality teams already run some version of a supplier scorecard. The problem is that IATF 16949 does not judge that scorecard in isolation anymore. Get it wrong and an OEM can flag you before you flag yourself.

Since 2020, the International Automotive Task Force has run a program called the Supplier Performance Initiative, and it changes what a scorecard is for. If GM, Ford, Stellantis or another participating OEM rates one of your sites poorly on their own scorecard, that status can be reported straight into the IATF KPI Hub, a database your certification body has access to. Your internal spreadsheet and your actual IATF certificate are now connected in a way a lot of quality managers do not appreciate until it happens to them.

This guide covers what a scorecard needs to do to hold up under IATF 16949, how the major OEM scorecards actually work, which metrics carry real weight, and a practical process for building one that catches problems before an OEM reports them for you.

Automotive supplier scorecard categories and typical weighting Composite supplier score Quality PPM, first-pass yield, CAPA closure rate 40% Delivery On-time-in-full, lead time reliability 30% Cost Cost variance, cost of poor quality 20% Compliance IATF/CSR status, PPAP on-time rate 10%

A typical weighting split for an automotive supplier scorecard. Exact weights should shift by supplier segment and part criticality.

Why your scorecard and your IATF certificate are now linked

IATF 16949 has always required organizations to monitor customer satisfaction, but for years that requirement was interpreted loosely. Then, starting as a pilot with GM and Ford in 2019 and formally launched in March 2020, the IATF's Supplier Performance Initiative (SPI) gave the scheme teeth. Participating OEMs now report suppliers rated "Red" on their own scorecards directly into the IATF KPI Hub, a database certification bodies use when planning and scoping audits.

The logic behind it is straightforward, and quality consultancy simpleQuE lays it out well: if a supplier is consistently missing OEM expectations on delivery and quality, continued IATF certification of that supplier calls the credibility of the entire certification scheme into question. That is now the certification body's problem too, not just yours.

This means your internal scorecard cannot exist in a bubble. If your own numbers say "green" while your top three OEMs all say "red," you have a data problem, not a performance problem, and it is one an auditor will eventually surface.

What IATF 16949 actually asks you to track

IATF 16949 builds on ISO 9001's customer satisfaction clause (9.1.2), but layers on something automotive-specific: Customer-Specific Requirements, or CSRs. Every major OEM publishes its own CSR document plus a scorecard quick-reference guide through the IATF Global Oversight website, and these are updated regularly. GM, Stellantis, Ford and Geely all updated their CSR and scorecard guidance multiple times through 2025 alone.

In practice, this means an internal auditor preparing for your IATF audit needs to check your scorecard against whatever the OEM CSR currently requires, not against a static internal template built two certification cycles ago. That is a maintenance job most teams underestimate.

The OEM scorecards running in parallel to yours

It helps to actually look at how an OEM scorecard behaves. Stellantis publishes a detailed quarterly-updated guide for its own Bidlist scoring system. Each manufacturing supplier site starts every month with 100 points in each of two areas, quality and warranty, and points are deducted for specific disruptive events such as a withdrawn IATF certificate or a critical quality event. Crucially, if either the quality or the warranty score turns red, the supplier's overall Bidlist score is red. There is no averaging your way out of a single bad area.

GM runs a comparable system through SupplyPower, with its own "Sourceability" levels tied to production history and quality records, and Ford and Geely publish their own equivalents. None of these systems care what your internal scorecard says. They pull from OEM-side transaction and complaint data, independently of you.

How an OEM red flag can reach the IATF KPI Hub, and how a reconciled internal scorecard prevents it Supplier performance deliveries, defects, PPAP OEM scorecard Stellantis, GM, Ford, Geely IATF KPI Hub visible to your CB if red Internal scorecard reconciled with OEM CSRs CAPA / 8D triggered before OEM sees a drop

A reconciled internal scorecard catches a quality or delivery drop early, so corrective action closes it before the OEM's own scorecard turns red.

The metrics that actually carry weight

Strip away the acronyms and an automotive supplier scorecard comes down to a handful of numbers that OEMs, auditors and your own quality team all care about.

Parts per million (PPM) defect rate

A PPM rate below 500 is the commonly cited threshold for automotive and precision manufacturing suppliers, tighter than the roughly 1,000 PPM ceiling used in less regulated sectors such as food and beverage. Some OEMs set stricter internal targets. Champlain Cable's published supplier quality manual, for example, uses a 0 to 5 rating scale where an overall score below 2.25 automatically triggers a written corrective action plan from the supplier, a good illustration of how tightly PPM and quality scoring feed directly into corrective action.

On-time-in-full delivery (OTIF / OTD)

Automotive OEMs typically expect on-time delivery of 98% or higher, measured against the confirmed delivery date rather than the date you originally requested. One useful red flag pattern to watch for: a supplier with excellent OTD numbers but a rising rate of expedite requests. That combination usually means the supplier is quietly padding lead times to protect the metric rather than actually improving.

PPAP approval rate and cycle time

How often does a supplier's Production Part Approval Process package get approved on the first submission, and how long does it take? A supplier that repeatedly resubmits PPAP packages is telling you something about their internal process discipline well before it shows up as a defect on your line.

CAPA / 8D closure time

Speed and quality of root cause response. A supplier that closes an 8D in two weeks with verified containment and a documented root cause is a fundamentally different risk than one that takes three months and reuses the same generic "operator error" root cause every time.

MetricAutomotive benchmarkTypical scorecard weight
PPM defect rate< 500 (tighter for critical parts)15–20%
On-time-in-full delivery≥ 98%20–25%
PPAP first-time approvalTracked as a rate, target > 90%5–10%
CAPA / 8D closure timeTracked in days, trend over snapshot10–15%
IATF / CSR compliance statusCertified, no open major nonconformities10%

Reference ranges only. Weight by supplier segment, part criticality and your OEM's own CSR where one exists.

Building the scorecard: a six-step approach

  1. Segment suppliers first. A sole-source IATF-certified Tier 1 supplying safety-critical parts should not be scored on the same template as a commodity fastener supplier. Segmentation drives which metrics matter and how tightly to weight them.
  2. Pick five to seven metrics, not twenty. The useful test for any candidate metric is simple: does it answer the question "should we give this supplier more business?" If a number cannot influence that decision, it is vanity measurement and it should not be on the scorecard.
  3. Pull hard metrics from source systems. PPM, OTD and lead time should come from ERP and quality system transaction data, not from a self-reported form the supplier fills in. Self-reported numbers and the official audited score can diverge enough to trigger their own penalty under some OEM rules, so building on live data avoids that gap entirely.
  4. Overlay your OEM's CSR requirements. If Stellantis, GM or Ford already scores your supplier on quality and warranty, your internal scorecard's red threshold should trip before theirs does, not after. Build the reconciliation check in, do not treat it as a side project.
  5. Track trend, not just snapshot. A supplier moving from a score of 4.2 to 3.8 to 3.5 over three consecutive quarters needs intervention now, even though the latest number might still look technically fine on its own. The trajectory is the signal, not the single data point.
  6. Close the loop with a formal CAPA, not a color chip. A red status that just sits on a dashboard achieves nothing. It needs to trigger an actual corrective action workflow with an owner, a root cause investigation, and a verification step before the supplier is allowed back to green.

Do not turn the scorecard into a weapon

There is a real risk in over-engineering this. Veteran quality managers on industry forums have flagged for years that scorecards used purely to punish suppliers, rather than to build a shared improvement plan, tend to backfire: suppliers game the metric instead of fixing the underlying problem, and the relationship sours in ways that eventually cost the buyer more than the original defect did.

The IATF's own SPI guidance is explicit that continued certification of a genuinely poor performer damages the whole certification scheme's credibility, not just the individual supplier relationship. That is the framing worth keeping in mind: the goal of a scorecard is defensible, evidence-based accountability, not a scoreboard for its own sake. Paraphrased from IATF Supplier Performance Initiative guidance, via simpleQuE quality consulting

In practice, the fix is procedural. Pair every red or declining trend with a required improvement plan and a re-evaluation date, not just a penalty. Suppliers that see a scorecard drop trigger genuine support, engineering time, a joint root cause session, tend to recover faster and stay more transparent about problems going forward than suppliers who only see the scorecard when it is used against them.

Closing the loop: from scorecard flag to closed CAPA

Consider a simplified example. Axleworth Components, a fictional Tier 1 automotive supplier certified to IATF 16949, sees its PPM rate spike after a tooling wear issue on a stamped bracket. Under a reconciled scorecard, that spike trips an internal red flag the same week it happens, well before the parts reach the OEM's own quarterly Bidlist update. The buyer's quality team opens an 8D, Axleworth's engineering team identifies the worn tooling as root cause within days, containment ships correct parts, and a permanent corrective action (revised tooling maintenance interval) closes within three weeks. By the time the OEM's own scorecard cycle runs, the defect never shows up as a sustained trend, because it was caught and closed on the buyer's own timeline.

That is the actual point of connecting a scorecard to a CAPA workflow: not compliance theater, but genuinely catching a problem before someone else's system catches it for you. Platforms built for supplier performance management, including EvaluationsHub, combine weighted multi-stakeholder scorecards with a built-in CAPA workflow so a red flag can trigger a corrective action with one click rather than a separate email chain and a spreadsheet nobody updates.

A checklist before you go live

  • Metrics are pulled from ERP or quality system data, not self-reported by the supplier
  • Weights differ by supplier segment and part criticality, not a single template for everyone
  • Your red threshold is calibrated to trip before or in line with your OEM's CSR scorecard, not after
  • Scorecard trend, not just the latest snapshot, is visible to whoever makes sourcing decisions
  • A red or declining score automatically opens a CAPA or 8D, with an owner and a re-evaluation date
  • The scorecard process includes a supplier-facing improvement conversation, not just an internal report
  • Someone owns keeping the scorecard template current against OEM CSR updates, which change multiple times a year

Frequently asked questions

What is the IATF Supplier Performance Initiative?

A program run by the International Automotive Task Force, piloted with GM and Ford in 2019 and formally launched in March 2020, under which participating OEMs report suppliers rated "Red" on their own scorecards into the IATF KPI Hub, a database visible to IATF certification bodies.

What PPM defect rate is acceptable for an automotive supplier?

Below 500 defective parts per million is the commonly used threshold in automotive and precision manufacturing, though critical safety parts and specific OEM CSRs can set a tighter target.

How often should an automotive supplier scorecard be updated?

Monthly is standard practice, aligned with how most OEM scorecards, including Stellantis Bidlist scoring, refresh on a monthly cycle.

What happens if a supplier scores red on an OEM scorecard?

Depending on the OEM, a red status can trigger new business holds, mandatory corrective action plans, and under the IATF Supplier Performance Initiative, reporting into the IATF KPI Hub, which certification bodies review when planning audits.

See how EvaluationsHub handles automotive supplier scorecards

Weighted, multi-stakeholder scorecards, one-click CAPA triggers, and RFx and portal tools built for IATF 16949 supply chains.

Book a demo
Sources referenced
  • IATF Supplier Performance Initiative overview, simpleQuE quality consulting: simpleque.com
  • OEM scorecard quick reference guides (Stellantis, GM, Ford, Geely), IATF Global Oversight: iatfglobaloversight.org
  • IATF 16949 certification and audit practice notes, DQS: dqsglobal.com
  • AIAG Core Tools and supplier performance management training overview: aiag.org
  • Champlain Cable Supplier Quality Manual QCP-0010: champcable.com
  • Supplier scorecard KPI benchmarking guidance, Procurement Toolkit: procuretoolkit.com

EvaluationsHub Is Now ISO 27001 Certified

What our Information Security Management certification means for procurement teams trusting us with their supplier data.


We’re pleased to announce that EvaluationsHub has achieved ISO 27001 certification, the internationally recognised standard for Information Security Management Systems (ISMS).

For a platform built to manage supplier performance, risk, and ESG/CSRD compliance data, this isn’t a milestone we’re treating as a trophy. It’s a baseline — one that our customers and the procurement teams evaluating us should be able to take for granted.

What ISO 27001 Means in Practice

ISO 27001 is the global benchmark for how organisations manage information security. It doesn’t just assess whether security controls exist — it evaluates whether they’re embedded in the way a company operates, monitored continuously, and improved systematically.

Certification requires an independent audit of the entire ISMS: the policies, procedures, technical controls, and organisational practices that together protect the confidentiality, integrity, and availability of the data we handle.

What’s in Scope

Our certification covers the full EvaluationsHub platform and the operations behind it, including:

  • Access controls and identity management — role-based access, multi-factor authentication, and the principle of least privilege across all environments.
  • Encryption — data encrypted at rest and in transit, with key management policies aligned to current best practices.
  • Incident response — documented procedures for identifying, escalating, and resolving security events, with defined communication protocols.
  • Supplier risk management — because we ask our customers to evaluate their suppliers’ security posture, we hold ourselves to the same scrutiny.
  • Business continuity — disaster recovery planning, backup procedures, and tested restoration processes.
  • Continuous monitoring — logging, alerting, and periodic internal audits to ensure controls remain effective as the platform and threat landscape evolve.

Why This Matters for Procurement Teams

When procurement teams centralise their supplier scorecards, risk assessments, and ESG data on a platform, they’re entrusting it with operationally sensitive information — performance ratings, audit findings, corrective action plans, compliance documentation, sometimes commercial terms.

That data deserves the same rigour that procurement professionals apply to evaluating their own supply base. ISO 27001 certification provides independent verification that we meet that standard.

For organisations operating in regulated industries or preparing for CSRD reporting obligations, it also simplifies vendor qualification. ISO 27001 is widely accepted as evidence of a mature information security programme, reducing the due diligence burden during procurement of the platform itself.

A Floor, Not a Ceiling

We’ve always viewed security as a prerequisite, not a feature. The controls we certified against weren’t built for the audit — they were built into how we work from the start, then formalised and independently verified.

Certification is a point-in-time assessment, but the ISMS it validates is designed for continuous improvement. We’ll keep raising the bar as the platform grows, as our customer base expands across DACH and Benelux, and as the regulatory landscape around supplier data continues to evolve.

If you have questions about our security practices or would like to review our ISO 27001 certificate, reach out to us at team@evaluationshub.com.


EvaluationsHub is a supplier performance management platform for mid-market to enterprise procurement teams. Book a demo →