A practical selection guide for procurement teams who have outgrown spreadsheets, written for the person who will have to live with the decision.

By Prof. Dr. Bert Paesbrugghe, founder of EvaluationsHub and Associate Professor of Sales and Purchasing at IÉSEG School of Management. Last updated 20 November 2026. Reviewed twice a year.

The short answer

  • An SRM system (supplier relationship management) is the layer that holds the supplier relationship between transactions: qualification, scorecards, risk and sustainability data, corrective actions and improvement plans. It sits above the ERP, not inside it.
  • Choose on five things, in this order: supplier-side adoption, who runs the cadence, scoring flexibility per segment, what the pricing model does to participation, and time to first live score.
  • Feature-count comparisons predict almost nothing. Every serious vendor has scorecards. Very few make it painless for a supplier in a different country, with no training, to respond on time.
  • Insist on a real pilot with your own supplier data before signing. One complete evaluation cycle on five to fifteen suppliers tells you more than six demos.
  • If nobody owns the process, KPI definitions are not agreed, and no executive sponsors it, buying software will scale the confusion. Fix that first.

1. Name the problem before you shortlist

Most disappointing SRM purchases were decided before the first demo, at the moment somebody wrote a requirements list instead of writing a problem statement. A requirements list produces a feature comparison. A feature comparison produces the vendor with the longest feature list, which is rarely the vendor whose product your suppliers will use.

In practice, procurement teams shopping for an SRM system are solving one of three quite different problems, and they need different things from the software.

  • The measurement problem. You have supplier performance data, but it lives in seven places and every category manager scores by instinct. You cannot rank suppliers, you cannot show a trend, and you cannot defend a de-selection decision. What you need is a consistent scoring model and a mechanism that collects the inputs without a human chasing them.
  • The governance problem. An auditor, a customer or a regulator wants evidence that suppliers are evaluated, re-evaluated and acted upon. You need records, timestamps, ownership, and a clean trail from finding to closure. Beauty of dashboards is irrelevant. Completeness of the trail is everything.
  • The administrative problem. The work is happening, but it costs too much human time. Somebody spends four days a quarter building decks that are out of date by the time they are presented. Here the value is automation of the collection and follow-up loop, not analytics.

Write down which of these is costing you most this year, in the language your CFO uses. That single sentence will settle more shortlist arguments than any scoring matrix.

There is a fourth situation worth naming honestly: sometimes the answer is not to buy anything yet. If you manage fewer than roughly twenty-five suppliers with real strategic weight, if no one person owns supplier performance, or if the business has not agreed what “on time” means, a platform will formalise a process that does not exist. Spend a quarter agreeing definitions and ownership with a shared spreadsheet, then buy. The spreadsheet will fail visibly and quickly, and that failure is the business case.

2. SRM, SPM, SLM, S2P, TPRM: what the categories actually mean

The vocabulary in this market is genuinely confusing, and vendors have an incentive to keep it that way. Here are working definitions, written so you can use them in an internal paper.

Table 1. The five categories buyers most often confuse when shopping for supplier software.
CategoryCore jobGood fit whenWrong tool when
SRM
Supplier relationship management
Managing the ongoing relationship: engagement model, reviews, collaboration, improvement You have strategic suppliers whose performance and cooperation move your P&L You mainly need transaction control and invoice matching
SPM
Supplier performance management
The measurement engine inside SRM: KPIs, weighted scorecards, evaluations, corrective actions Scoring is inconsistent and reviews slip You need sourcing events and contract creation more than measurement
SLM
Supplier lifecycle management
One supplier record from intake and qualification through sourcing, contracting, performance and improvement Data keeps dying at the handover between stages You only have a single narrow gap to close
S2P
Source-to-pay
The full commercial chain including requisitions, purchase orders, invoices and payment Maverick spend and payment processes are the actual problem Your ERP already handles transactions and your gap is relationship management
TPRM
Third-party risk management
Screening and monitoring: sanctions, beneficial ownership, financial health, cyber posture Compliance and legal own the mandate You need continuous performance improvement, which these tools rarely close the loop on

Two clarifications that save weeks of internal debate. First, SPM is a component of SRM, not a competitor to it, and we set out the difference between SPM and SRM here. Second, source-to-pay is not a superset of SRM in any useful sense. A suite can cover the transaction chain end to end and still leave you with no structured way to score a supplier, agree an improvement plan and verify it closed. If you want the foundational definition first, start with our explainer on what supplier relationship management is.
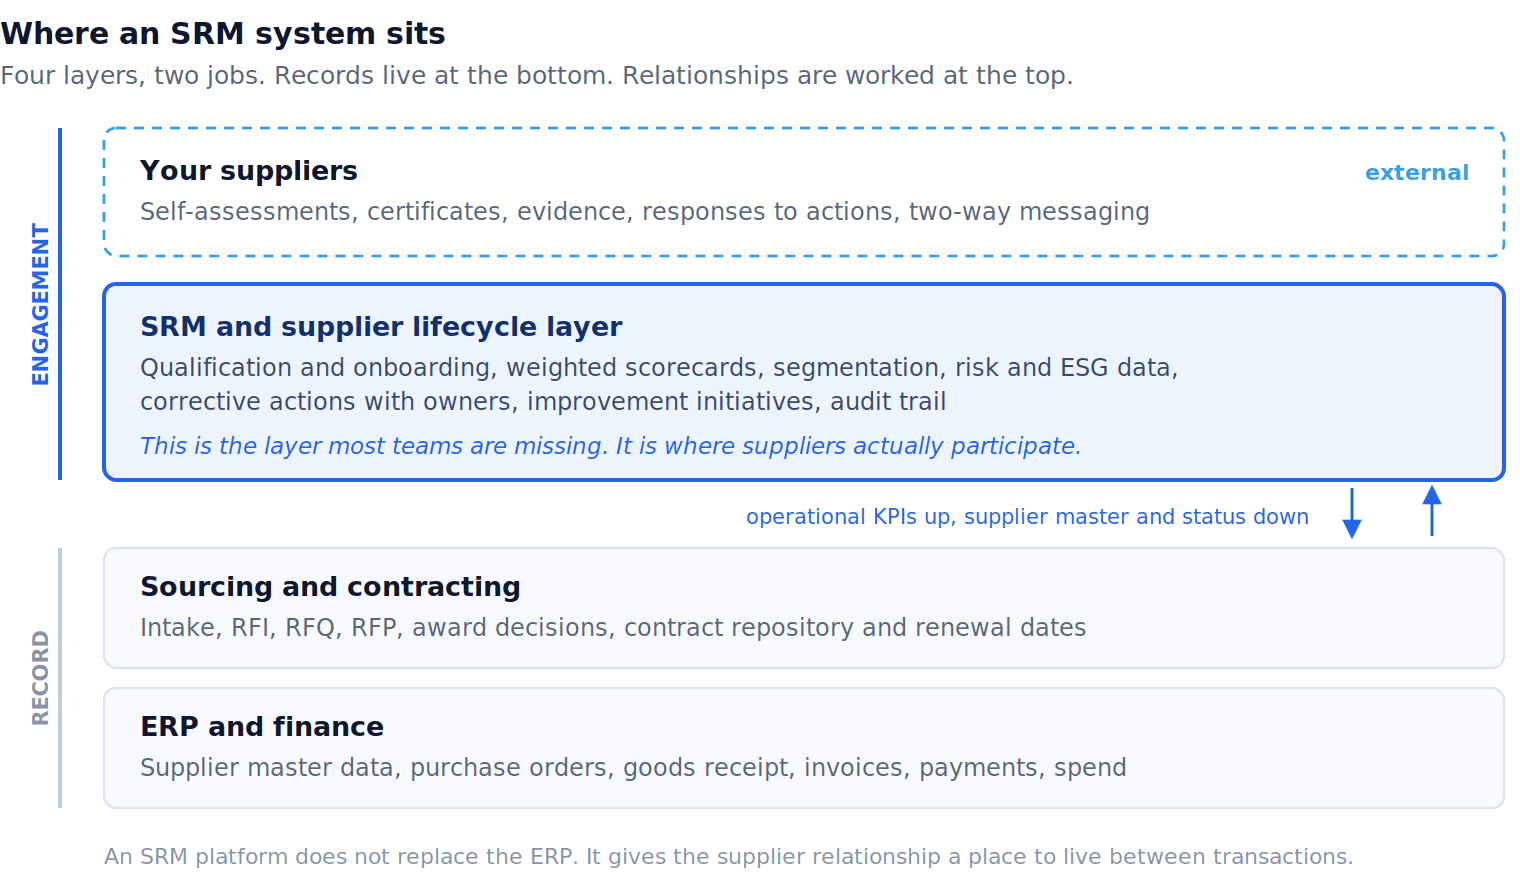
Four-layer diagram showing suppliers at the top, the SRM and supplier lifecycle layer below it, then sourcing and contracting, then ERP and finance
Figure 1. Where an SRM system sits. The ERP holds the records. The SRM layer is where the relationship is worked and where the supplier actually participates.

The layer diagram matters for one commercial reason. When the CFO asks why the ERP cannot do this, the honest answer is that the ERP holds transactions and master data brilliantly and has no concept of a relationship, a review cycle, or a supplier who needs to be persuaded to answer a questionnaire. Those live in a different layer, and it is a layer where supplier collaboration is the point rather than a side effect.

3. Which category do you actually need

Run this before you build a shortlist. It takes ten minutes and it disqualifies half the market.
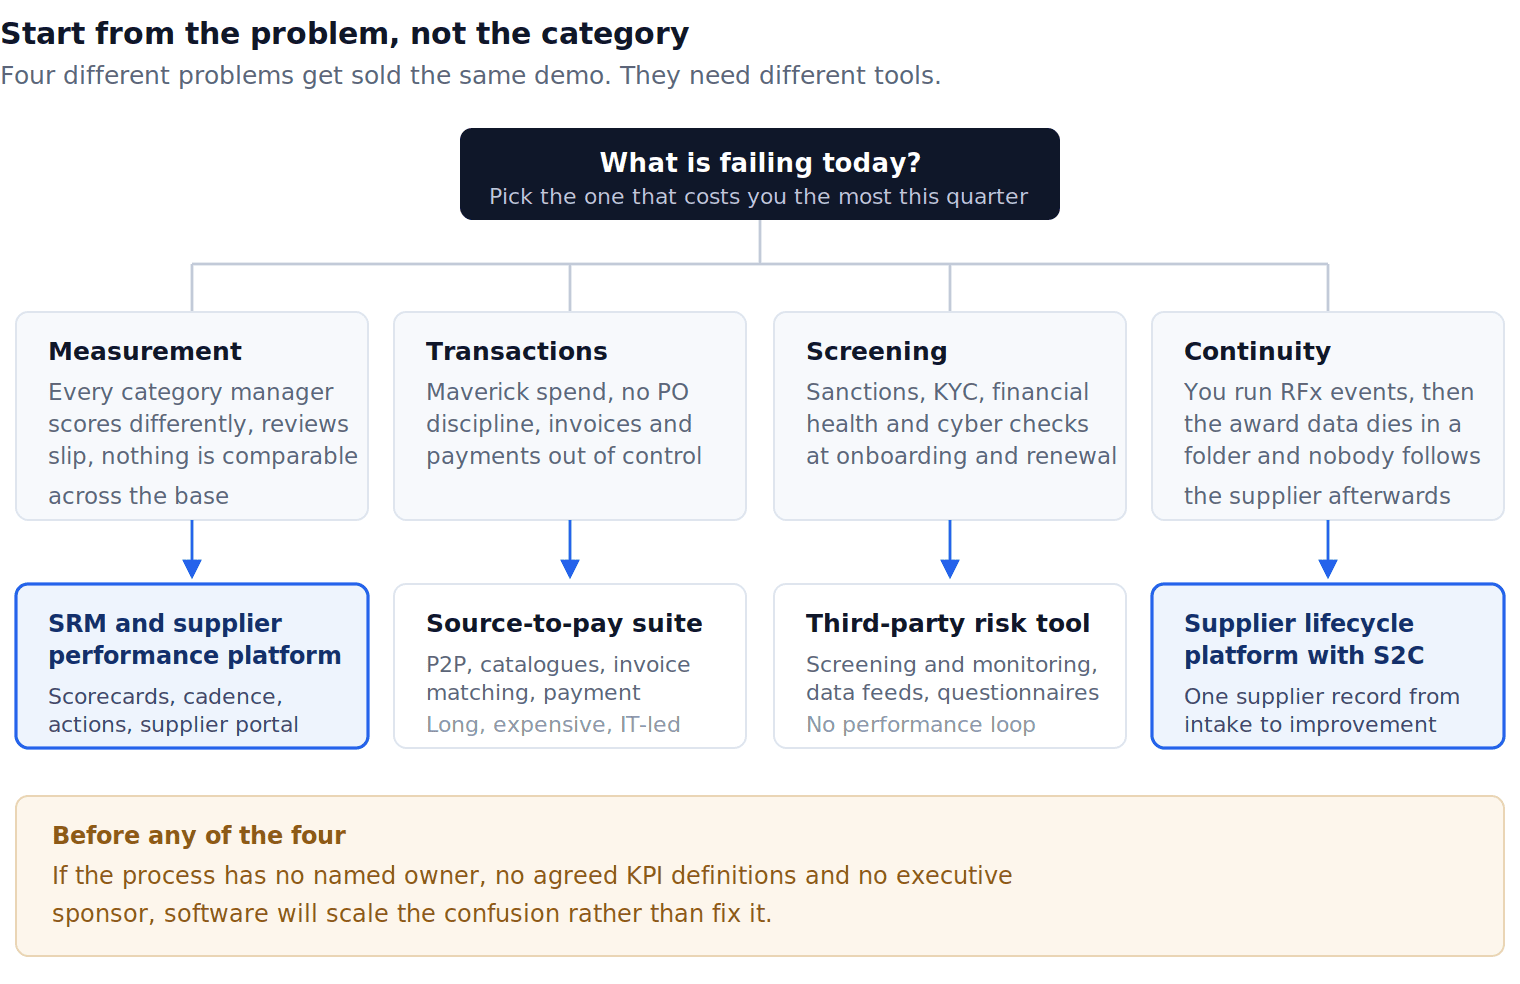
Decision tree routing four procurement problems to SRM, source-to-pay, third-party risk and supplier lifecycle platforms
Figure 2. Start from the process that is failing, not from the product category. Four common problems lead to four different classes of tool.

A note on combinations. Many mid-market teams discover they have two of these problems at once, typically measurement and continuity: they run sourcing events and they have inconsistent scorecards, and the award data never reaches the people who manage the supplier afterwards. That combination is the specific reason supplier lifecycle platforms exist, and it is worth asking whether one supplier record across sourcing and performance would remove more work than two best-of-breed tools with an integration between them. Our view on where sourcing tools end and lifecycle management begins goes deeper on that boundary.

4. The twelve criteria that predict success

These are ordered by how strongly they correlate with a programme still running two years later. The weights are a starting point. Adjust them, but keep the top four dominant, because they are the ones that fail silently.

01 Supplier-side adoption

The single most common cause of a stalled programme is that suppliers do not respond. Everything downstream depends on data arriving from organisations you do not employ, do not train and cannot discipline easily. Ask to see the supplier experience, not the buyer experience: the invitation email, the first login, the mobile view, the language options, what happens when the wrong person receives it, and how a supplier submits a certificate.

Evidence to demand: a live supplier-side login during the demo, plus the vendor’s actual response rate data from comparable accounts. If the supplier portal costs extra per supplier user, treat that as a structural problem, not a pricing detail.

02 Who runs the cadence

A scorecard tool stores scores. An SRM system runs the calendar: it sends the evaluation on schedule, chases the people who have not answered, escalates when a deadline passes and aggregates the result without anybody copying anything. The difference is roughly one full-time equivalent of administrative work per few hundred suppliers, and it is the difference between a programme that survives a busy quarter and one that quietly stops.

Evidence to demand: show me the reminder and escalation configuration, and show me the log of what the system sent last month without a human involved.

03 Scoring flexibility, and whether you can change it yourself

Your scoring model will change. It always does, usually in month four when quality argues that defects should carry more weight than delivery. The question is whether that change costs an email to support and a change request, or ninety seconds in the interface. Look for weighted scoring where weights are set per evaluation method, different methods running on different cadences, and a consistent scale. We use a scale out of 10 throughout, because a mixed set of scales is where comparability dies.

Evidence to demand: change a weight, add a question and re-run a score during the demo, without the vendor saying “our team can configure that for you”.

Supplier scorecard table with weighted evaluation methods, cadences, Kraljic segments and total scores out of 10 for four suppliers
Figure 3. The four things to look for on one screen in any scorecard demo. Supplier names are fictional.

04 Segmentation that actually changes the workflow

Sending a strategic supplier questionnaire to a stationery vendor is how you lose supplier goodwill and buyer time in one move. Segmentation, whether you use the Kraljic model from Peter Kraljic’s 1983 Harvard Business Review article or your own tiering, has to drive different templates, different cadences and different thresholds. Many tools let you tag a supplier as strategic and then treat it identically to every other supplier.

Evidence to demand: two suppliers in different segments, showing genuinely different questionnaires, review frequencies and alert thresholds.

05 The data model underneath

This is unglamorous and it decides whether the system still works in year three. Real supplier bases are messy: one legal entity with eleven plants, one group with three trading names, one contract covering four sites, one supplier that is also a customer. If the tool models a supplier as a single flat record, you will be creating duplicates within a month and your scores will not aggregate.

Evidence to demand: ask for the entity relationship model in writing. Suppliers to sites, sites to contracts, contracts to categories, users to roles. A vendor who cannot produce this quickly has not thought about it.

06 Closing the loop from score to action

A score with no consequence is a report. The system needs to turn a threshold breach into a task with an owner, a due date, required evidence and a verification step, then reflect the outcome in the next cycle. Ask specifically how the loop closes: who verifies, what evidence is stored, and whether the improvement is visible in the trend line.

Evidence to demand: follow one corrective action from trigger to verified closure in the product, including the supplier’s side of it.

07 Risk, certificates and sustainability data in the same record

Certificates expire, audits fall due, and sustainability questionnaires arrive from your own customers. If these live in a separate tool from performance, somebody reconciles two systems by hand. The practical test is whether an expiring ISO certificate can raise an alert and, if unresolved, affect the supplier’s status without a manual step.

Evidence to demand: an expiring certificate alert, and a sustainability questionnaire template you can edit rather than commission.

08 Integration realism

Ambitious integration plans are the most common cause of delayed go-lives. The mature pattern is to start with a file import of twelve months of history, prove the cycle works, then connect the systems that carry your operational KPIs. Ask what the vendor supports natively rather than what is technically possible, and get the effort estimate in days from someone who has done it. EvaluationsHub connects through native SAP and Salesforce sync via AWS AppFlow, a REST API with webhooks, and CSV or Excel import and export, which is documented on the integration capabilities page.

Evidence to demand: a named reference customer using the same ERP, and the field mapping document.

09 Governance, permissions and the audit trail

If procurement, quality, legal and finance all touch supplier data, you need role-based access with real segregation of duties, and an audit trail that records who changed a weight, who approved a score and when a document was uploaded. This is what turns your programme into evidence during an audit rather than an anecdote.

Evidence to demand: export an audit log. Look at whether it is readable by an auditor without a translator.

10 Pricing structure, not just price

Covered in detail in the next section, because it deserves it. In short: the unit a vendor charges on tells you what behaviour their product will encourage.

11 Security, hosting and exit

Ask where the data is hosted, under which certification, and how you get it out. EvaluationsHub is ISO/IEC 27001:2022 Certified, GDPR compliant and hosted on AWS in Paris (eu-west-3), with the detail on our trust center and data security page. Whoever you choose, put the exit clause in the contract at signature, not at renewal: full export of suppliers, scores, documents and audit history in a machine-readable format, on request, at no charge.

Evidence to demand: the certificate itself with its scope and validity dates, the data processing agreement, and a sample export file.

12 Time to first live score

The best single predictor of a programme surviving is how quickly it produces something real. A pilot that scores fifteen suppliers in week three creates internal advocates. A nine-month configuration project creates fatigue and a change of sponsor. Ask every vendor for the date of your first supplier-visible score, and hold them to it in the contract.

Table 2. A starting weighting for your own selection matrix. Copy it, argue about it internally, then score each vendor out of 10.
CriterionWeightFails silently?
Supplier-side adoption and ease of response15%Yes, six months in
Automated cadence, reminders and escalation15%Yes, in the first busy quarter
Self-service scoring and template configuration12%Yes, at the first model change
Segmentation driving differentiated workflow10%Yes
Data model, entities, sites and hierarchies10%Yes, in year two
Corrective action loop with verification10%No, visible quickly
Risk, certificates and sustainability in one record8%Partly
Integration effort and native connectors7%No, visible at go-live
Governance, permissions and audit trail5%Yes, at the first audit
Security, hosting, data residency and exit terms4%Yes, at renewal
Total cost of ownership across three years2%No
Time to first live score2%No

Two of those weights surprise people. Cost is deliberately low, because within a shortlist of credible platforms the price difference is usually smaller than the cost of a failed rollout. Time to first score is low as a weight but should be a hard gate: if it exceeds one quarter, the tool is heavier than your problem.

5. The pricing structure trap

The commercial model shapes the behaviour of your programme more than any feature. This is the part of SRM selection that almost nobody analyses properly.

Consider the most common model, per-user licensing. Multi-stakeholder scoring is the main defence against buyer bias: quality, operations, engineering, finance and the plant all see a different supplier, and the aggregate is far more accurate than one category manager’s view. Now price every one of those contributors at a few hundred euros a year. What happens is entirely predictable. Licences get rationed, participation narrows to procurement, and within a year you have an expensive single-scorer system with the same bias as the spreadsheet it replaced. Nobody decided this. The pricing model decided it.

Table 3. What each pricing model quietly optimises for.
ModelVendor incentiveEffect on your programmeQuestion to ask
Per named userGrow seat countStakeholders excluded, scoring narrows to procurement, suppliers kept outsideWhat does it cost to add fifty occasional internal reviewers and every supplier contact?
Per supplierGrow supplier coverageEncourages participation, but tail suppliers can get expensive at volumeWhat is the price at 250, 500 and 1,000 suppliers, and is there a free tier for tail vendors?
Percentage of spendGrow with your spendCost rises for reasons unrelated to the value deliveredWhat happens in a year when spend rises 30% and our usage is flat?
Module bundlesBundle everythingYou pay for modules you will not configure for two yearsCan we buy the performance module alone and add sourcing later on the same supplier record?
Quote on request onlyPrice on perceived budgetLong cycles, weak internal comparison, renewal surprisesWill you publish the price list we are being offered, and cap year-two uplift in the contract?

Our own answer to this is deliberate and structural rather than promotional: EvaluationsHub charges a platform fee plus a per-supplier fee that steps down with volume, with unlimited seats for internal users and supplier-side users, and the price list is published on the pricing page rather than gated behind a call. Unlimited seats is not generosity. It is the only pricing shape in which multi-stakeholder scoring survives contact with a budget holder.

6. Twenty-four questions to ask every vendor

Send these in writing before the demo and ask for written answers. The written answers are worth more than the demo, and the speed and specificity of the reply is itself a signal.

Supplier experience

  1. Show me the supplier’s first login, on a phone, in a language other than English.
  2. What percentage of invited suppliers complete their first evaluation, across your customer base?
  3. What does a supplier pay, and what do we pay per supplier user?
  4. Can suppliers see their own score and trend, or only our conclusion?
  5. How does a supplier submit evidence, and where is it stored afterwards?

Measurement and workflow

  1. Change a weight in front of me and re-run the score.
  2. Show me two segments with genuinely different templates and cadences.
  3. How are late responses chased, and by whom or by what?
  4. Show me a corrective action from trigger to verified closure.
  5. How do you aggregate scores from internal stakeholders and the supplier without one overwriting the other?
  6. Can a category, a plant and a group-level view all show the same underlying data correctly?

Data, integration and IT

  1. Send me the entity relationship model.
  2. Which connectors are native, and which require middleware or services?
  3. How do we import twelve months of history, and how long does that take in practice?
  4. Who owns the master supplier record if we also run a source-to-pay suite?
  5. Show me a sample export of everything we would take with us if we left.

Commercial and delivery

  1. What is our first supplier-visible score date, and will you write it into the order form?
  2. What is the total three-year cost including implementation, at our supplier count?
  3. What is the contractual cap on annual price increases?
  4. Which of your customers are closest to us in sector, size and supplier count, and may we speak to one without you present?
  5. What is your average implementation length for a customer our size, measured from signature to first live cycle?

Trust and continuity

  1. Which security certification do you hold, what is its scope, and when does it expire?
  2. Where is the data hosted, and can it stay in the EU?
  3. How many customers of our size have left in the last two years, and why?

On reference calls. Ask the reference one question that vendors cannot coach: “what does your team still do in a spreadsheet?” The honest answer maps the product’s real boundary far better than any feature list.

7. How to run the evaluation itself

Demos reward presentation skills. Pilots reward products. A structured pilot is the only reliable way to see what a platform is like on a Tuesday afternoon when a supplier has not replied and the plant manager wants an answer.

Run one full cycle, with your own data

Pick between five and fifteen suppliers that genuinely matter, including at least one that is currently underperforming. Load real history. Run one complete evaluation cycle end to end: send, chase, collect, score, review, open one corrective action, and close it. Anything a vendor pre-configures for you in a sandbox has been made to work in advance and tells you nothing about your Tuesday afternoon.

Score the pilot on process outcomes rather than impressions: response rate without human chasing, time from cycle start to complete scorecard, number of times you needed vendor support to make a change, and how many people outside procurement contributed a score. That last number is the one that predicts whether the programme has a future.
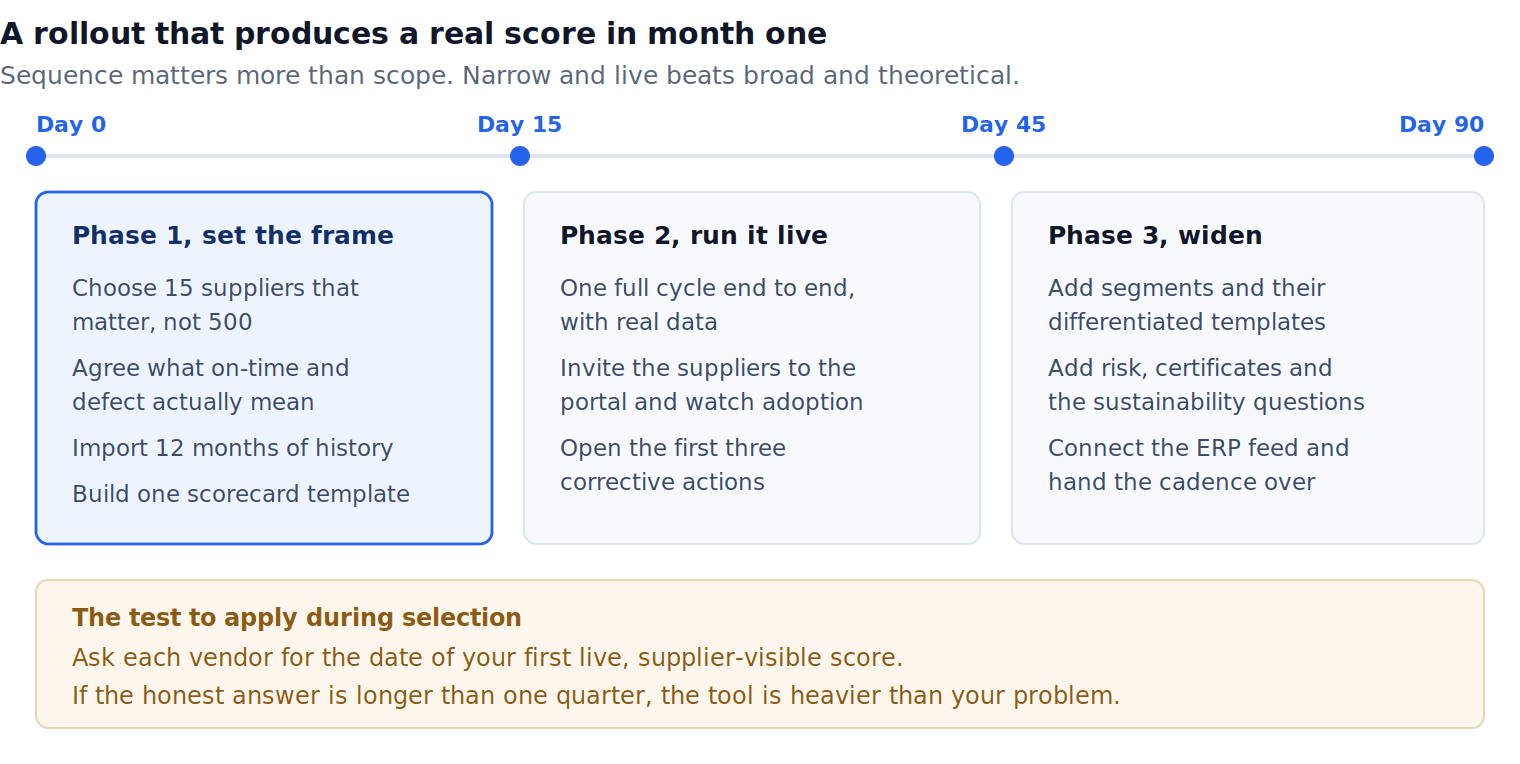
Three-phase timeline from day zero to day ninety for rolling out a supplier evaluation programme
Figure 4. A rollout sequenced so that a real, supplier-visible score exists in month one.

If you want to run that pilot with us. EvaluationsHub offers a free pilot with your own supplier data, up to three accounts and thirty seats, with no card and no commitment, at evaluationshub.co. If your current framework already lives in spreadsheets, we will rebuild it in the platform for you at no cost through white-glove onboarding, or you can book a working session with a procurement specialist rather than a sales development rep.

8. The full cost, not the licence fee

Build the three-year number before you negotiate, because it changes which vendor is actually cheapest surprisingly often.

Table 4. Cost lines to model across three years. The lines below the licence are where the surprises live.
Cost lineUsually quoted?What to ask for
Platform and per-supplier or per-seat licenceYesPrice at your supplier count today and at plus 50%
Implementation and configurationSometimesFixed price, with the first live cycle as the acceptance criterion
Data migration and history loadRarelyWhether import is self-service, and the format required
Integration build and maintenanceRarelyDays of internal IT effort, plus who maintains the mapping
Internal administrationNeverHonest estimate of the ongoing admin load in days per month
Supplier onboarding effortNeverWho writes the supplier communications, and in which languages
Training and turnoverRarelyCost of training a new category manager in year two
Annual upliftBuriedA contractual cap, in writing, at signature
Exit and data extractionNeverA no-charge full export clause in the contract

On the benefit side, be conservative and specific. Tie the case to things you can evidence: hours of administrative work removed, cycle time reduction, avoided cost from a supplier issue caught early, and audit preparation time. Broad savings percentages are easy to quote and hard to defend in a business case review. If you want a worked example with real numbers from a manufacturer of around 3,200 employees, our case study on evaluation cycle time shows the arithmetic.

9. Buy for the durable driver, not the deadline

A large share of SRM projects in Europe over the past three years were justified by a compliance deadline. That is a fragile business case, and 2026 proved it. The EU’s Omnibus package, published in the Official Journal on 26 February 2026, narrowed mandatory CSRD reporting to companies above 1,000 employees and 450 million euro net turnover, with the new scope applying to financial years starting on or after 1 January 2027. The due diligence directive was narrowed further still, to companies above 5,000 employees and 1.5 billion euro turnover, with application pushed out to 2029. Many mid-market manufacturers who bought tooling for a 2026 reporting obligation now sit outside the direct scope entirely.

Here is the nuance that matters for your decision. Falling out of direct scope does not remove the work. Your large customers remain in scope, and they meet their obligations by asking you and your suppliers for data. That flow does not depend on your own headcount. The same applies to the requirements that were never in the Omnibus at all: ISO 9001 clause 8.4 requires documented criteria for the evaluation, selection, monitoring and re-evaluation of external providers, and retained records of those activities and the actions arising. Automotive suppliers face the same expectation through IATF 16949. Those obligations are stable and they are the ones to build your case on.

The other durable driver is capacity. The Hackett Group’s 2026 Procurement Key Issues research found procurement workloads rising while headcount and operating budgets edge down, with technology spend expected to absorb the gap. If your team is being asked to cover more suppliers with the same people, automation of the collection and follow-up loop is a capacity argument, and capacity arguments survive changes in regulation and changes in sponsor.

Practical translation. Write the business case on administrative capacity and audit evidence. Treat sustainability reporting as a capability you will need whichever way the rules move, rather than as the deadline that justifies the purchase.

10. Red flags and green flags

Red flags in a vendor process

  • The demo never shows the supplier’s side of the product.
  • Every configuration change is answered with “our team can set that up for you”.
  • Pricing is only available after a discovery call, and the quote arrives without a unit price.
  • Reference customers are offered only with the vendor on the call.
  • The implementation plan measures progress in workshops rather than in live cycles.
  • Claimed integrations turn out to mean “possible via API” with no customer live on it.
  • The audit trail exists but cannot be exported in a form an auditor would accept.

Green flags

  • They ask about your supplier segmentation before they ask about your budget.
  • They are specific about what the product does not do.
  • They offer a pilot with your data rather than a longer sandbox trial with theirs.
  • Written answers come back fast and match what the demo showed.
  • They will commit to a first live score date in the order form.
  • Published pricing, or at least a published structure.

11. Where EvaluationsHub fits, and where it does not

We build one of the platforms in this market, so treat this section as informed rather than neutral, and hold it to the same tests as everyone else’s.

EvaluationsHub is a supplier lifecycle platform with source-to-contract capability. The evaluations module covers weighted scorecards, multi-stakeholder scoring, segmentation, risk and sustainability data collection, corrective action workflows and a white-labelled supplier portal that carries your brand rather than ours. The initiatives module covers intake, RFI, RFQ, RFP, contracting, onboarding and improvement programmes. Both modules run on one shared supplier record, and they can be bought independently. Founded in 2021 by Vockam SAS in Paris, the platform is used by more than 350 procurement teams, holds a 4.9 out of 5 rating on G2, is ISO/IEC 27001:2022 Certified and GDPR compliant, and is hosted on AWS in Paris.

Three design decisions are worth putting next to the criteria above. Seats are unlimited on both the internal and the supplier side, which is what makes multi-stakeholder scoring economically survivable. The cadence is run by the platform, which sends, chases, escalates and aggregates without procurement doing the chasing. Pricing is published rather than quoted. Where we go further than most scorecard tools is the shared cross-buyer supplier portal, which means a supplier already onboarded for another buyer is not starting from zero with you.

Where we are not the right answer. If your primary problem is requisitions, purchase orders, invoice matching and payment, you need a source-to-pay suite, and we do not handle POs, invoicing or payments by design. If you need continuous automated screening of sanctions lists, beneficial ownership and cyber posture as your central use case, a specialist third-party risk platform will do that better. If you manage twenty-five suppliers with one buyer, a well-designed spreadsheet and a recurring calendar invitation genuinely is enough, and we would rather say so than sell you a platform you will abandon.

Sector-specific detail lives on the pages for automotive, food and beverage, medical devices, pharma, specialty chemicals, aerospace and IT services. Consultancies running supplier programmes on behalf of clients should start with the advisory firms page.

12. The ten-step selection checklist

  1. Write the problem statement in one sentence, in the CFO’s language.
  2. Confirm the process owner and the executive sponsor by name.
  3. Agree KPI definitions with quality and operations before you shortlist.
  4. Use the decision tree to pick the category, then shortlist three vendors, not seven.
  5. Send the written questions before any demo.
  6. Score against a weighted matrix your stakeholders agreed in advance.
  7. Run a real pilot with your own data and at least one underperforming supplier.
  8. Model the three-year total cost, including internal administration.
  9. Negotiate the first live score date, the uplift cap and the exit clause together.
  10. Go live narrow, prove one cycle, then widen. Do not launch with 500 suppliers.

Templates for the scoring model itself, including weighted scorecard structures you can adapt, are in our SRM template library, and the longer strategic background is in the whitepapers.

13. Frequently asked questions

What is an SRM system?

An SRM system is software that manages the ongoing relationship with suppliers: qualification and onboarding, performance scorecards, risk and sustainability data, corrective actions, improvement plans and the collaboration between buyer and supplier. It complements the ERP, which records transactions and master data, by holding everything that happens between transactions.

What is the difference between SRM and SPM?

Supplier performance management is the measurement engine: KPIs, weighted scorecards, evaluations and corrective actions. Supplier relationship management is the wider discipline that includes measurement plus segmentation, governance, collaboration and development. In software terms, SPM is a module inside an SRM platform.

Can we not just use our ERP?

An ERP holds supplier master data and transaction history, both of which you need. What it generally does not provide is a supplier-facing portal, scheduled multi-stakeholder evaluations, weighted scoring configurable by segment, or a corrective action loop with evidence and verification. Most teams keep the ERP as the system of record and add an SRM layer above it.

How much does an SRM system cost?

Mid-market platforms are typically priced as a platform fee plus a per-supplier or per-user fee, and land somewhere between roughly 20,000 and 120,000 euro a year depending on supplier count and modules. The larger variable is implementation, which ranges from included to several times the annual licence. Always model three years including internal administration time, and get any annual uplift capped in the contract.

How long does implementation take?

A focused rollout should produce a first live, supplier-visible score inside a quarter, with a narrow first scope of ten to twenty suppliers. Full deployment across several hundred suppliers, multiple segments and an ERP integration usually runs six to nine months. If a vendor’s honest first-score date is beyond one quarter, the tool is probably heavier than the problem.

How many suppliers do you need before an SRM system is worth it?

There is no universal threshold, but the practical trigger is usually somewhere above 50 to 100 actively managed suppliers, or fewer than that when a small number of suppliers carry high risk, as in medical devices or aerospace. Below roughly 25 suppliers with one buyer, a disciplined spreadsheet and a calendar reminder is often the honest answer.

What is the most common reason SRM implementations fail?

Suppliers not responding, followed closely by nobody owning the cadence internally. Both are process failures that software can mitigate but not cure. This is why supplier-side experience and automated chasing should carry more weight in your selection than analytics or dashboard design.

Should we buy a suite or a best-of-breed SRM platform?

Buy the suite if your dominant problem is transactional control and your IT function will resource a long programme. Buy best-of-breed if your dominant problem is measurement, governance or administrative load, and you want a first live cycle this quarter. A common and sensible pattern is an S2P suite for transactions with a dedicated SRM layer above it for relationships and performance.

Do we still need sustainability data collection after the EU Omnibus changes?

Very probably, even if you are now outside the direct reporting scope. Companies that remain in scope satisfy their obligations by requesting data from their value chain, so mid-market suppliers continue to receive questionnaires from their customers. Build the capability, but write the business case on capacity and audit evidence rather than on a specific reporting deadline.

What should a supplier scorecard actually contain?

Between four and seven weighted evaluation methods, each on its own cadence, scored on one consistent scale, with weights summing to 100 percent and differentiated by supplier segment. Typical methods are on-time delivery, quality, compliance or audit results, responsiveness, cost performance and sustainability. Each method needs an agreed definition and a named data source before the first cycle.

About the author. Prof. Dr. Bert Paesbrugghe is the founder and CEO of EvaluationsHub (Vockam SAS, Paris) and a permanent Associate Professor of Sales and Purchasing at IÉSEG School of Management, with guest professorships at Ghent University and the Luxembourg School of Business. He holds a PhD from Vlerick Business School and received the American Marketing Association’s Best Dissertation Award in 2018. He is the author of The Buyer’s Balance and co-author of The Buyer’s Code, a research report based on 203 interviews with B2B buyers.

Questions about anything in this guide, including the parts that are unflattering to our own product, can go to bert.paesbrugghe@evaluationshub.com.

For most of the last twenty five years, supplier controls were something an FDA investigator reached on the way to something else. The Quality System Inspection Technique organised an inspection around four subsystems, and purchasing was not one of them. FDA’s own QSIT guide names them plainly: “Management Control; Corrective and Preventive Actions (CAPA) (with satellites Medical Device Reporting, Corrections and Removals, and Medical Device Tracking); Design Controls; and Production and Process Controls (P&PC) (with satellite Sterilization Process Controls).” Purchasing controls appears in that guide as a linkage, something the investigator checks while evaluating design or production, for example by verifying “purchasing controls and receiving acceptance activities regarding at least one component or raw material.”

That is no longer how it works. Since 2 February 2026, part 820 has incorporated ISO 13485:2016 by reference, and FDA inspects against a new compliance program, 7382.850. That program replaces the four subsystems with six QMS Areas, and one of them is Outsourcing and Purchasing. In the most common inspection model, the investigator evaluates at least one element in every one of the six.

Read that again, because it is the part most coverage has skipped. Supplier controls have moved from an area an investigator might reach to an area the inspection design says they will open. Every time.

This piece is for the people who own those files: supplier quality engineers, supplier quality managers, and the vendor management teams who sit alongside them. It sets out what genuinely changed, what only moved from one document to another, and what a well kept supplier file now needs to contain. If you are outside medical devices, the last section explains what transfers, because the underlying shift is not really a device story. And if you want the wider picture of how supplier management works in this sector first, our SRM for medical devices page is the place to start.

What changed, and what only moved

There is a lot of writing about the QMSR that reads as if every supplier requirement was rewritten. Most of it was not. The honest picture is that a small number of requirements genuinely tightened, a larger number were already familiar to anyone who held an ISO 13485 certificate, and one protection quietly disappeared.

Here is the comparison that matters for supplier controls.

TopicUnder the old QSR (21 CFR 820.50)Under the QMSR (ISO 13485:2016 clause 7.4)Genuine change?
Evaluating and selecting suppliersManufacturers had to “Evaluate and select potential suppliers, contractors, and consultants on the basis of their ability to meet specified requirements, including quality requirements. The evaluation shall be documented.”Criteria for evaluation and selection, based on the supplier’s ability to meet requirements, with records keptMostly moved. The obligation is the same shape.
How much control to applyType and extent of control defined “on the basis of the evaluation results”Control proportionate to the risk the purchased product carries for the deviceYes. Risk is now the explicit yardstick.
Records of acceptable suppliers“Establish and maintain records of acceptable suppliers, contractors, and consultants.”Records of evaluation, plus re-evaluation and ongoing monitoringPartly. The monitoring expectation is firmer.
Change notification from the supplierPurchasing documents should, “where possible”, include an agreement that the supplier notify changesAn agreement that the supplier notifies changes before implementing them, scoped as applicable to the itemYes. From a best effort to a stated expectation with timing attached.
Verifying what arrivesHandled through acceptance activities elsewhere in the QSRVerification of purchased product, with the extent tied to riskMostly moved, with a clearer risk link.
Supplier audit reports during an inspectionShielded. Section 820.180(c) exempted them from routine FDA reviewNo such exemption existsYes. This is the largest single change.

Three rows carry the weight. Take them in turn.

Risk became the yardstick, not the evaluation result

The old rule asked you to set the type and extent of control on the basis of the evaluation results. In practice that produced a common pattern: a supplier scored well on the questionnaire, so they got light oversight, and a supplier scored poorly, so they got heavy oversight. It is a sensible instinct, but it measures the supplier rather than the exposure.

ISO 13485 asks a different question. The level of assessment and monitoring should be proportionate to the risk the purchased product carries for the device. A supplier with an immaculate record who makes a component in the patient contact path is not a low control supplier because they score well. They are a high control supplier who happens to perform well, which is a much better place to be, and the file should say so.

This is a distinction worth making out loud internally, because it changes who gets attention. If you already run risk based supplier segmentation, you have the machinery. What usually needs work is making the link legible: the tier, the reason for the tier, and the control activities that follow from it, all in one place rather than inferred across three systems. Our note on supplier segmentation models covers the tiering logic, and risk based supplier segmentation covers how to make the segmentation defensible rather than historical.

Change notification grew teeth

The old text was gentle. Purchasing documents should, where possible, include an agreement that the supplier notify the manufacturer of changes to the product or service that may affect the quality of the finished device. “Where possible” is an easy phrase to satisfy with a clause nobody monitors.

ISO 13485 asks for purchasing information to include, where the nature of the item makes it applicable, a written agreement that the supplier gives notice of changes before implementing them. Two independent readings of the clause agree on that shape, and both note the scoping. The standard itself is paywalled, so we are paraphrasing rather than quoting, and we would encourage anyone writing the clause to read clause 7.4.2 in their own copy.

The word doing the work is “before”. A notification that arrives with the shipment is not notice, it is news. Which means the clause is only as good as two things you control: a stated notice period per category, and a turnaround commitment of your own. A supplier who tells you about a resin change ninety days early and hears nothing for eleven weeks learns quickly that early notice costs them time and buys them nothing.

We wrote about how to draft clauses like this so they can actually be measured in supplier quality agreements: write clauses you can actually measure. The short version is that every clause needs a named record, a named owner and a review point, and change notification is the clause where that discipline pays back fastest.

The shield came down

This is the change with the sharpest practical edge, and FDA states it without ambiguity. Asked whether it can now review audit records, the agency’s QMSR FAQ answers: “Yes. The QMSR gives the FDA the authority to inspect management review, quality audits, and supplier audit reports. The exceptions that existed in the QS regulation at § 820.180(c) are not maintained in the QMSR.”

Supplier audit reports were, for a long time, one of the few places a quality team could write with complete candour. That is no longer the position. The useful response is not to write blander audit reports, which would waste the instrument. It is to close findings on the timeline your own procedure promises, so that any report an investigator reads comes with its closure evidence attached.

An open finding from fourteen months ago is a problem whether or not anyone reads it. What changed is only whether anyone reads it. Teams that already run supplier findings through a tracked corrective action loop are in good shape here; teams that keep audit findings in a spreadsheet beside the report are the ones with work to do. Our pages on supplier CAPA and corrective actions and digital supplier audits both deal with keeping the finding and its evidence in one thread.

Pull three supplier files

The fastest way to know where you stand is not a gap assessment. It is to pick three suppliers and open their files as an investigator would.

Choose them deliberately: one supplier of a component in the highest risk path, one supplier you onboarded in the last twelve months, and one long standing supplier nobody has looked at in years. That third one is where the interesting findings live.

For each, ask whether the file answers these questions without anyone having to go and ask a colleague.

QuestionWhat should be in the fileCommon gap
Why is this supplier approved?The evaluation record, with the criteria used and the dateApproval exists, criteria do not, or the criteria are a form with no thresholds
Why do they get this level of oversight?The risk tier, the reason for it, and the control activities it drivesTier is in a different system from the file, or was set once and never revisited
What exactly are they making, and where?The parts and the named manufacturing site, with datesParts sit in the ERP, sites are in nobody’s system
What did we agree they would tell us?The quality agreement, with the change notification clause and notice periodAgreement exists, notice period is “promptly”
Have they told us anything, and what did we do?Change notifications received, with the review and the decisionNotifications arrive by email to one person
How have they performed?Scorecard history, with the metric definitions usedScores exist, definitions are disputed
What did the last audit find, and is it closed?Audit report, findings, evidence of closure, datesReport filed, closure evidence elsewhere or absent
When is the next look scheduled, and why then?The re-evaluation date and the rule that set itAnnual for everyone, regardless of risk

If three files answer all eight, you are in genuinely good shape and the rest of this is confirmation. If the third supplier answers four, you have found the work, and you have found it in a form you can cost.

Two of these deserve a note. The question about parts and sites is the one most likely to produce a blank look, because supplier records are almost always organised per vendor while the questions asked of them are about products. We set out how to build the supplier, site and part layer properly in the data model that answers product level questions. And the last question, on timing, is the one where “annual for everyone” quietly contradicts the proportionality principle the QMSR just made explicit. Building a cadence suppliers can earn sets out a merit based alternative.

Why this is good news for supplier quality teams

It is tempting to read a new inspection program as pure downside. We would argue the opposite, and not as a consolation.

Supplier quality has always been an unusually hard function to resource, because its best work is invisible. A change caught before it reached production, a second source qualified before it was needed, a finding closed before it became a complaint: none of these generate an event anyone outside the team sees. Budget follows visible things.

Outsourcing and Purchasing being one of six named areas in the inspection program changes that arithmetic. The work is now structurally visible to the regulator, which makes it structurally visible internally. A supplier quality manager asking for a system rather than a spreadsheet has a much shorter conversation in 2026 than they had in 2024, and the argument does not need to be dramatic. It is simply that the files will be opened, so they should be worth opening.

There is a second benefit that is easy to miss. Because part 820 now points at ISO 13485:2016, the file that satisfies an FDA investigator is very close to the file that satisfies your notified body under EU MDR, and very close to the file your ISO 13485 certification audit already looks at. One well built supplier record serving three audiences is a better outcome than three overlapping ones, and it is the same collect once, report many principle that applies across the EU supply chain regulations. For teams running both markets, that convergence is the quiet win of the whole exercise.

What good looks like in the record layer

None of this requires a large programme. It requires that a handful of things stop living in email and start living somewhere with a date attached.

The change notification intake is the clearest example. A clause requiring notice before implementation creates an inbound flow, and an inbound flow with no defined destination becomes one engineer’s inbox. What it needs is an entry point suppliers can use without asking who to email, a triage step, a record of the decision, and a timestamp on each. That is the whole mechanism, and it is the difference between a clause you can evidence and a clause you can only assert. A supplier portal is the ordinary way to give that flow a front door, and automated follow up is what stops the triage step from depending on someone remembering.

The same logic applies to the other records in the eight question table. The audit finding and its closure evidence belong in one thread, not two systems. The risk tier belongs next to the controls it justifies, not in a separate segmentation file. The evaluation criteria belong with the evaluation, so that a decision made three years ago can still be explained by someone who was not there. Moving from annual reviews to continuous monitoring is what keeps those records current rather than merely complete. Supplier information management is the shape of that, and a full audit trail is what turns a set of records into something you can hand over.

If your supplier records currently live across a shared drive, a questionnaire tool and a spreadsheet of approvals, the honest first move is consolidation rather than sophistication. Replacing spreadsheets for supplier management covers that step without overselling it.

If you are not a device manufacturer

The specific rule is a device rule. The pattern is not.

Regulators and standards bodies have been converging for several years on the same idea: that oversight of external providers should scale to the risk those providers introduce, and that the oversight should be evidenced rather than asserted. The control of external providers in ISO 9001:2026 carries the same logic into general manufacturing. IATF 16949 has long expected it in automotive, where the scorecard requirements are unusually specific. The pharmaceutical equivalents sit in GMP chapter 7 on outsourced activities, and our SRM for pharma page covers how that plays out in practice.

So the three file test transfers directly. Pick three suppliers, open their files, and see whether each one explains why the supplier is approved, why they get the oversight they get, what you agreed they would tell you, and what happened the last time they told you something. If those four questions have answers with dates on them, the regulatory framework you happen to sit under matters much less than you would think.

Frequently asked questions

Does the QMSR require a supplier quality agreement? Not in those words. The requirement is that purchasing information includes an agreement, where applicable to the item, that the supplier gives notice of changes before implementing them. A quality agreement is simply the most practical place to put that, along with the metric definitions and the mutual obligations that make it workable. FDA’s own guidance on quality agreements in contract manufacturing recommends keeping them separate from commercial terms.

Do we have to requalify every supplier because of the QMSR? No, and any vendor telling you otherwise is selling something. Most of the evaluation and selection obligation moved rather than changed. The work is more usually in making existing decisions explainable: recording why a tier was set, attaching criteria to evaluations that have none, and closing audit findings that are open past their own due date.

Does FDA really read supplier audit reports now? The exemption that protected them at § 820.180(c) is not carried into the QMSR, and FDA has said directly that it has the authority to inspect them. Whether a given investigator asks for a particular report is a separate question from whether they may. Plan on the basis that they may.

We hold ISO 13485 certification already. How much of this is new? Less than for a company that ran purely to the QSR. The clause 7.4 obligations will be familiar. The genuinely new elements are the inspection structure, which puts Outsourcing and Purchasing on the agenda every time, and the loss of the audit report exemption, which is a US inspection matter rather than a standards matter.

Where should we start if the files are in poor shape? With three files, not with all of them. The three file test tells you which of the eight questions fail across different supplier types, and that tells you whether your problem is records, structure or cadence. Those are three different projects with three different costs, and guessing between them is how supplier programmes get oversized.


If you would like to see what a supplier record that answers all eight questions looks like in practice, our supplier performance pilot runs on a subset of your supply base so you can judge it against your own files, or you can book a demo and bring the awkward third supplier with you.

Since 1 October 2026, an importer bringing covered steel into the European Union has to be able to show where that steel was melted and poured, and show it with a document that carries the heat number. The rule is short, it is already in force, and it has a one year grace period attached to it that most teams will only notice once it has expired.

The useful part, for anyone who manages suppliers rather than customs declarations, is that the document in question is one your organisation very probably already receives. Commission Implementing Regulation (EU) 2026/1963 did not invent a new certificate. It took a document the steel trade has used for decades and made it the evidence that clears a border. So this is not a data collection project. It is a filing and retrieval project, and those are cheaper.

This piece is written for the supplier quality and procurement side of that work: which document, from whom, stored where, retrievable by whom, and what to put in a purchase order this quarter so the question stops coming up.

The sentence that makes this worth an hour of your time

Article 2(3) of the Regulation is one line long:

Failure to declare the country of ‘melt and pour’ with appropriate verifiable evidence as defined under Articles 1 and 2 shall lead to a rejection of the import.

That is a supply interruption with a documentary cause. It is the kind of risk that is almost free to remove in advance and expensive to resolve at a port, which makes it a good candidate for the small amount of preventive work described below.

What the Regulation actually asks for

Two facts, in one document. Article 1(1):

At the moment of import into the Union, importers of products falling under categories listed in Annex I to Regulation (EU) 2026/1384 shall provide a Mill Test Certificate that includes the country of ‘melt and pour’ and the heat number of the imported steel.

Regulation (EU) 2026/1384 of 17 June 2026 is the parent instrument, addressing the trade effects of global overcapacity on the Union steel market. Its Annex I lists steel product categories identified by Combined Nomenclature codes: hot rolled sheet, cold rolled sheet, stainless products, bars, wire rod, tubes and pipes among them. If you import any of those, the rule is yours to satisfy. If you buy from an EU supplier who imports them, it reaches you as a document request and a lead time question, which is the distinction drawn out below.

“Melt and pour” has a precise meaning in the parent regulation. It is the original location where raw steel or iron is first produced in liquid form in a steel or iron making furnace and then cast into its first solid state. Not where it was rolled. Not where it was cut, coated, galvanised or formed. The furnace.

Two points are worth drawing out, because both are good news.

The Regulation names the Mill Test Certificate and does not define it by reference to any standard. There is no clause requiring a European certificate format. A mill in Korea, Turkey, India or Brazil that issues its own certificate carrying the country of melt and pour and the heat number has issued an acceptable document. You are not asking anyone to reissue paperwork in a new form. You are checking that two fields are present.

The Commission chose this document precisely because it is already in circulation. Recital 9 explains that the Mill Test Certificate is the document “most widely recognised as the primary means of evidencing the country” and is “already being requested when exporting steel to some other non-Union countries.” The regulatory ask and the existing commercial practice point the same way, which is a more comfortable position than most compliance work starts from.

The one year window, and the better way to spend it

Article 3 sets the clock:

This Regulation shall enter into force on the day following that of its publication in the Official Journal of the European Union. It shall apply as from 1 October 2026. However, Article 1(3) shall apply from 1 October 2026 to 30 September 2027.

Article 1(3) is the flexible route. Where no Mill Test Certificate can be provided, eight other document types may be accepted on their own, as long as they carry the country of melt and pour and the heat number:

(a) invoices; (b) delivery notes; (c) quality certificates and clauses in implemented purchase orders or contracts; (d) long-term declarations from suppliers; (e) cost accounting and production documents; (f) customs documents from the exporting country; (g) commercial correspondence; or (h) production descriptions.

Recital 12 is explicit about why: a one year allowance lets economic operators progressively adjust their practices. The Commission has given the trade twelve months of tolerance on purpose.

Here is the part worth saying plainly. The standalone route expires. A purchase order clause does not. The temptation is to use the year as cover, defaulting to delivery notes and supplier declarations because they are easier to get, and to arrive at 30 September 2027 having built a process that stops working the following morning. The better use of the same twelve months is to spend them making the Mill Test Certificate arrive automatically, and to keep the Article 1(3) list in your back pocket for the handful of shipments where it genuinely does not.

After 30 September 2027 those eight document types are still useful. They stop being standalone evidence and become complementary evidence, which is what Article 1(2) provides for when a certificate exists but is missing one of the two fields. That is a real and permanent role for them. It is just not a substitute for the certificate.

The reconciliation nobody has run yet

Most organisations affected by this already hold the document. What they do not have is the document in the shape the declaration needs. Running these two columns against each other is the whole exercise, and it usually takes an afternoon.

What the quality file holdsWhat the declaration needs
A certificate per supplier, filed by vendorA certificate per heat, retrievable by shipment
Filed on receipt, opened at auditAvailable at the moment of customs declaration
Owned by quality or goods receiptNeeded by customs, trade compliance or the broker
Checked for chemical composition and mechanical propertiesChecked for country of melt and pour and heat number
Good enough as a PDF in a folderNeeds the melt and pour country as a declared value, via TARIC document codes
Covers the material gradeCovers this consignment of this material
Kept because the standard asks for itKept because the border asks for it

The last two rows are where the work is. Article 2(2) states that the country of melt and pour is declared by means of TARIC document codes, which means it is not enough for the certificate to exist somewhere in your building. Somebody has to read a value off it and put that value in a field, per consignment, on time. Your customs team or broker will have the current code values; they change and they are not worth copying into a blog post.

That is a handoff between two functions that, in most mid-sized manufacturers, have never needed to speak to each other about a document. Quality holds it. Customs declares it. Neither owns the gap. This is the same structural problem as a supplier notification that nobody opens, pointed at a different pair of desks, and it responds to the same fix: name the owner of the handoff, not just the owner of each side. If your evaluation and compliance records already support cross-department collaboration, and your audit trail records who received which document and when, this is a small configuration job rather than a new process.

Why this obligation is a different shape from the others

Every supplier data obligation covered on this site so far attaches at one of two levels. Some attach to the company: certificates, policies, headcount, the certificate transition records you keep per vendor, and most of what sits in supplier master data today. Some attach to the product or the site, which is why a supplier register organised purely by vendor struggles with them, and why the supplier, site and part data model is worth building before a regulation forces the issue.

The heat number is a third level, below both. It identifies a batch of liquid steel from a single furnace charge. One purchase order can span several heats. One heat can be spread across several purchase orders and several customers. It is the finest grain of supplier data that any EU instrument has yet asked a buyer to hold.

And it has a second property that makes it genuinely new: the heat number is created by your supplier’s supplier. You almost certainly do not buy from the mill. You buy from a service centre, a stockholder, a distributor or a parts maker, and the certificate you need was issued one or two tiers upstream of your contract. The document has to travel down the chain to reach you, which means your direct supplier’s job is not to produce the information but to pass it through intact.

That distinction matters commercially, because it changes the tone of the request. You are not asking a distributor to generate data they do not have. You are asking them to forward a document that came with the coil. Framed that way, the request is reasonable, cheap for them to satisfy, and much more likely to be met. A supplier portal that lets them upload the mill document against the purchase order, once, removes most of the remaining friction. Request design is the single biggest driver of whether supplier data arrives at all, which is covered at length in what actually lifts supplier response rates.

It also sets a clear standard for what counts. A buyer-published supplier specification from the drive technology manufacturer Dellner Bubenzer states the position in one line: “Only inspection certificates issued by the original manufacturer are allowed.” A distributor’s own restamped summary of a mill certificate is a different document from the mill certificate. Worth knowing before you accept one.

Two positions to be in, and only one of them is yours

Work out which one applies before you do anything else. It takes a spend report and an import list, and no supplier contact at all.

You are the importer. You bring covered steel or covered steel products into the Union yourself. The evidence obligation is yours, the declaration is yours, and the rejection risk under Article 2(3) is yours. Your job is to make the certificate arrive with the goods, every time, and to make the melt and pour country reach whoever files the declaration.

Your supplier is the importer. You buy from an EU service centre or an EU parts maker who imports the raw material. The obligation sits with them. What reaches you is a document request and, occasionally, a lead time conversation, because a supplier who cannot evidence melt and pour cannot clear the material they were going to make your parts from. This is worth a line in your supplier risk view rather than a project: an EU supplier heavily dependent on imported steel in the Annex I categories now has a documentary dependency that did not exist in September 2026. It is exactly the sort of signal third party risk scoring should pick up and most models do not yet carry.

Many organisations are in both positions at once, for different parts. That is normal, and it is the usual reason a role recorded against the vendor rather than against the buying relationship goes quietly out of date. The useful record is per material per sourcing route, not per supplier.

The lever that works better than a chase

The cheapest way to make a document arrive reliably is to stop asking for it and start owing something for it.

The Dellner Bubenzer specification mentioned above does exactly this, and publishes it. It states that the inspection certificate “is part of the scope of supply”, that it “must be received by the time of delivery at the latest”, and then adds the sentence that does the actual work: “invoices cannot be settled until the APZ 3.1 is received.” The same document requires parts to be physically marked with the heat number, by steel stamp, engraving or etching pen, so the material and its certificate cannot drift apart on a shop floor.

None of that is novel, and none of it needs a regulation to justify it. It is simply a purchase order term that converts a recurring chase into a condition both sides understand from the start. If you write one thing into your terms this quarter, write that: the mill test certificate carrying country of melt and pour and heat number is part of the scope of supply, due no later than delivery, and a condition of invoice settlement.

A clause like this is only as good as the record behind it, which is the argument made in full in writing supplier quality agreement clauses you can actually measure. One clause, one record, one owner, one review point. A certificate requirement with no named field to store the result in is a wish.

Published stockholder guidance is worth reading alongside your own terms. The UK stockholder West Yorkshire Steel describes a 3.1 inspection certificate as one issued by “the manufacturer of the steel” which “will show the cast/heat number, material size or thickness and the chemical composition”. That is the shape of the document to expect, described by someone who issues them daily.

A ten field certificate record

If you are going to store this properly, store it so the four questions below can each be answered with one filter. The fields are a starting point, not a benchmark, and most of them already exist somewhere in your systems, usually spread across supplier information records, goods receipt and a shared drive.

FieldWhy it earns its place
Heat numberThe identifier everything else hangs from, and the one the Regulation names
Country of melt and pourThe declared value. Not the country of shipment, not the country of rolling
Issuing mill, with plant name and locationThe certificate is issued by a named works, not by a company
Certificate type and referenceWhat you received, so a restamped summary is visibly not a mill certificate
Direct supplierWho you bought from, which is usually not the mill
Sourcing routeMill direct, service centre, stockholder, parts maker. Changing route changes the document path
Material grade and specificationWhat the quality function cares about, and the reason the file already exists
Purchase order and consignment referenceThe link that makes the certificate retrievable by shipment rather than by vendor
Document received date and received byThe evidence that the clause in your terms is being honoured
Melt and pour value declared, with dateCloses the loop between the document and the declaration

The four questions that record has to answer in one filter each:

  1. For this consignment, which heats are in it and where was each melted and poured?
  2. For this heat number, where is the certificate and who received it?
  3. Which suppliers delivered covered material in the last quarter without a mill certificate?
  4. Which of our EU suppliers source Annex I material from outside the Union, and would therefore feel a documentary delay before we do?

The third question is the one that tells you whether your purchase order clause is actually working. The fourth is the one that nobody is asking yet.

Doing this without a project

A sensible first pass, in order, with no supplier contact until step four.

  1. Get the covered list. Ask your customs team or broker for your import lines falling in the Annex I categories of Regulation (EU) 2026/1384 over the last twelve months. This is a report they can already run.
  2. Find the certificates you already hold. Sample ten of those lines and try to retrieve the mill certificate for each by consignment, not by supplier. How many you find, and how long it takes, is the real measure of where you stand.
  3. Check the two fields. On the certificates you did find, confirm the country of melt and pour and the heat number are both present and legible. Missing fields are what Article 1(2) complementary evidence exists for, and knowing which suppliers have the gap is more useful than knowing the count.
  4. Write the clause. Put the certificate into your purchase order terms for covered material: part of the scope of supply, due by delivery, condition of settlement. Then tell suppliers, with the reason, before the first invoice is held, and fold the requirement into onboarding and qualification for new ones so it never needs retrofitting.
  5. Name the handoff owner. One person accountable for the melt and pour value reaching the declaration, on both sides of the quality to customs boundary.
  6. Set the review date. Put 30 September 2027 in the calendar with one question attached: are we still relying on Article 1(3) anywhere, and for which suppliers?

Six steps, and five of them involve no new software and no supplier burden. If your supplier records currently live in spreadsheets, the retrieval test at step two is usually the moment that becomes obvious, which is a separate conversation covered in moving supplier management off spreadsheets.

What this does not do

Worth being clear, because adjacent claims are already circulating.

It does not make you responsible for your supplier’s declaration. Where your EU supplier is the importer, the evidence obligation is theirs.

It does not replace the material verification your quality function already performs, nor does it change what your supplier compliance records need to hold for every other regime. Chemical composition and mechanical properties are still why the certificate matters technically. The Regulation adds two fields to the list of reasons to keep it.

It does not require a specific certificate standard. The Regulation names the Mill Test Certificate and leaves the format alone.

It does not tell you the TARIC document codes. Article 2(2) says the declaration is made by means of them, and the current values belong to your customs team, not to a blog post.

And it does not, on its own, give you traceability. A certificate retrievable by consignment plus a heat number marked on the material is traceability. A PDF in a folder named after a vendor is a record that you once received a document.

The reusable part

Strip out the steel and the structure generalises, which is why this is worth reading even if you never buy a tonne of the stuff.

A document your organisation already receives acquired a second purpose, in a second function, with a different retrieval pattern and a hard date attached. Nothing was added to the collection burden. Everything changed about where the document has to be reachable from. That happens repeatedly, across regimes, and the organisations that absorb it cheaply are the ones that stored the purpose of every field alongside the field, which is the argument in collect once and report many times. The EUDR supplier data plan is the same shape with a different commodity list, and automotive teams will recognise the pattern from the material traceability their customers already demand, discussed in the IATF 16949 scorecard guide and in our notes on automotive supplier management.

The second reusable piece: when a document is created upstream of your direct supplier, your request is a forwarding request, not a data request. Say so. It is true, it is easier to agree to, and it gets better results.

Frequently asked questions

When did this start?

Commission Implementing Regulation (EU) 2026/1963 of 28 August 2026 applies as from 1 October 2026. The flexible standalone evidence route in Article 1(3) applies from 1 October 2026 to 30 September 2027.

Which products are covered?

Products falling under the categories listed in Annex I to Regulation (EU) 2026/1384, which lists 28 steel product categories by Combined Nomenclature code, including hot rolled and cold rolled sheet, stainless products, bars, wire rod, tubes and pipes. Confirm your own lines against the CN codes with your customs team rather than by product name.

What exactly is the country of melt and pour?

The original location where raw steel or iron is first produced in liquid form in a steel or iron making furnace and then cast into its first solid state, as defined in Regulation (EU) 2026/1384. It is not the country of rolling, coating, forming or shipment.

What if the mill certificate does not show the heat number?

Article 1(2) allows complementary evidence where the certificate is missing the country of origin or the heat number, drawing on the same list of document types as Article 1(3). That route is permanent. The standalone route, where there is no certificate at all, is the one that ends on 30 September 2027.

Is an EN 10204 certificate what is being asked for?

The Regulation names the Mill Test Certificate and does not define it by reference to a standard, so it does not require any particular certificate type. In European practice the document usually arrives as an inspection document issued by the steel manufacturer, and published stockholder guidance describes that document as carrying the cast or heat number, dimensions and chemical composition. Check that your supplier’s certificate carries the two fields the Regulation names, whatever it is called.

We buy finished parts, not steel. Does this apply to us?

It applies where the products you import fall in the Annex I categories. If you buy finished parts from an EU supplier who imports the material, the obligation sits with that supplier, and what reaches you is a documentary dependency in their supply chain worth tracking in your supplier risk records.

Will suppliers push back on this?

Less than you might expect, because most of them are being asked by other customers too, and because the document already exists upstream. Recital 9 of the Regulation notes the certificate is already requested when exporting steel to some non-Union countries. The requests that fail are usually the ones that ask a distributor to create information rather than forward it.

What is the single highest value thing to do first?

Try to retrieve the mill certificate for ten recent consignments, by consignment. Whatever that exercise reveals is your real starting position, and it takes an afternoon.


If you are tightening up how supplier documents are requested, stored and retrieved across several regimes at once, EvaluationsHub keeps certificates, declarations and evidence against the supplier, site and material records they belong to, with the request and follow up handled for you. Book a walkthrough or start with a focused pilot on one category.

Every January someone publishes a list of supplier relationship management trends. Most of it could have been written in any year. This piece takes a different route. It starts from the dates that are already fixed for 2027, works out what each one asks of your suppliers, and only then asks how SRM work has to change to keep up.

The short answer: 2027 is the year several postponed deadlines actually arrive. Deforestation, carbon border, batteries, cybersecurity, forced labour and high-risk AI all land within twelve months. Each one needs supplier data. Very few of them need it in the same shape.

All dates below were checked against primary or professional sources at the end of September 2026. Where something is expected but not confirmed, I say so. If you want the market view (vendors, analyst evaluations, how to choose tools), our SRM research overview covers that ground; this post stays on the calendar.

Three kinds of 2027 date

Before the table, one distinction that makes it easier to plan. The 2027 dates fall into three groups, and each group calls for a different kind of work.

  • Hand-over dates. A supplier must give you specific data by a specific day, or you cannot file, import or sell. EUDR, CBAM and the battery passport are in this group. The work is collection.
  • Test dates. Nothing is filed, but from this day an authority can ask you a question and your answer will be judged. The Forced Labour Regulation, the Cyber Resilience Act and the Machinery Regulation sit here. The work is readiness: can you answer quickly, with evidence?
  • Drafting dates. The rulebook is still being written, and what gets written will shape your 2028 and 2029 requests. The CSDDD guidelines and the ISO 9001:2026 transition belong here. The work is watching, and not over-building.

Most SRM teams treat all three the same way, with a questionnaire. That is how supplier fatigue starts.

The 2027 calendar for supplier managers

SRM 2027: dated obligations, the supplier data they need and a suggested owner (dates checked September 2026)
Date What applies Supplier data you need Who owns it
30 Dec 2026 (run-in) EUDR applies to large and medium operators, and to micro and small operators already covered by the EU Timber Regulation. Hand-over. Geolocation of the plots where the commodity was produced, plus due diligence information per product placed on the market. Procurement with sustainability; compliance signs off
1 Jan 2027 First financial year reported by companies newly in CSRD scope after Omnibus I (more than 1,000 employees and more than EUR 450 million turnover). Reports are published in 2028. Value chain sustainability data, limited by the value chain cap for suppliers with 1,000 employees or fewer. Sustainability lead; procurement runs the supplier requests
20 Jan 2027 Machinery Regulation (EU) 2023/1230 replaces the Machinery Directive, with no transition period. Test. Conformity documentation for machinery and safety components placed on the market from this date. Quality and engineering; procurement for supplier contracts
1 Feb 2027 CBAM certificates go on sale, covering emissions embedded in 2026 imports. Hand-over. Installation-level embedded emissions from non-EU producers of CBAM goods such as iron, steel, aluminium and fertilisers. Trade compliance; procurement chases non-EU installations
18 Feb 2027 Battery passport required for EV, light means of transport and industrial batteries above 2 kWh. Hand-over. Passport data from battery manufacturers, linked to the product you place on the market. Product compliance; supplier quality
30 Jun 2027 EUDR applies to micro and small operators. Hand-over. Same as above, now reaching your smallest upstream partners. Procurement, with extra supplier support
26 Jul 2027 Commission deadline to adopt general CSDDD due diligence guidelines. Drafting. None yet. Read the guidelines before designing 2028 requests. Legal; SRM lead reviews
18 Aug 2027 Battery due diligence obligations apply (postponed by two years). Test. Raw material sourcing and due diligence evidence from your battery supply chain. Supplier risk; sustainability
30 Sep 2027 First annual CBAM declaration and certificate surrender for 2026 imports. Hand-over. Verified 2026 emissions per installation, reconciled with import volumes. Trade compliance; finance
2 Dec 2027 AI Act obligations for stand-alone high-risk systems (Annex III) apply, moved from 2 August 2026. Test. Documentation from vendors of any AI you buy for Annex III uses, such as employment decisions. IT procurement; legal; data protection
11 Dec 2027 Cyber Resilience Act main obligations apply to products with digital elements. Test. Security and vulnerability-handling evidence from suppliers of connected hardware and software components. Product security; IT procurement
14 Dec 2027 EU Forced Labour Regulation applies. Test. Product-level supply chain mapping you can produce on request: which site, which inputs, which sub-tier. Supplier risk; compliance
30 Dec 2027 EUDR extends to newly added products, including soluble coffee, certain palm oil derivatives and frozen cattle tongues. Hand-over. EUDR data for the new product codes. Category managers for affected categories

A few notes on precision. The EUDR dates come from the European Commission’s EUDR page. The CBAM dates follow the CBAM Omnibus, Regulation (EU) 2025/2083, as summarised by EY and confirmed by KPMG. The battery due diligence postponement is in Regulation (EU) 2025/1561. The Cyber Resilience Act date is on the Commission’s CRA page. The Forced Labour Regulation date is confirmed by Linklaters and Squire Patton Boggs.

The AI Act row deserves a word of its own. The high-risk delay was only a proposal until mid-2026. It is now law: Regulation (EU) 2026/1744 was published in the Official Journal in July 2026, moving Annex III obligations to 2 December 2027 and product-embedded (Annex I) systems to 2 August 2028. Our AI Act guide for procurement covers the rest of that regulation.

What is not on the calendar, and why

  • ISO 9001:2026 transition. The standard was published in September 2026. Certification bodies expect ISO 9001:2015 certificates to remain valid until 30 September 2029, but that end date is still subject to confirmation by the accreditation body. Expect supplier recertifications to trickle through 2027 rather than arrive on one date. Ask for the certificate edition in your supplier records now so you can see the drift.
  • ESPR digital product passports. The Ecodesign Regulation has been in force since July 2024, and passports arrive product group by product group through delegated acts. I found no product group with a confirmed 2027 application date. The battery passport, which sits under the Batteries Regulation, is the first passport most supplier managers will meet.
  • CSDDD itself. After Omnibus I (Directive (EU) 2026/470), companies apply the directive from 26 July 2029. The only 2027 CSDDD date is the Commission’s guidelines deadline.

Five shifts in how SRM work gets done in 2027

A calendar with thirteen rows does not fit inside an annual supplier review. That mismatch drives most of what changes next year.

1. Continuous monitoring replaces the annual cycle

An annual review assumes one moment a year when you ask everything. In 2027 the deadlines are spread from January to December, and the test dates can arrive on any working day as a letter from an authority. The only workable pattern is to monitor signals continuously (certificate expiry, sanctions hits, delivery performance, incident reports) and reserve supplier effort for the points where a date or a signal demands it. We set out that model in moving from annual reviews to continuous supplier monitoring.

2. Supplier, site and part replace the flat vendor record

Look at the second column of the table again. EUDR asks about plots and products. CBAM asks about installations. The battery passport attaches to a product. A forced labour request names a product. Almost none of the 2027 obligations are satisfied by a record that says “Supplier X, country Y”. If your supplier master cannot tell you which site makes which part, and since when, 2027 is the year that gap becomes visible to people outside procurement.

3. Collect once, report many times

The same supplier will be asked for plant locations by trade compliance for CBAM, by sustainability for CSRD and by procurement for EUDR. Three requests, three formats, one answer. The fix is a shared supplier data layer where each field is collected once, to the strictest standard any regime needs, and tagged with the purpose it serves. The purpose tag matters. The CSRD value chain cap protects suppliers with 1,000 employees or fewer from CSRD requests beyond the voluntary standard, but it does not limit a request made for EUDR or CBAM. You can only respect that line if you record why you asked.

4. Supplier response rate becomes a planning constraint

Every hand-over date on the calendar depends on a supplier replying. A small cocoa cooperative, a Turkish steel mill and a Chinese battery cell maker have finite attention, and your competitors are asking them too. In 2027 the binding constraint on compliance will often be the reply rate rather than the regulation. Good teams will plan requests the way they plan capacity: fewer, shorter, pre-filled with what you already hold, and returned with something useful for the supplier, such as their own scorecard. A two-way supplier portal helps because the supplier updates one record instead of answering five emails.

5. AI proposes, people approve

The volume of signals in shift one is more than a small SRM team can read. One answer is AI that watches contracts, scorecards and risk feeds, then proposes an action with its reasoning. The sensible design keeps a person in charge of anything that reaches a supplier and logs every decision. If you are evaluating tools on this point, our guide on how to compare AI features in SRM software sets out the questions to ask. The AI Act dates above are also a reminder to check which AI in your own stack falls into a regulated use before 2 December 2027.

A 2027 planning routine that fits on one page

  1. Map each row to categories. For every date, list the categories and suppliers affected. Most organisations will find that only some rows apply, and that is useful to know early.
  2. Tag each row by type. Hand-over rows go into a collection plan with supplier deadlines set four to six weeks before yours. Test rows go into a readiness check: could you answer a request about a named product quickly, with evidence? Drafting rows go on a watch list.
  3. Build the site layer where two or more rows overlap. If a supplier appears in the EUDR, CBAM and forced labour rows, start there.
  4. Merge the requests. One campaign per supplier per quarter, not one per regulation.
  5. Close the loop. Missing or poor data becomes a corrective action with an owner and a date, tracked like any other supplier nonconformity, alongside OTIF and PPM issues. A supplier who cannot supply EUDR geolocation is a supplier quality problem, and CAPA is the tool you already use for those.

Where EvaluationsHub, InitiativesHub and Eva AI fit

Read the calendar again and it is a data problem before it is a compliance problem. EvaluationsHub is a supplier performance and lifecycle management platform: supplier risk, ESG and CSRD data, weighted performance scorecards, CAPA, QBR management and a two-way supplier portal, with an audit trail on every change. It holds the supplier record the table depends on, and it is ISO 27001 certified and hosted on AWS in the EU.

InitiativesHub covers the execution side of the lifecycle: intake, RFx, supplier qualification, awarding, contract management with SLAs and KPIs mapped to clauses, and onboarding with a handover into EvaluationsHub. That handover matters for 2027, because EUDR, CBAM and battery requirements are easiest to write into a contract at award, not bolt on afterwards.

Eva AI sits on top of both. It is designed to compare contract KPI obligations against live scorecard data and propose a CAPA when a deviation crosses a threshold, to monitor risk signals against your acceptance frame and recommend a compliance workflow linked to the relevant clause, and to surface cost reduction candidates as projects in InitiativesHub. Every proposal is held for human approval, shows its reasoning, and lands in an exportable AI decision audit log. Nothing reaches a supplier without a person saying yes.

If you want to see how your 2027 calendar would map onto it, book a demo.

Frequently asked questions

What will change in SRM in 2027?

The main change is volume and timing. Thirteen EU dates with supplier data implications fall between 30 December 2026 and 30 December 2027, including EUDR, CBAM, the battery passport, the AI Act high-risk rules, the Cyber Resilience Act and the Forced Labour Regulation. That pushes SRM towards continuous monitoring, site and product-level supplier data, and fewer but better supplier requests.

Were the AI Act high-risk obligations delayed?

Yes. Regulation (EU) 2026/1744, published in the Official Journal in July 2026, moved obligations for stand-alone high-risk systems listed in Annex III to 2 December 2027, and for high-risk AI embedded in regulated products to 2 August 2028.

When does the EU Forced Labour Regulation apply?

From 14 December 2027, under Regulation (EU) 2024/3015. The practical preparation for supplier managers is to be able to show, for a named product, which supplier sites and inputs sit behind it.

Does CSDDD apply in 2027?

No. After Omnibus I, companies apply CSDDD from 26 July 2029. In 2027 the relevant date is 26 July, the Commission’s deadline for general due diligence guidelines. Newly in-scope CSRD companies, however, start collecting value chain data for financial year 2027.

By Prof. Dr. Bert Paesbrugghe, founder of EvaluationsHub and associate professor at IÉSEG School of Management.

Here is a clause that appears in a great many supplier quality agreements, in almost exactly these words:

The Supplier shall maintain a robust quality management system and shall promptly notify the Buyer of any significant changes.

It reads well. It has survived legal review at both ends. And it is doing almost no work, because three of its words carry the whole meaning and none of them is defined. Robust according to whom. Promptly meaning what. Significant by whose judgement.

A clause like that is not a problem when everything is going well. It becomes a problem on the one day you need it, when a supplier has moved a process to a second plant, told nobody, and can point out with a straight face that they did not consider the change significant.

The good news is that this is a fixable drafting problem rather than a relationship problem. Most supplier quality agreements can be made materially stronger in an afternoon, without renegotiating commercial terms and without a single adversarial conversation. The method is simple: every clause gets a record, an owner and a review point. If a clause has none of those three, it is a wish rather than a requirement.

What the quality agreement is for, and what it is not for

A supplier quality agreement is the document that says who does what on quality. It sits alongside the commercial contract rather than inside it, and the regulators who have written most clearly about these documents are unusually direct on that point.

The FDA’s 2016 guidance on quality agreements for contract drug manufacturing recommends that quality agreements “be separate documents, or at least severable, from commercial contracts such as master services agreements or supply agreements”, and says they “should not cover general business terms and conditions such as confidentiality, pricing or cost issues, delivery terms, or limits on liability or damages”. The guidance also describes the sections most quality agreements contain: purpose and scope, definitions, resolution of disagreements, manufacturing activities, and the life cycle of and revisions to the agreement itself.

The EU’s good manufacturing practice guidance takes the same line from a different angle. EudraLex Volume 4, Chapter 7 on outsourced activities states that “There must be a written Contract between the Contract Giver and the Contract Acceptor which clearly establishes the duties of each party”, and that the contract should specify “their respective responsibilities and communication processes relating to the outsourced activities”.

Those two sources come from pharmaceutical and medical device supply, where the expectations are written down most explicitly. Two things follow from the pairing, and they apply well outside those sectors.

First, the agreement is a responsibilities document. Its job is to remove ambiguity about who acts, not to express an aspiration about quality.

Second, keeping it severable from the commercial contract is what makes it maintainable. A quality agreement you can revise without reopening pricing is a quality agreement that stays current. One that is buried in a master supply agreement will be exactly as accurate as it was on the day it was signed.

That separation is also why the life cycle section the FDA describes matters more than it looks. An agreement with no stated revision route quietly becomes a historical document.

The clause-to-evidence map

This is the part worth doing properly, and it is the part almost nobody does. Take your existing agreement, list the clauses, and for each one write down the record that proves compliance, the person who looks at it, and the interval at which they look.

The clause promisesThe record that proves itWho watches itReview point
A certified quality management systemCertificate number, issuing body, scope statement, expiry dateSupplier qualityOn expiry, automatically
Notice before any change to product, process, material or siteDated change notifications, matched against what you actually receivedSupplier quality and engineeringEach notification, plus an annual confirm-or-correct
Manufacture only at the agreed sitesSite list with valid-from and valid-to dates, linked to the parts made thereMaster data ownerOn change, plus annual
No subcontracting without prior approvalApproved sub-tier list with the approval date and approverCategory ownerOn request, plus annual
Response to a corrective action request within an agreed timeCAPA record with raised date, acknowledged date, containment date, closed dateQuality engineerPer case, reported monthly
Retention of batch, lot or build records for an agreed periodThe retention period stated per record type, plus a tested access routeQuality systemsAnnual spot check
Agreed performance levels for delivery and qualityThe metric definition and the dataset it is calculated fromSupplier qualityPer scorecard cycle
No shipment of non-conforming material without a written concessionConcession and deviation register, with an expiry on each oneIncoming qualityPer case

The exercise usually produces two uncomfortable findings and one useful one.

The uncomfortable findings are that several clauses have no record at all, and that several records exist but nobody owns them. The useful one is that the list of things you genuinely need from suppliers turns out to be shorter than the agreement implies, which makes the request you send them easier to answer. That matters, because supplier response rate is the constraint that decides whether any of this works in practice.

None of this needs new infrastructure to start. A spreadsheet with four columns will expose the gaps perfectly well. It is only when you want the review points to fire on their own that you need somewhere to keep them, which is the argument for holding the agreement’s obligations in the same place you hold supplier records and documents rather than in a folder on a shared drive.

The three words to replace

Most weak clauses are weak for the same three reasons. Each has a straightforward fix.

Robust, appropriate, adequate. These invite a difference of opinion at the worst possible moment. Replace them with a named standard and a verifiable artefact. Not “a robust quality management system” but “certification to ISO 9001, with the certificate, its scope statement and its expiry date provided on request and on renewal”. If the site is a manufacturing site in a regulated sector, name the sector standard instead. ISO 13485 and IATF 16949 both certify at site level rather than company level, so a single corporate certificate does not answer the question you are asking. The control of external providers in ISO 9001:2026 works the same way: it asks you to state your requirements, not to hope they are understood.

Promptly, in a timely manner, as soon as practicable. Replace with a number, and attach the number to an event rather than to a feeling. Change notification is the clearest example. ISO 13485:2016 addresses this directly in its purchasing information requirements, which call for a written agreement that the supplier will notify the organisation of changes to the purchased product before those changes are implemented. Before implementation is the load-bearing phrase, and it is the one to borrow whatever sector you are in. In practice most teams turn that into a stated notice period for planned changes and immediate notice for unplanned ones. Whatever number you choose, choose it per category rather than globally, because thirty days of notice is generous for a packaging film and nowhere near enough for a sterilised component that needs revalidation.

Significant, material, major. This is the one that causes the most trouble, because it hands the judgement to the party with the least incentive to exercise it broadly. Replace it with a list. A change list does not need to be long to be effective: manufacturing site or line, production process or key process parameter, sub-tier supplier of a listed material, raw material grade or source, test method, software or firmware in a delivered product, packaging that contacts the product, and the standard or certificate the site holds. Then add a catch-all that asks the supplier to notify anything they are unsure about, and answer those quickly enough that asking stays cheap for them.

The last point is the one that decides whether the clause works. A change notification clause is only as good as your turnaround on the notifications you receive. If a supplier’s notice sits unanswered for six weeks, they will stop sending them, and no drafting will fix that.

The clauses worth the argument

Not every clause earns the negotiation time. These generally do, and they hold up across sectors.

Change notification, as above. The single highest-value clause in the document. Most supplier quality surprises are changes that were never announced.

Site of manufacture, named. A clause that commits the supplier to manufacture only at agreed sites gives you something specific to check, and it is the clause that makes the rest of your supplier and site data trustworthy. Ask for the site list with valid-from dates, not just a current snapshot.

Sub-tier visibility and approval. EudraLex Chapter 7 puts this plainly: “The Contract Acceptor should not subcontract to a third party any of the work entrusted to him under the Contract without the Contract Giver’s prior evaluation and approval.” You do not need full multi-tier mapping to benefit from this. Naming the sub-tiers that matter for the parts that matter is enough to start, and it is far easier to get at contract renewal than in the middle of an incident.

No unauthorised changes. Chapter 7 again: “The Contract Acceptor should not make unauthorized changes, outside the terms of the Contract, which may adversely affect the quality of the outsourced activities.” Worth including even where no GMP obligation applies, because it closes the gap between notifying a change and being allowed to make it.

Corrective action response times, tiered by severity. One response time for everything is either too slow for real problems or too aggressive for minor ones, and the second failure is worse because it trains everybody to miss the deadline. Tier it, and make sure the tiers match how your corrective action process actually classifies findings.

Concessions and deviations, with expiry dates. Every concession should carry an end date or a quantity limit. Concessions that quietly become permanent are one of the most common ways a specification drifts without anyone deciding to change it.

Records, retention and access. State the retention period per record type and, more importantly, state the access route. A retention clause that has never been tested is an assumption. One spot check a year turns it into a fact, and gives you the audit trail you will want if a customer or notified body ever asks how you verified it.

Audit rights, including remote. Write in the option of a documented remote assessment alongside on-site audit rights. It costs nothing to include and it is what makes a digital or remote audit available to you later without a fresh negotiation.

Exit provisions. Last-time-buy rights, record handover, tooling return and a transition period. These are far cheaper to agree at the start of a relationship than at the end of one, and they make an eventual structured offboarding a process rather than an argument.

The clauses that create work for you

Here is the part that most templates leave out, and it is the part that makes the rest credible.

A supplier quality agreement that only imposes obligations tends to be complied with narrowly. One that also states what you will do tends to be complied with willingly, and it is a much easier document to get signed. The FDA guidance and the EU GMP chapter both frame these documents as establishing the duties of each party, which is a useful reminder that there are two parties in the phrase.

Four mutual clauses are worth writing in.

Your approval turnaround. If you require notice before a change, state how quickly you will respond. Suppliers who wait months for a deviation decision start making decisions themselves.

Your forecast horizon. Say what visibility you will provide and how far ahead. Much of what looks like supplier delivery unreliability is a forecast problem wearing a supplier’s name, and saying so in the agreement is an act of good faith that costs very little.

A named contact on your side, with a named backup. Agreements routinely require the supplier to nominate a quality contact and say nothing about who the supplier should call. This one clause removes a surprising amount of friction.

The results come back. Commit to sharing the supplier’s own performance data with them on a stated cycle. This is the cheapest clause in the document and one of the most effective, because the data already exists on your side. Sending the supplier scorecard back is what turns evaluation from something done to a supplier into something they can act on, and it makes every subsequent data request easier to land.

Where the agreement meets the scorecard

Most disputes about a supplier scorecard are not disputes about performance. They are disputes about definitions, and they are almost always traceable to a clause that was never written.

Two teams looking at the same shipments will produce different on-time delivery numbers if one measures against the date the supplier promised and the other against the date the buyer requested. Add goods-receipt date versus dock date, a tolerance window measured in days versus hours, and different treatment of partial deliveries, and the gap between two honest calculations can be very wide.

The agreement is where those definitions belong. For each metric you intend to hold a supplier to, write down the event that starts the clock, the event that stops it, the tolerance, the treatment of partials and reschedules, and the data source of record. That is perhaps a paragraph per metric, and it converts an annual argument into a shared reference.

The same logic applies to quality metrics. Parts per million defective is not one number until you have said whether it counts incoming rejections only or includes line stoppages and field returns, and whether it is measured per part number or per site. Settling that in the agreement is what allows a weighted scorecard to be discussed on its merits.

There is a useful discipline here: do not write a metric into the agreement that you are not yet able to calculate. A committed metric you cannot produce is worse than no metric, because the first time you fail to produce it you have taught the supplier that the agreement is decorative.

Retiring clauses is part of maintaining them

Quality agreements only ever grow. Every incident adds a clause, and nothing ever removes one. After a few years the document is long, parts of it contradict other parts, and nobody can say which clauses are actually monitored.

The fix is a review point on the document itself, which is exactly what the FDA guidance means by including the life cycle of and revisions to the agreement. Once a year, walk the clause-to-evidence map and ask three questions of each clause: has anybody looked at this record in the past twelve months, is the named owner still in the role, and would we notice if the supplier stopped complying.

A clause that fails all three is not protecting you. It is either a record you should start collecting or a clause you should remove, and removing it is a legitimate answer. A shorter agreement that is fully monitored is stronger than a long one that is monitored in patches, and it is a much better basis for the kind of conversation you want in a quarterly business review.

Tier the review effort the way you tier everything else. Your critical and strategic suppliers deserve a genuine annual clause review. For the long tail, a confirm-or-correct on the certificates and the site list is proportionate, and that judgement should follow the same risk-based segmentation you already use for evaluation frequency.

A first pass you can do this week

You do not need a legal project to make progress. Pick your three highest-spend or highest-risk suppliers and do this.

  1. Print the current quality agreement and list its clauses in a four-column table: clause, record, owner, review point.
  2. Fill in the columns you can. Leave the rest blank rather than guessing, because the blanks are the output of the exercise.
  3. Circle every use of robust, appropriate, adequate, promptly, timely, significant, material and major.
  4. For the change notification clause only, draft the replacement: the change list, the notice period per category, and your own response commitment.
  5. Check the certificate expiry dates you hold against the certificates the supplier holds. This single check finds more issues than most people expect, and it is a friendly conversation to have.
  6. Note which of the blanks in column two are records you could collect through your existing supplier portal rather than by email.

Three suppliers is enough to tell you whether your template needs a revision or a rewrite, and it gives you a worked example to take to the rest of the base. If you want a structured way to prove the approach before rolling it out, a short supplier performance pilot on those same three is a reasonable way to do it.

The short version

A supplier quality agreement is not a statement of intent. It is a list of obligations, each of which should point at a record, an owner and a date. Write clauses you can measure, say what you will do as well as what you require, put your metric definitions in the document rather than in the argument, and review the whole thing once a year with permission to delete.

Suppliers are rarely the obstacle here. Most of them would much rather be held to a clear standard they can meet than a vague one they can only fail unexpectedly.

If you would like to see how the obligations in an agreement can be held against live supplier records, certificates and scorecards in one place, we are happy to walk you through it.

Frequently asked questions

Is a supplier quality agreement the same as a supply agreement?

No, and it is generally better if it is not. The FDA’s guidance on quality agreements recommends they be separate documents, or at least severable, from commercial contracts, and that they leave out general business terms such as confidentiality, pricing, delivery terms and liability. The practical benefit is maintainability: you can revise a severable quality agreement as processes change without reopening the commercial negotiation.

Do we need one for every supplier?

Very few organisations need a full quality agreement with every supplier, and attempting it usually produces a lot of unsigned documents. Tier it. A full agreement for suppliers whose output affects product conformity or regulatory status, a short quality annex for the middle tier, and standard purchase order terms for the long tail is a defensible structure. The segmentation model you already use for evaluation can decide the tiers.

What is the single most valuable clause to fix first?

Change notification, in almost every case. Most supplier quality surprises are changes that happened without notice. Replace the word significant with an explicit change list, require notice before implementation rather than promptly, set the notice period per category, and state your own response time in the same clause.

How do we handle a supplier who will not sign our template?

Ask which specific clauses they object to, because the answer is informative. Objections to record retention, site naming or sub-tier disclosure sometimes reveal a capability gap rather than a commercial position, and a capability gap is something you can work on together through supplier development. Objections to one-sided approval timelines are usually fair, and adding your own commitments is the cheapest concession available.

Where should the agreement’s obligations actually live?

Wherever you will see them without looking for them. An agreement in a contract repository is a legal record; the obligations inside it need to be operational, which means certificate expiry dates that raise a task, change notifications that create a record, and clause owners who are named people rather than departments. Teams that keep this in documents tend to discover lapses at audit time, which is the argument for moving supplier obligations out of spreadsheets.

Does this apply outside regulated industries?

The drafting method does, entirely. The regulatory sources quoted here are simply the places where the thinking has been written down most clearly. A change notification clause with a defined change list is just as useful for an electronics contract manufacturer or a packaging converter as it is for a pharmaceutical contract facility, and the clause-to-evidence map works the same way in IT services as in automotive.

Run one query against your supplier database this week.

Find every supplier record holding an ISO 9001:2015 certificate with a stored expiry date after 30 September 2029. Then find every supplier record holding an ISO 14001:2015 certificate with a stored expiry date after 30 April 2029.

Both lists are wrong, and they were wrong the moment the transition requirements were published in September 2026. The certificates in those records will stop being accredited certification before the dates printed on them. Nothing in your system knows that yet, because the expiry date on a certificate and the end of a transition period are two different things, and almost every supplier database stores only the first one.

This is not a crisis. It is a three year piece of housekeeping with a very long runway, and the teams that start it now will spend an hour on it rather than a quarter. It also happens to be one of the cleanest opportunities you will get this year to improve the quality of your supplier records, because it gives you a concrete, dated reason to go and look at them.

What actually happened in September 2026

Three things landed within two weeks of each other.

ISO 9001:2026 was published on 16 September 2026. We covered what the revision itself changes for supplier quality teams in our guide to ISO 9001:2026 and the control of external providers, and this piece deliberately does not repeat it. The question here is not what the new standard asks of your quality system. It is what the transition does to the certificates you hold on file for other companies.

ISO 14001:2026 was published shortly before it, and it has its own separate transition.

The transition rules for both were set by Global ACI, which is the body that now does the job the International Accreditation Forum and the International Laboratory Accreditation Cooperation used to do separately. Global ACI came into operation on 1 January 2026, and its single mutual recognition arrangement replaces the former IAF MLA and ILAC MRA. If you have been searching for an IAF resolution on the ISO 9001:2026 transition and finding nothing, that is why. The document exists, it just has a different name on it now.

For ISO 9001:2026, the rules sit in Global ACI-TECH-3-TR 2029-09-30 (M), Transition Requirements for ISO 9001:2026, issued 16 September 2026. For ISO 14001:2026, they sit in Global ACI-TECH-3-TR 2029-04-30 (M), Transition Requirements for ISO 14001:2026, issued 14 September 2026.

The two timetables, side by side

Here is where it gets interesting for anyone maintaining a supplier file. The two transitions do not run in step.

MilestoneISO 9001:2026ISO 14001:2026
Accreditation bodies ready to assess31 March 202731 October 2026
Certification bodies submit transition declarations30 June 202731 January 2027
Accreditation decisions completed30 September 202730 April 2027
New certifications issued only to the 2026 edition31 March 202831 October 2027
Final deadline for existing certificate holders to transition30 September 202930 April 2029

Read the two right hand columns against each other and the practical shape of the next three years appears. The environmental transition is roughly five months ahead of the quality one at every stage. The first milestone of either transition, accreditation bodies being ready to assess against ISO 14001:2026, falls on 31 October 2026, which is a few weeks away rather than a few years.

If you treat these as one combined project with one deadline, you will be late on the environmental side and early on the quality side. They are two projects that happen to look alike.

The two dates that are actually yours

Of the ten dates in that table, eight describe work that accreditation bodies and certification bodies have to do. You can safely ignore those. They matter to your suppliers’ auditors, not to you.

Two rows are yours.

The row that changes what arrives. From 31 March 2028 for quality, and 31 October 2027 for environment, new and initial accredited certifications may only be issued to the 2026 editions. This is the date that affects onboarding rather than monitoring. Qualify a new supplier after it, and the certificate they send you will be a 2026 one. Qualify a new supplier before it, and you may well receive a 2015 certificate that is perfectly valid on the day it arrives and already has a shortened life. If your supplier onboarding process has a checkbox that says “ISO 9001 certificate received”, that checkbox is about to start meaning two different things.

The row that changes what you already hold. 30 September 2029 for quality and 30 April 2029 for environment are the final deadlines for organisations still certified to the 2015 editions to complete their transition. These are the dates that quietly rewrite the expiry fields in your database.

Why the expiry field is wrong

A certificate carries an expiry date, usually three years from issue. A transition period carries an end date. When the two disagree, the transition date wins.

The previous cycle shows what that looks like in practice. ISO 9001:2015 replaced ISO 9001:2008, the transition period ended on 18 September 2018, and ISO/TC 176/SC 2 recorded the outcome in one sentence: “Accredited certification to ISO 9001:2008 is now no longer valid.” Certificates with printed dates running past that point did not survive it.

Global ACI’s announcements set the final deadline for completing the transition and do not spell out what happens to a 2015 certificate the day after. The sensible reading, and the one the previous cycle supports, is that an organisation which has not transitioned by then no longer holds accredited certification to the standard, whatever date is printed on the paper.

So the practical rule for your records is simple and slightly uncomfortable: for any ISO 9001:2015 or ISO 14001:2015 certificate you hold, the real expiry is the earlier of the printed date and the transition deadline. That is a one line change to how you calculate a renewal reminder, and it is worth making now rather than in 2029, because the whole point of the reminder is to give you notice.

A supplier whose certificate reads “valid to 14 March 2030” is not giving you cover until 2030. They are giving you cover until 30 September 2029 and then a question. If your certificate tracking lives in a spreadsheet, this is the kind of rule that has to be applied by hand every time somebody looks, which is to say it will not be applied. Systems that hold supplier information as structured records rather than attachments can hold two dates and alert on the earlier one, which is the whole argument for moving this work off spreadsheets in a single sentence.

Three populations in your supply base

Transitions are much easier to manage once you stop thinking of your certified suppliers as one group. They are three, and each needs a different thing from you.

The ones who will transition early and tell you. Typically larger suppliers with a dedicated quality function, often multi site, often certified to several standards at once. They will move during a scheduled surveillance or recertification audit, and a new certificate will arrive without you asking. Your only job here is to make sure the new certificate actually lands in the system and replaces the old one rather than sitting in somebody’s inbox. This is a process problem, not a supplier problem, and a supplier portal where the supplier uploads the document themselves removes it entirely.

The ones who will transition on their own schedule and need a reminder. The large middle. They are not at risk, they are just busy, and their certification body will handle it at the next audit in the normal way. They need one well timed, friendly request rather than a campaign, and the timing is the whole trick: too early and you are asking for something that does not exist yet, too late and you are chasing. More on timing below.

The ones who may quietly let certification lapse. This is the group worth your attention, and the reason is not compliance. A supplier deciding not to transition is a supplier making a decision about cost, capability or commitment, and that decision usually says something about the direction of the business well before it shows up in delivery or quality numbers. Treated well, a transition is a free, early, honest signal about supplier health, arriving years before your performance scorecards would pick anything up. That is genuinely useful information and it costs you nothing to collect.

Which suppliers belong in which group is a segmentation question, and if you already run risk based supplier segmentation you have most of the answer. Certification matters most where the purchased item carries the most risk, not where the supplier is largest, and segmentation models that separate strategic importance from risk exposure will tell you where to spend the attention.

The timing trap: do not require what cannot yet be issued

Here is the mistake to avoid, and it is an easy one to make with the best of intentions.

Someone writes a clause, or updates an onboarding requirement, or sends a supply base wide letter, asking suppliers to provide certification to ISO 9001:2026. In late 2026 and most of 2027, a large number of suppliers simply cannot, because their certification body has not yet been assessed and declared for the new edition. The accreditation decisions are not due to be complete until 30 September 2027 for quality and 30 April 2027 for environment. Asking before then produces confusion, a round of apologetic emails, and a small dent in your credibility with exactly the suppliers whose goodwill you will want later.

The generous version of the same request works far better and costs nothing. Ask when the supplier’s certification body expects to be able to audit them against the 2026 edition, and when their own transition audit is planned. That is a question every supplier can answer at any point in the next three years, it tells you what you actually need to know, and it reads as a buyer who understands the system rather than one issuing demands into it. It is also a much better use of your supplier follow up capacity than a request that will have to be sent twice.

A reasonable sequencing, which you can adjust to your own risk profile:

  • Now to early 2027. Fix the data. Correct the expiry logic, find the records with missing or unreadable certificates, and establish which of your suppliers hold which standards at which sites. No supplier contact required.
  • Through 2027. Ask the planning question above during reviews you are already holding. Fold it into the business reviews and evaluation cycles already in your calendar rather than creating a separate campaign.
  • 2028. Follow up with the suppliers who have no plan and the suppliers who have gone quiet. By this point the system has capacity and there is still well over a year of runway.
  • First half of 2029. Handle the exceptions, with the environmental deadline arriving five months before the quality one.

Starting the supplier facing work in 2027 rather than 2026 is not procrastination. It is waiting until the question has an answer.

What a certificate record should actually hold

Most supplier databases store a certificate as a file plus an expiry date. That was always a little thin, and this transition is a good excuse to fix it. A certificate record that earns its place holds:

FieldWhy it matters
Standard and editionThe whole point. “ISO 9001” is no longer enough to identify what you hold.
Certificate number and issuing certification bodySo you can verify it, and so you know whose transition declaration affects it.
Accreditation bodyAn unaccredited certificate is a different thing from an accredited one, and the transition rules described here govern accredited certification.
Scope statementA certificate covering a product family you do not buy tells you very little.
Sites coveredThe field most often missing, and the one that matters most.
Issue date and printed expiry dateThe baseline.
Effective expiryThe earlier of the printed date and the applicable transition deadline.
Transition status and planned audit dateThe field that makes the next three years manageable.

The sites row is worth dwelling on, because it is where this topic meets a bigger one. A certificate is issued to named sites, not to a company, and a supplier can perfectly well hold a current certificate covering a plant that does not make your parts. If your records attach certificates to the vendor rather than to the site, you cannot answer that question at all. We set out how to build the underlying structure in supplier, site and part: the data model that answers product level questions, and the certificate layer is one of the clearest arguments for building it.

Storing the transition status and planned audit date turns a three year wait into something you can actually report on, which is the difference between knowing your exposure and discovering it. Whatever system holds this needs a reporting and audit trail layer so you can show when a certificate was received, by whom, and what it replaced.

What to put in the agreement

If you are writing or revising supplier quality agreements, this transition is a reason to look at the certification clause, which in most templates is one of the weakest things in the document. The usual wording says the supplier “shall maintain ISO 9001 certification”. It names no edition, no notice obligation and no evidence, so it cannot be monitored and nobody ever checks it.

A clause that works through a transition does four things. It names the standard and the edition rather than the standard alone. It requires the supplier to notify you of any change to the status, scope or sites of their certification, within a stated number of days, which is the same change notification discipline that applies to process and material changes. It names the record where the current certificate lives and who owns keeping it current. And it says what happens if certification lapses, which should be a conversation and a plan rather than an automatic consequence, because a supplier who loses certification for administrative reasons and a supplier who loses it for capability reasons are not the same problem.

The general method is the one we apply to every clause worth having: name the standard, name the record that proves it, name the owner, and name the point at which somebody looks. The certification clause is a good first candidate for it, because the evidence is unusually easy to name. It sits naturally alongside the qualification evidence you already gather at onboarding and qualification.

Worth saying plainly: adding a notice obligation to an agreement does not oblige you to renegotiate every contract this year. Most teams will pick the clause up at the next scheduled revision, and a short covering note to strategic suppliers explaining how you intend to handle the transition will do more good in the meantime than a contractual amendment.

The supplier who is not going to transition

Some suppliers will decide that certification is no longer worth the cost. For a small specialist with one customer who cares, that can be an entirely rational decision, and it is better to find out in 2027 than in 2029.

Treat it as a sourcing question rather than a compliance failure. The useful questions are whether the certificate was ever the thing giving you confidence or just the thing giving you documentation, whether you have your own evidence of capability from audits, performance history and corrective action records, and whether a second source exists if you need one. For many indirect and low risk categories the honest answer is that the certificate was a convenience, and a well evidenced supplier without one is a perfectly good supplier. For a critical component in a regulated product it is a different conversation, and you now have two full years to have it calmly.

Where the supplier is one you want to keep, this is also an opening for supplier development rather than an exit. A small supplier struggling with the cost of transition is a supplier telling you about a capability gap, and that is the kind of gap a buyer can actually help close. Where it is not, a planned and ethical offboarding started early beats an unplanned one started late.

A twenty minute first pass

You can do the whole of the valuable part of this in one sitting.

  1. Pull every supplier record with an ISO 9001 or ISO 14001 certificate on file.
  2. Flag the ones with a printed expiry after 30 September 2029 (quality) or 30 April 2029 (environment). Those are your effective expiry corrections.
  3. Flag the ones where you cannot tell which edition the certificate is, or cannot find the certificate at all. In most supply bases this list is longer than the first one, and it is the more useful finding.
  4. Cross the flagged list against your critical and strategic suppliers. That intersection is your actual work. Everything else can wait for a scheduled review.
  5. Add two fields to wherever you keep this: edition, and transition status.

Step three is the one that pays for the exercise. Most teams running it discover that the transition is the smaller problem and the state of their certificate records is the bigger one. That finding has been sitting there for years and this is simply what finally surfaced it, which is a good outcome rather than a bad one.

If you want to see what this looks like when certificates, sites and expiry logic sit in one place, our supplier compliance tracking and audit capability covers the mechanics, and a short supplier performance pilot is usually the quickest way to find out whether your current records would survive the exercise. You can also book a demo and bring your own certificate list to it.

Frequently asked questions

Does this affect my own ISO 9001 certification as well as my suppliers’?

Yes, and your quality function is almost certainly already on it. This piece is deliberately about the other side of the relationship, the certificates you hold for other companies, because that side usually has no owner. Our ISO 9001:2026 guide covers what the revision means for your own system and for how you control external providers.

Do my suppliers have to be certified to ISO 9001:2026 by 30 September 2029?

Suppliers who hold accredited ISO 9001:2015 certification and wish to keep accredited certification need to complete the transition by then. Suppliers who are not certified at all are unaffected, and suppliers certified to other schemes follow those schemes’ own rules. The equivalent environmental deadline is 30 April 2029.

Should I ask my suppliers for ISO 9001:2026 certificates now?

Asking for the certificate now will not get you far, because certification bodies are still being assessed and declared for the new edition into 2027. Asking when their transition audit is planned works at any time and gives you better information.

What about IATF 16949, AS9100 and the other sector schemes?

Sector schemes built on ISO 9001 have their own governance and their own transition arrangements, which are published separately by the bodies that own them. Do not assume the dates above apply to them. If you work in automotive, our piece on building a supplier scorecard that satisfies IATF 16949 covers the related ground on evidence, and SRM for automotive covers the wider context.

Is this relevant in regulated manufacturing, where we rely on other standards?

Very. In medical devices and pharma, supplier files are inspected, and a file containing a certificate that expired under a transition you did not track is exactly the sort of finding that is easy to avoid and awkward to explain. The fix is the same: store the edition, calculate the effective expiry, and keep the evidence where somebody can find it.

We have hundreds of suppliers. Is this really worth it?

The correction itself is a one off rule change, not a per supplier task. The work that scales is only the follow up, and the three population split above exists precisely so you do not do it for everyone. Teams running supplier programmes at scale handle this by acting on the critical intersection and letting the rest resolve through normal review cycles.

In every kitchen I worked in, the new piece of equipment arrived on a Monday and the arguments started on Tuesday. A combi oven can do almost anything. It cannot decide what you are cooking, in which order, for whom. Mise en place is a logic about how work flows, not a gadget, and the gadget only helps once that logic exists.

I was reminded of this by a Gartner press release published on 8 October 2026. In its 2026 Chief Procurement Officer Survey, covering 213 senior procurement leaders, 63% said they expect AI to significantly improve procurement performance over the next three years. Yet only 25% had redesigned jobs or roles as a direct result of implementing AI. Gartner’s Fareen Mehrzai calls successful AI implementation at functional level “fundamentally a role redesign challenge”, and warns that skipping it invites what Gartner calls “job chaos”. (Both surveys concluded in April 2026. The full release is on Gartner’s newsroom.)

Read those two numbers side by side. Nearly two thirds expect the benefit. A quarter changed the work to earn it. That gap is where most buyer enablement technology goes to die.

Technology, but no logic

I have interviewed buyers for years as part of my research, and one pattern keeps returning. When I ask what would make buying easier, they rarely ask for another platform. They describe friction: a supplier who needs the same information three times, an approval route nobody can explain, a tool that records decisions after they have been made rather than helping to make them. The technology was bought. The logic of the work was never revisited.

This matters well beyond your own department. Your suppliers experience your processes as the product you sell them. If your AI-assisted intake form asks twelve questions a human colleague would never ask, the supplier does not see innovation. They see a buyer who is hard to work with. And a buyer who is hard to work with gets the second-best proposal, the slower response, the account manager who is quietly reassigned.

What a role redesign actually asks of you

Mehrzai says CPOs must give employees agency in shaping how their roles evolve, and that redesign cannot be a one-time exercise. I would translate that into three questions for your next team meeting.

First, which task did this tool take away, and what did we decide the person does instead? If the honest answer is “the same job, plus the tool”, you have added load, not leverage.

Second, where does the time saved go? In a kitchen, a faster prep station only helps if the pass is ready for it. In procurement, the hours released from chasing quotes should flow towards the work machines handle badly: reading what a supplier is really telling you, building trust, spotting the weak signal in a delivery pattern.

Third, who decides when the tool is wrong? Every system needs a human who is allowed to say “this recommendation does not make sense for this supplier”. Without that person, you have automated your blind spots.

The balance in it

In The Buyer’s Balance I argue that B2B relationships work when buyer and seller find equilibrium, and that relevance and information sharing build that relationship far more reliably than a dazzling moment. Technology can serve that balance or erode it. Used well, it clears the administrative undergrowth so a buyer has time for the conversation that matters. Used badly, it puts a more efficient wall between you and the people who hold the information you need.

So the test I would apply is a simple one. After you introduced the tool, did your suppliers find you easier to work with? If you do not know, ask five of them. That is cheap research, and in my experience the answers arrive within the week.

Before the next licence renewal

Pick one tool your team already owns. Write down the job it was meant to change, then write down what actually changed. Where the two lists differ, you have found your role redesign. Start there, with the people doing the work in the room.

Gartner’s numbers suggest most of us are still waiting for the technology to do the redesigning for us. It will not. The oven never decided what was for dinner.

Bert Paesbrugghe is associate professor of sales management and purchasing strategy at IESEG School of Management (Paris) and guest professor at Ghent University. He is the author of The Buyer’s Balance: What your customers want to share with you (Owl Press, 2025, ISBN 9789464778908). More at evaluationshub.com/book.

Source: Gartner, “Gartner Survey Shows Chief Procurement Officers Stalling on Needed AI Role Redesign”, press release, 8 October 2026.

Picture a supplier that misses its on-time-in-full target for the third month running. The quality engineer opens a corrective action. The category manager wants to know whether the contract allows a service credit. Nobody can find the qualification note from eighteen months ago that approved the supplier “subject to confirmation of second-shift capacity”. Every stage of the lifecycle did its job. The failure happened in the gaps between them.

That pattern is the reason for this article. Most supplier lifecycle management programmes are assessed by listing their stages and checking that each one has a process, an owner and a screen. The better test is to look at what moves from one stage to the next, and what gets dropped on the way.

SLM, SRM and SPM are three different scopes

The three terms get used as synonyms. They describe different jobs, and mixing them up is one reason handovers go unowned.

  • Supplier performance management (SPM) measures. It defines KPIs, collects data, builds supplier scorecards and flags deviations.
  • Supplier relationship management (SRM) manages the relationship itself. CIPS defines it as “the management and maintenance of the relationship between a buyer and supplier” and notes that the type of relationship depends on the criticality of what is being bought. In practice SRM is selective: strategic suppliers get QBRs and joint plans, the long tail does not.
  • Supplier lifecycle management (SLM) covers the whole span, from the first internal need to the last day of the relationship, for every supplier you buy from. Its real subject is continuity: the same supplier record, the same obligations and the same accountability carried from sourcing through to renewal or exit.

SPM and SRM live inside SLM. If you want the finer distinction between the first two, we covered it in the difference between SPM and SRM. For a stage-by-stage walkthrough of the lifecycle itself, see full supplier lifecycle management from sourcing to offboarding. This piece picks up where those leave off: the joins.

Why modules are the wrong unit of evaluation

Every supplier management vendor can show you an onboarding screen, a scorecard and a CAPA form. A module checklist will almost always come back green. It tells you very little about whether the qualification risk, the contract KPI and the corrective action are the same thread or three unrelated records.

The standards that supplier quality teams work to are written as chains, not as separate boxes. ISO 9001:2015, still the basis of most certificates while the transition to ISO 9001:2026 runs, shows this in clause 8.4.1, which puts the whole sequence into one requirement: the organisation shall “determine and apply criteria for the evaluation, selection, monitoring of performance, and re-evaluation of external providers”, and retain documented information of those activities and any actions arising from them. Clause 8.4.3 goes further and requires you to communicate to the supplier how its performance will be controlled and monitored. In other words, the performance regime is supposed to be known at the point of contract, not invented afterwards.

IATF 16949 makes the dependency explicit for automotive. Clause 8.4.2.5 asks organisations to determine the priority, type and timing of supplier development actions based on defined inputs: performance issues from supplier monitoring, second-party audit findings, third-party QMS certification status and risk analysis. Supplier development is defined by what it receives from earlier stages. If those inputs do not arrive, the clause cannot be met, however good your development process looks on paper.

The commercial side sees the same thing. World Commerce & Contracting put it plainly in June 2026: “Value leaks between handoffs.” In an earlier piece, WorldCC’s Tim Cummins cited the association’s own research identifying 11% value erosion in procurement contracts and described how procurement focuses on award, legal on risk allocation, and operations “inherit the consequences”. Each function is competent. The value disappears between them.

The lifecycle as a chain of handovers

The table below treats each stage as a supplier of information to the next one. For each stage it names the question the stage exists to answer, the data object it must pass on, and the failure we see most often at that join.

Supplier lifecycle stages, the data object each hands on, and the typical handover failure
Stage Question it must answer Data object it hands on Typical failure at the handover
Intake and needs capture What exactly do we need, and how critical is it? Requirement record with criticality, specification and budget owner Criticality is never recorded, so every later stage treats a sole-source part like office supplies
Sourcing (RFI, RFQ, RFP) Who can meet the requirement, at what cost and risk? Evaluated bids with weighted criteria and the supplier’s own commitments Commitments made in the bid (lead times, capacity, certifications) stay in the RFx file and never reach the contract
Qualification Is this supplier and site capable and compliant? Approval status per supplier and site, with conditions and open risks “Approved with conditions” becomes “approved”, and the conditions disappear
Award and contract What have both sides agreed to deliver and measure? Obligations: SLAs and KPIs with definitions, targets, remedies and review cadence KPIs are written as prose in a PDF, with no definition a scorecard could use
Onboarding Is the supplier set up to perform from day one? Complete supplier master record, contacts, documents, and the KPI set switched on Onboarding closes when the vendor number is created, before performance measurement is configured
Performance and risk monitoring Is the supplier delivering what was agreed, and is its risk changing? Scorecard history, risk signals and threshold breaches Scores are reviewed but a breach has no owner and no route into corrective action
Development and CAPA What will change, who owns it, and did it work? CAPA with root cause, actions, owners, due dates and verified effectiveness CAPA is closed on paperwork, and nobody checks the following months of scorecard data
Renewal or exit Should we continue, change terms, or leave? Full relationship history feeding the next sourcing decision, or a retained record at exit Renewal is decided on price alone and three years of performance and CAPA history go unread

Read the right-hand column again. None of those failures is caused by a bad stage. Each one is caused by an object that was produced and then not received.

Four handovers that deserve your attention first

Qualification to contract: conditions must become clauses

Qualification often ends in a conditional approval. The site passed the audit but the process capability study on a critical characteristic was marginal, or the supplier’s certification expires in five months. Those conditions are the most valuable output of qualification, and they are the easiest to lose. The fix is mechanical: every condition should become either a contract clause, a monitored KPI, or a dated follow-up task. If it is none of these, it will not survive the award.

Contract to performance: one definition, not two

This is where most programmes quietly break. The contract says 97% OTIF. The scorecard also says OTIF. But the contract measures against the requested date and the scorecard against the confirmed date, or the contract counts PPM at goods receipt while quality counts it at the line. Both numbers are correct and they will never agree. Because ISO 9001 clause 8.4.3 already requires you to tell the supplier how its performance will be monitored, the contract is the natural place to fix the definition once. The scorecard should inherit it, not reinterpret it.

Performance to CAPA: every threshold needs a route

IATF 16949 clause 8.4.2.4 names minimum monitoring indicators: delivered product conformity, customer disruptions at the receiving plant, delivery schedule performance and premium freight occurrences. Measuring them is the easy part. The handover question is what happens when one crosses a limit. If a breach sits on a dashboard until the next quarterly review, the scorecard is only reporting the problem. A good handover opens a supplier corrective action with a named owner, links it to the metric and the clause it breaches, and closes it only when later data confirms the effect.

CAPA and performance to renewal: the history must be in the room

Renewal is where the lifecycle is supposed to loop back to sourcing. It frequently becomes a fresh negotiation, run by someone who was not involved in the previous term, looking at price and volume. The scorecard trend, the CAPA record and the risk changes over the contract period are the strongest negotiating material a buyer has. They are only in the room if the renewal stage receives them automatically. The same applies at exit: ISO 9001 asks you to retain documented information of evaluations and resulting actions, and a clean audit trail is what lets you answer a question about a supplier you stopped using two years ago.

A handover audit you can run in an afternoon

You do not need a transformation programme to find out where your lifecycle leaks. Pick three suppliers: one onboarded in the last six months, one mid-contract, and one approaching renewal. For each of the seven handovers in the table, ask three questions.

  1. Does the object arrive, or is it re-keyed? If someone copies KPI targets from a contract PDF into a spreadsheet, the handover exists only as long as that person does.
  2. Is there a named owner on both sides? A handover with a sender and no receiver is a filing exercise.
  3. Can you trace it backwards? Start from an open CAPA and try to reach the contract clause, the qualification record and the original sourcing commitment. Count the systems and the people you had to ask.

Score each handover 0 (missing), 1 (manual) or 2 (connected and traceable). This is a diagnostic, not a benchmark, so the total matters less than the pattern. Most teams find one or two joins scoring zero, and those are almost always the ones where different functions own the stages on either side.

Better questions to ask a supplier lifecycle management vendor

Swap the module checklist for handover demonstrations. Ask the vendor to show you, live, with their own demo data:

  • A qualification condition that reappears as a tracked KPI or task after award.
  • A contract SLA and the scorecard metric that inherits its definition and target.
  • A threshold breach that opens a CAPA linked to both the metric and the clause.
  • A CAPA closed only after subsequent performance data confirmed the fix.
  • A renewal view that shows the full performance, risk and CAPA history for the term.
  • A backwards trace from any CAPA to the original sourcing event.

If the vendor offers AI across these steps, ask what it reads, what it proposes, and who approves before anything reaches a supplier. Our guide on how to compare AI features in SRM software sets out those questions in more detail.

How EvaluationsHub, InitiativesHub and Eva AI close the loop

We built our two products around the handovers, because that is where supplier data and accountability most often go missing.

InitiativesHub covers the execution side of the lifecycle: intake and needs capture, RFx (RFI, RFQ, RFP), supplier qualification, awarding and negotiation, and contract management with SLAs and KPIs mapped to the clauses they come from and deviation tracking. It ends with supplier onboarding and a handover to EvaluationsHub, so the obligations agreed in the contract arrive as the starting configuration for performance measurement rather than as a PDF.

EvaluationsHub takes over from there: weighted performance scorecards, supplier risk, ESG and CSRD data, CAPA, QBR management, a two-way supplier portal, and reporting with a full audit trail. Together the two cover the full supplier lifecycle, with renewal decisions drawing on the history EvaluationsHub has kept.

Eva AI sits on top of both and is designed to watch the contract-to-performance join in particular. It reads contract KPI obligations, compares them against live scorecard data, and proposes a CAPA with its reasoning when a deviation crosses a threshold you have defined. It is also designed to monitor risk signals against your acceptance frame and to recommend compliance workflows linked to the relevant clause. Every proposed action is held for human approval, with one-click approve, edit or dismiss, nothing goes to a supplier without sign-off, and each AI decision is logged in an immutable, exportable audit log.

If you want to see a handover trace on your own supplier scenario, book a demo.

Frequently asked questions

What is supplier lifecycle management?

Supplier lifecycle management (SLM) is the end-to-end management of every supplier from the first internal need, through sourcing, qualification, contract, onboarding, performance monitoring and development, to renewal or exit. Its purpose is to keep one continuous supplier record, with obligations and accountability carried from stage to stage.

What is the difference between SLM, SRM and SPM?

SPM measures supplier performance through KPIs and scorecards. SRM manages the relationship, usually with extra depth for strategic suppliers. SLM is the widest scope: it covers every stage and every supplier, and it contains both SPM and SRM.

Where do supplier lifecycle programmes usually fail?

Most failures happen between stages rather than inside them. The most common are qualification conditions that never reach the contract, contract KPIs defined differently on the scorecard, threshold breaches with no route into corrective action, and renewals decided without the performance history.

Does ISO 9001 require supplier lifecycle management?

ISO 9001:2015 does not use the term. Clause 8.4 does require criteria for the evaluation, selection, monitoring of performance and re-evaluation of external providers, retained documented information of those activities and resulting actions, and communication to suppliers of how their performance will be monitored. A connected lifecycle is a practical way to meet those requirements consistently.

By Prof. Dr. Bert Paesbrugghe, founder of EvaluationsHub and associate professor at IÉSEG School of Management.

Published by EvaluationsHub. We make one of the products discussed below, so we have described every other vendor using their own public pages and linked each claim. Vendor information last reviewed 29 September 2026.

Every supplier management vendor now has an AI story. Some call it an assistant, some a copilot, some a fleet of agents. The demos look alike: a chat box, a summary of a supplier, a risk alert that appears on cue. The differences that matter for a supplier quality or vendor management team sit underneath, and they rarely show up in a standard demo script.

This guide gives you a way to compare them. It is written for people who have to live with the result: the supplier quality engineer who owns the CAPA, the category manager who owns the QBR, and the procurement lead who has to explain an AI decision to an auditor.

Why comparing AI features is harder than it looks

Buyers are clearly interested and still cautious. In a Gartner survey of 101 chief procurement officers run in January and February 2026, only 36% said they were very confident in their ability to redesign roles and processes around AI. The Hackett Group’s 2026 Procurement Key Issues study found that 43% of organisations are actively pursuing AI deployment, but only 12% report large-scale implementation, and that 69% access AI through capabilities embedded in their existing procurement platforms.

That last figure is the important one. Most teams will not buy AI on its own. They will get whatever AI comes with the supplier platform they choose. So the AI question is really a platform question, and it deserves the same rigour as the rest of your evaluation.

Three things make it hard:

  • The same words mean different things. “Agent” can mean a model that drafts an email or one that changes supplier master data without asking.
  • Availability varies. Several capabilities announced in 2025 and 2026 are in beta, rolling out, or planned for a later release. Vendors usually say so on their own pages, but not in the demo.
  • AI is only as good as the supplier data under it. A brilliant model reading a stale supplier record produces a confident, wrong answer.

Compare the loop, not the model

Almost every vendor builds on one of a handful of large language models. Comparing model names tells you little. What differs is the loop the AI sits in. For supplier management, that loop has five steps, and you can compare every vendor on each one:

  1. Read. Which of your data can the AI actually see? Scorecards, contracts, CAPA history, supplier portal submissions, external risk feeds, ERP transactions?
  2. Reason. Does it show why it reached a conclusion, with the data points and sources behind it?
  3. Recommend. What does it propose: a summary, a score, a corrective action, a sourcing event, a message to a supplier?
  4. Act. What happens next? Does a person approve, edit or dismiss, or does the AI proceed on its own? Which actions can it never take alone?
  5. Record. Is every AI output, approval and outcome logged in a way you could export and hand to an auditor?

A capability that is strong at step 3 and silent on steps 4 and 5 is a nice demo. A capability that is solid across all five is something you can put into a regulated supplier quality process.

Eight questions to ask every vendor

Use these in the RFP and again, live, in the demo. They are deliberately practical.

1. What supplier data does the AI read, and how fresh is it?

Ask for a list of the objects the AI can access. The most useful supplier AI connects things that normally live apart: a contractual KPI in one place and the measured OTIF or PPM in another. If the AI only reads documents you upload into a chat, it is a writing aid, which is useful but different.

2. Can you show me the reasoning behind one recommendation?

Pick a recommendation in the demo and ask to see exactly which data triggered it. You want to see the threshold, the measured values and the time window, not a paragraph of fluent prose.

3. What can it do without a human, and can I switch that off?

This is the single most important question. Ask for the list of actions the AI can take autonomously, the list it can only propose, and whether you can configure the boundary per action type. Supplier-facing communications, awards and changes to bank details deserve particular attention.

4. Where is the audit trail, and can I export it?

For teams working under ISO 9001, IATF 16949, GMP or medical device rules, an AI-proposed corrective action is still a corrective action. You need to show who approved it, when, and on what evidence.

5. Is my data used to train models, and where is it processed?

Get the answer in writing, in the contract, not just on a web page. Ask separately about the vendor’s own models and any third-party model providers they use.

6. What is generally available today, and what is on the roadmap?

Ask the vendor to mark each capability you saw as generally available, beta, or planned, with dates. There is nothing wrong with a roadmap. There is something wrong with buying one by accident.

7. What happens when the AI is wrong?

Ask to see a dismissed recommendation. Does the dismissal get recorded? Does the system learn from corrections? Can you tune thresholds so the queue does not fill with noise?

8. Can you run it on our data before we sign?

A demo on the vendor’s sample data proves the interface works. A short session on a slice of your own supplier data proves the AI works for you.

What leading vendors say their AI does

The table below summarises how each vendor describes its own AI for supplier management, using its public pages as of 29 September 2026. It is a starting point for your own questions, not a ranking, and features change quickly. Where a vendor’s page did not address a topic, we say “not stated on the page reviewed”. That does not mean the capability is absent, only that you should ask.

Supplier management AI as described by each vendor (public sources, reviewed 29 September 2026)
Vendor AI layer Supplier management examples, in the vendor’s framing Oversight and data statements published A genuine strength
SAP (Ariba) Joule, Supplier Management Assistant Sanctions screening, financial health checks and risk evaluations; supplier classification; onboarding data enrichment; “corrective action plans before performance risk materializes” Not stated on the supplier management page reviewed; see SAP’s general AI ethics principles Built on a long-established supplier lifecycle module and third-party data enrichment
Coupa Navi agents Supplier Discovery Agent and Supplier Assistance Agent (announced November 2025) Not stated in the announcement reviewed Community data from a very large buyer and supplier network
Ivalua IVA Validating documents and enriching profiles at onboarding; keeping risk and performance scores current “Every AI action has a person accountable”; continuous audit trails; IVA inherits user permissions; “never uses your data to train LLMs” Among the clearest published governance commitments
JAGGAER JAI Supplier self-service onboarding and cited answers across procurement data “JAI suggests. You decide. Always.” No customer data used for model training; data processed in the customer’s selected region Explicit data residency statement and source citations on answers
Oracle Fusion Procurement Supplier Qualification Workspace (agentic app) AI summary of qualification compliance; flags missing or adverse qualifications; currently up to 500 strategic suppliers across three tiers “Review AI recommended priority actions for accuracy before applying” Precise release documentation, including stated limits
Gatekeeper Gatekeeper AI and agents SLA Compliance Check Agent; Bank Details Validator Agent; claims 50+ agents Not stated in detail on the page reviewed A wide catalogue of narrow agents on one vendor and contract record
Kodiak Hub AI across the platform AI-enhanced insights for supplier performance, risk forecasting and anomaly detection; document extraction ISO 27001 stated; AI oversight not stated on the page reviewed AI inside a full SRM loop of ratings, goals and actions
Prewave AI-based risk alerts Prioritising risks by AI-driven impact, probability and relevance; deep-tier mapping Not stated on the page reviewed External risk sensing across languages and supply tiers

Two patterns stand out. First, governance disclosure is uneven. A few vendors publish specific commitments on human accountability, training data and residency; many do not address them on their AI pages at all. Second, most published examples cluster around risk sensing, onboarding documents and sourcing. Fewer vendors describe AI that connects what a supplier promised in a contract with how that supplier is actually performing, which is where supplier quality teams spend most of their week.

Suites, specialists and risk platforms: which kind of AI fits you

A source-to-pay suite’s AI is a strong fit if you already run that suite, your priority is transactional efficiency across sourcing, contracts and payables, and you have an enterprise agreement in place. The AI benefits from seeing spend and transaction data in one system.

A risk intelligence platform’s AI is a strong fit if your main exposure is external: disruption, sanctions, adverse media or deep-tier visibility. It watches the world outside your supply base very well.

A supplier performance and lifecycle specialist’s AI is a strong fit if your pain sits in the relationship itself: scorecards, corrective actions, QBRs, contractual KPIs, supplier development, and the evidence trail auditors ask for. Here the AI can be very close to the data that quality and vendor management teams work with every day.

Many large organisations will combine a suite with a specialist. The limits of S2P suites for supplier relationship work and the ERP versus specialised SPM question are covered in separate articles.

Where EvaluationsHub, InitiativesHub and Eva AI fit

We are a specialist in supplier performance, and we built our AI around the loop described above rather than around a chat window. Three products work on one supplier data model:

  • EvaluationsHub covers supplier performance and risk: weighted supplier scorecards per segment, risk and ESG data collection, corrective actions (CAPA), QBR management and a two-way supplier portal.
  • InitiativesHub covers execution: intake, RFx, supplier qualification, awarding, contract management with SLAs and KPIs mapped to clauses, and onboarding that hands over to EvaluationsHub when it is complete. Together, the two cover the full supplier lifecycle.
  • Eva AI is the AI layer on top. It is designed to do three things.

Contract and performance cross-check. Eva reads the KPI obligations in your contracts and compares them with live scorecard data. When a deviation crosses a threshold you define, it proposes a corrective action with its reasoning attached. For example: a contract requires 97% OTIF, the 30-day average is 88.4%, and the gap has exceeded your 5-point threshold for three consecutive weeks.

Risk and compliance monitoring. Eva watches risk signals across the supplier portfolio against your acceptance frame and proposes the right compliance workflow, linked to the relevant contract clause.

Cost reduction intelligence. Eva looks for consolidation opportunities, suppliers ready for renegotiation based on performance, and pricing anomalies, and proposes structured cost reduction projects in InitiativesHub.

On the questions above, our answers are simple. Eva recommends and you decide: every action is held for human review, with approve, edit or dismiss in one click. No supplier-facing action happens without explicit approval. Confidence thresholds are configurable per action type. Every AI recommendation, approval and outcome goes into an immutable, exportable audit trail. The platform is ISO 27001 certified and hosted in the EU.

We are not the right choice for everything. If you want one vendor for requisitions, invoices and payments, a suite will serve you better. If deep-tier news monitoring in dozens of languages is your main need, a dedicated risk intelligence platform goes further. Our focus is the performance, risk and improvement loop with your suppliers, and the AI that makes that loop faster without taking the decision away from your team.

A note on regulation

Human oversight is becoming a regulatory expectation, not only good practice. Under the EU AI Act, high-risk AI systems must be designed so that people can oversee them effectively. In May 2026 the Council and Parliament agreed to move the application dates for high-risk obligations to 2 December 2027 for stand-alone high-risk systems and 2 August 2028 for those embedded in products. Most supplier management uses are unlikely to fall in the high-risk categories, but the oversight principle is a sensible benchmark for any AI that proposes actions affecting suppliers. Our EU AI Act guide for procurement goes further; check any specific obligation with your legal team.

What this comparison cannot tell you

We compared public statements, not live systems. We did not test any vendor’s AI on real data, pricing for AI add-ons is rarely published, and some capabilities may be further along or further behind than a web page suggests. Ask each vendor, including us, to show you the loop working on your own suppliers.

Frequently asked questions

What is the most important AI feature in SRM software?

The ability to connect data that normally sits apart, such as contract obligations and measured performance, and to turn a deviation into a proposed action with clear reasoning. Summaries and chat are helpful, but the value is in the action loop.

Should AI in supplier management act without human approval?

For low-risk, reversible, internal tasks, limited autonomy can be reasonable. For supplier-facing communications, awards, corrective actions and any change to supplier bank details, human approval with an audit trail is the safer design and the one auditors will expect.

How do I check whether a vendor’s AI feature is actually available?

Ask the vendor to label each capability as generally available, beta or planned, with dates, and put that list in the contract schedule. Many vendors state availability on their own release notes or press releases, so check those too.

Do I need clean supplier data before AI is useful?

You need reasonably current core data: supplier records, a scorecard with defined KPIs, and your key contract terms. You do not need perfection. A good platform will show you where data gaps are weakening its recommendations.

If you want to see the loop on your own supplier data, book a demo and bring one supplier you are worried about.

For a fuller treatment of what agents should and should not do, read our guides on AI agents in procurement and AI agents in supplier quality.

By Prof. Dr. Bert Paesbrugghe, founder of EvaluationsHub and associate professor at IÉSEG School of Management.

A kitchen can have a superb fishmonger and still run out of fish on a Saturday night. I learned that as a chef long before I studied buyers for a living. The fishmonger was financially sound, delivered great product and never once missed an invoice. The problem sat elsewhere: one boat, one road, one driver. When any of the three failed, the supplier was fine and my dining room was not.

Procurement is now discovering the same lesson at scale. ProcureAbility’s 2026 CPO Benchmark Study, published on 9 September 2026 and based on 160 senior procurement leaders at large enterprises across 21 industries, describes what it calls a shift in procurement’s risk focus from supplier health to supply continuity. Read that sentence twice. For years we asked whether the supplier is a sound business. Increasingly we are asking whether the thing we need will actually arrive.

The numbers behind that shift are worth sitting with. In the same study, 62% of respondents cite geopolitical disruption as a primary risk and 55% cite logistics disruption. Yet only 6% say they have predictive or real-time monitoring tools, while 62% still rely on manual or periodic risk assessment. So buyers worry about continuity more than anything, and most of them check on it the way a chef checks a walk-in fridge: by opening the door now and then and hoping.

Why this is a relationship question, not only a tooling question

When I interviewed buyers for my research, continuity came up again and again, often before price did. The sentence behind it was rarely “we want the cheapest supplier” and far more often “I never want to explain to my board why the line stopped”. Business continuity is the buyer’s quiet top priority, and it shapes how they judge every supplier interaction, whether or not they say so.

Here is the part that interests me most. The early warning signs of a continuity problem usually sit with the supplier long before they sit in any dashboard. A second-tier component maker is struggling. A port is congested. A key engineer has left. The supplier often knows first. Whether the buyer hears about it depends on something no monitoring tool can buy: the quality of the relationship.

That is where balance enters. If a supplier expects to be punished for bad news, bad news arrives late. If a buyer never explains which parts of the supply are truly critical, the supplier cannot prioritise them. Both sides are guessing, and the guessing happens in the space where continuity is won or lost.

Three habits that build continuity before the crisis

Say what “critical” means. Most buyers have a mental list of the three or four things that would stop the business. Few suppliers have ever seen that list. Share it. A supplier who knows that one item out of forty matters enormously will treat it differently on a bad week. This is mise en place for a relationship: everything in its place before service starts.

Make bad news cheap. Ask suppliers, in a regular conversation and not only in a quarterly review, what worries them about the next ninety days. Then respond to the answer with help, not a penalty clause. A supplier who is thanked for an early warning will send the next one earlier.

Swap the snapshot for a rhythm. A yearly risk assessment is a photograph of a river. Continuity moves. Even without expensive tooling, a light monthly check-in on the handful of critical suppliers gives you more signal than a thick annual questionnaire. Technology can then amplify that rhythm, but it should follow a logic you have already agreed on.

The balance point

There is a temptation, when risk headlines pile up, to tighten control: more audits, more clauses, more reporting demands. Some of that is sensible. Yet a supplier buried in compliance requests has less attention left for your actual supply, and the relationship becomes a paperwork exercise that produces reassuring documents and thin resilience.

The alternative is equilibrium. The buyer is clear about what matters and generous with context. The supplier is honest about risk and early with news. Neither side wins at the other’s expense, because the outcome both want, goods arriving on time, is shared.

I explore this buyer-side perspective, including what buyers told me they wish their suppliers understood, in my book The Buyer’s Balance: What your customers want to share with you (Owl Press, 2025, ISBN 9789464778908). More at evaluationshub.com/book.

So here is my question for this week. If your most critical supplier had a problem today, how many days would pass before you heard about it, and from whom?

Source: ProcureAbility, 2026 CPO Benchmark Study, press release of 9 September 2026 (160 senior procurement leaders, 21 industries).